
+- Hack Forums (https://hackforums.net)
+-- Forum: Hacks, Exploits, and Various Discussions (https://hackforums.net/forumdisplay.php?fid=45)
+--- Forum: Grayhat • Purple Team • Hybrid Security (https://hackforums.net/forumdisplay.php?fid=449)
+---- Forum: Website Hacking (https://hackforums.net/forumdisplay.php?fid=43)
+---- Thread: [VPN USERS: ]>_ Your VPN could be Leaking your REAL IP Address_[/How to fix] (/showthread.php?tid=4682819)
[VPN USERS: ]>_ Your VPN could be Leaking your REAL IP Address_[/How to fix] - mObiIe - Feb 12, 2015

A new security flaw can reveal your real IP address to prying eyes, even if you're using a VPN, and it's easy to exploit. Here's how it works, and what you can do about it. A recently discovered security flaw allows remote sites to take advantage of WebRTC (Web Real Time Communication, a feature built in to most browsers.
A few lines of code is all it takes to remove the location protection you get from using a VPN, and figure out where you're actually located and who your internet service provider really is (who can then tie your address back to who you are specifically.) While the vulnerability is primarily browser-based right now, any application that can render web pages (and uses WebRTC) is affected, meaning anyone who wants to can see past your VPN to where you really are and who you really are. Advertisers, data brokers, and governments can use it to peek through your VPN to find out where your connection is really coming from.
How Can I Check If My VPN Is Affected?
Firefox and Chrome have implemented WebRTC that allow requests to STUN servers be made that will return the local and public IP addresses for the user. These request results are available to javascript, so you can now obtain a users local and public IP addresses in javascript. This demo is an example implementation of that.
Additionally, these STUN requests are made outside of the normal XMLHttpRequest procedure, so they are not visible in the developer console or able to be blocked by plugins such as AdBlockPlus or Ghostery. This makes these types of requests available for online tracking if an advertiser sets up a STUN server with a wildcard domain.
To see if your VPN is affected:
1.) Visit:
Quote:http://whatismyipaddress.com/
and jot down your actual ISP-provided IP address.
2.) Log in to your VPN, choose an exit server in another country (or use whichever exit server you prefer) and verify you're connected.
3.) Go back to What Is My IP Address and check your IP address again. You should see a new address, one that corresponds with your VPN and the country you selected.
4.) Visit Roseler's WebRTC test page
Quote:https://diafygi.github.io/webrtc-ips/
and note the IP address displayed on the page.
[img]http://torrentfreak.com/images/nkoreaip.png[/img]
If both tools show your VPN's IP address, then you're in the clear. However, if What Is My IP Address shows your VPN and the WebRTC test shows your normal IP address, then your browser is leaking your ISP-provided address to the world.
The Easy Way: Disable WebRTC In Your Browser.
Chrome, Firefox, and Opera (and browsers based on them) generally have WebRTC enabled by default. Safari and Internet Explorer don't, and thus aren't affected (unless you've specifically enabled WebRTC.) Either way, if the test above worked in your browser, you're affected. You can always switch to a browser that doesn't have WebRTC enabled, but since most of us like the browsers we use, here's what to do:
Chrome and Opera:
Install RTC Block or ScriptSafe extension from the Chrome Web Store. It's overkill, but it'll disable WebRTC in your browser.
Quote:https://chrome.google.com/webstore/detail/webrtc-block/nphkkbaidamjmhfanlpblblcadhfbkdm?hl=en
Quote:https://chrome.google.com/webstore/detail/scriptsafe/oiigbmnaadbkfbmpbfijlflahbdbdgdf?hl=en
Firefox: You have two options. You can install the Disable WebRTC addon from Mozilla Add-ons
Quote:https://addons.mozilla.org/en-US/firefox/addon/happy-bonobo-disable-webrtc/
or disable WebRTC directly by opening a tab and going to
PHP Code
<?php
about:config
in the address bar. Find and set the
PHP Code
<?php
media.peerconnection.enabled
setting to false.
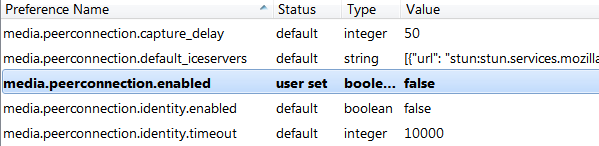
To be sure WebRTC is disabled go to:
Quote:https://www.browserleaks.com/webrtcand you should see something like this, if your good.

Otherwise you will see this:

I know a lot of you use VPN software and probably don't know about this so I hope it was helpful. Got to stay anonymous if you are hacking websites, 👍 🤝
SOURCES:
Spoiler (Click to View)
PHP Code
<?php
http://torrentfreak.com/huge-security-flaw-leaks-vpn-users-real-ip-addresses-150130/
PHP Code
<?php
http://lifehacker.com/how-to-see-if-your-vpn-is-leaking-your-ip-address-and-1685180082
PHP Code
<?php
https://www.browserleaks.com/webrtc
* - Fʀᴀɴᴋɪᴇ - Feb 12, 2015
I believe this was posted about earlier but for those that were not able to see it I am sure they will thank you.
* - Zealot - Feb 12, 2015
I did not know this at all, thanks man.
* - Suits - Feb 12, 2015
A++ man. Great info on taking proper precautions with VPNs.
* - Inkling - Feb 12, 2015
Check out my signature to abuse this bug with my IP Logger. :)
* - robby_j - Feb 12, 2015
This is false. Only proxy servers would be affected by this.
* - Scy7e - Feb 12, 2015
(Feb 12, 2015 08:26 PM)cl0ck Wrote: This is false. Only proxy servers would be affected by this.
This is not false at all. It definitely is able to get your real IP even from behind a Tor as long as webRTC isn't disabled. I've used this exploit for quite a while now and it has worked more often than not.
* - EPIXIA - Feb 12, 2015
(Feb 12, 2015 08:33 PM)Scy7e Wrote: It definitely is able to get your real IP even from behind a Tor as long as webRTC isn't disabled.webRTC is disabled by default in Tor already
(Feb 12, 2015 07:03 PM)Inkling Wrote: Check out my signature to abuse this bug with my IP Logger. :)This is not a bug, it is by design
* - Scy7e - Feb 12, 2015
(Feb 12, 2015 08:51 PM)EPIXIA Wrote: webRTC is disabled by default in Tor already
Yes, on the official client, though I don't see many reasons why someone would use anything else. Either way, works almost 10/10 on VPN.
* - Jcgob - Feb 12, 2015
I think Internet Explore won this battle ;)
* - frank3nstien - Feb 13, 2015
Thank you for these TUT, I will Check it now with my Premium VPN 😅
* - robby_j - Feb 13, 2015
(Feb 12, 2015 08:33 PM)Scy7e Wrote: This is not false at all. It definitely is able to get your real IP even from behind a Tor as long as webRTC isn't disabled. I've used this exploit for quite a while now and it has worked more often than not.Tor isn't a VPN. Free VPN's even block this.
* - Scy7e - Feb 13, 2015
(Feb 13, 2015 12:19 AM)cl0ck Wrote: Tor isn't a VPN. Free VPN's even block this.
I never said Tor is a VPN. I don't know what kind of point you're trying to make, the fact is this exploit does work as long as webRTC isn't disabled, be it a VPN or Tor. Not all VPN's block this and neither does Tor in some edge cases.
* - Frankstare - Feb 13, 2015
Thanks for posting about this, wouldn't have known if I didn't see this.
* - Chr0nicHax - Feb 13, 2015
http://nexon-nx.ml/iplogger/js/x01.js
JS_Kryptik.ALB trojan
this is the only source on that page:
<script src="js/x01.js"></script>