
+- Hack Forums (https://hackforums.net)
+-- Forum: Hacks, Exploits, and Various Discussions (https://hackforums.net/forumdisplay.php?fid=45)
+--- Forum: Whitehat • Blue Team • Defensive Security (https://hackforums.net/forumdisplay.php?fid=448)
+---- Forum: White Hat Hacking (https://hackforums.net/forumdisplay.php?fid=400)
+---- Thread: [Legends] Severe Veritas Vulnerability Allows Attackers to Run Malicious Code (/showthread.php?tid=6294056)
Severe Veritas Vulnerability Allows Attackers to Run Malicious Code - JoseMar - Mar 11, 2025
Severe Veritas Vulnerability Allows Attackers
to Run Malicious Code (CVE-2025-27816)
to Run Malicious Code (CVE-2025-27816)
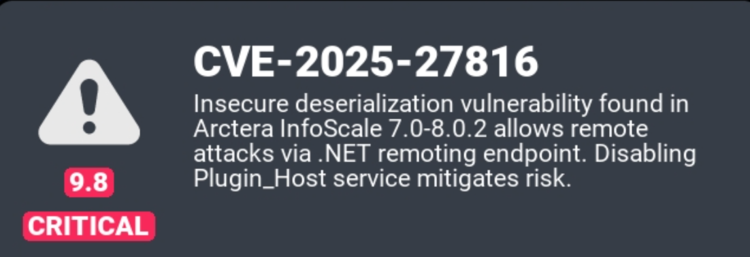
A serious security blemish in Veritas’ Arctera InfoScale has put endeavor frameworks at risk, permitting aggressors to execute code (RCE) remotely and pick up full control over-influenced servers. This helplessness highlights continuous security challenges in calamity recuperation (DR) infrastructure, where versatility is basic; however, vulnerabilities can lead to disastrous failures.
What’s the Issue?
Tracked as CVE-2025-27816 with a CVSS score of 9.8 (Basic), this blemish dwells in the Windows Plugin_Host benefit, a center component utilized when setting up catastrophe recuperation (DR) setups through InfoScale’s DR wizard.
Attackers can bypass confirmation and execute self-assertive code by sending uncommonly created .NET remoting messages to defenseless servers.
Since the benefit runs by default on all Windows servers with Arctera InfoScale, it presents a major assault vector, particularly in organizations depending on robotized DR setups.
If abused, this powerlessness awards SYSTEM-level benefits, giving an aggressor full control over the system.
Who’s Affected?
Veritas has affirmed that the taking after adaptations are impacted:
- Arctera InfoScale Endeavor for Windows forms 7.0 – 8.0.2
- Legacy (unsupported) forms are too vulnerable.
Veritas has not, however, discharged a fix, but you can quickly diminish hazard by:
- Crippling the Plugin_Host benefit overall cluster nodes.
- Exchanging to manual DR arrangement, maintaining a strategic distance from the defenseless component.
- Taking after Veritas’ rules to anticipate inadvertent reactivation of Plugin_Host.
Sina Kheirkhah from Watchtower Labs, who found the blemish, warns:
- “Insecure deserialization remains a major security hazard. Designers frequently belittle how simple it is to weaponize .NET contraption chains.”
Act Presently Sometime recently Misuses Surface
With a CVSS 9.8 seriousness rating, this is a simple target for assailants, requiring no uncommon get-to or insider benefits. Organizations must act rapidly to secure their frameworks by crippling powerless administrations and examining their catastrophe recuperation configurations.
Patching alone isn’t enough; proactive defense is key in a period where aggressors quickly weaponize vulnerabilities like this.
Don´t forget to update and stay safe!🕵️
Additional sources to explore: You can also search directly by CVE on Google for more information:
- https://nvd.nist.gov/vuln/detail/CVE-2025-27816
- https://cybersecuritynews.com/critical-veritas-vulnerability/