DO NOT DEAL WITH THIS MEMBER
Mar 1, 2026 03:33 PM
(This post was last modified: Mar 5, 2026 03:09 PM by am00.)
Hi everyone!
I'm creating this thread to keep you updated about goahead. cc — a runtime malware scanner I'm building.
The project started because I couldn't find a tool that would actually execute the file across multiple AV engines instead of just doing static scans. So I built one — and I made privacy of your files a core part of it.
I'll be posting changelogs and updates here as development progresses. The platform is not yet public, but it's getting close.
If you have ideas, suggestions, or features you'd like to see in a scanner built by this community for this community — drop them below. I'm reading everything.
# 03.01.26 #
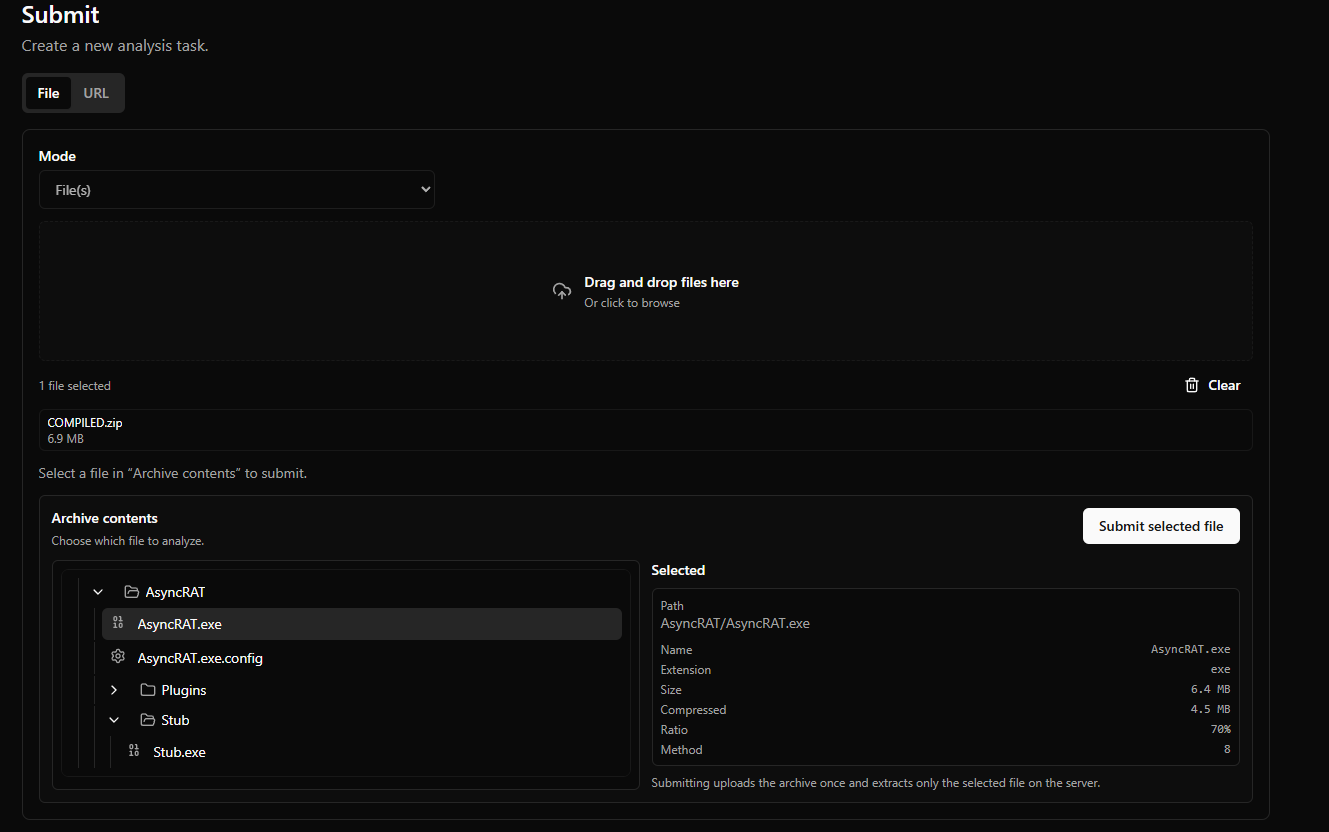
[*] Added content viewer for compressed files (.ZIP, .RAR).
[*] Improvements to the overall user experience.
[*] Added support for .BAT files.
Preview content viewer:
DO NOT DEAL WITH THIS MEMBER
Mar 2, 2026 06:01 PM
(This post was last modified: Mar 3, 2026 05:24 PM by am00.)
# Security Update - 03.02.26
New Features- Scan Sharing System - User configurable. Share analysis results securely with full control over permissions.
- Network Analysis System (TurboFlow) - Advanced real-time network traffic monitoring and suspicious behavior detection.
- Dropped Files Verification - Automatic validation and tracking of removed/dropped files with operation logging.
- Behavioral Analysis Engine - Comprehensive monitoring including:
- Hooking Detection - System call interception tracking
- Process Monitoring - Active process execution analysis
- Threading Analysis - Thread behavior inspection
- Registry Inspection - Windows registry modification tracking
- API Filtering - Advanced API call filtering
- FileSystem Tracking - File system activity monitoring
- Miscellaneous Detection - Additional behavioral flags
Improvements & Fixes- SHA256 Verification Enhanced - Fixed verification against public databases (VirusTotal, MWDB, BAZAAR) with improved accuracy.
- Office Suite Integration - Machines updated with Office Suite for better file analysis. Now supports: .XLS, .XLSX, .DOC, .DOTM, .PPTX
- File Compatibility Fixed - Resolved issues with files not opening correctly. Improved support for PE32+ & .NET assemblies.
Development Roadmap
Planned Initiatives:- Electron-based Application Framework - Development of cross-platform desktop application to extend support across multiple operating systems and devices. This will provide a unified interface and enhanced compatibility beyond current Windows-only deployment.
- Scantime Integration
- Multi-Antivirus Engine Integration - Currently limited to Windows Defender [11] support. Future releases will incorporate integration with enterprise-grade antivirus solutions, including Kaspersky, Norton 360, McAfee, Avast, AVG, Bitdefender, Trend Micro, ESET, G Data, and additional industry-standard engines.
BETA TESTING PHASE - USER REGISTRATION OPENING
We are entering the active beta testing phase and will be opening registration for selected users. During this period, we acknowledge that the platform contains known issues and limitations that we are actively working to resolve.
Important Notice:- This is a pre-release testing phase - expect bugs and incomplete features
- Your participation helps us identify and fix critical issues
- All feedback will be documented and prioritized for upcoming patches
- Stability and performance are core focuses of our development efforts
WORKER DISTRIBUTION & SYSTEM ARCHITECTURE
Worker Distribution Model:
Our platform utilizes a distributed worker-based architecture designed to optimize scan processing and resource utilization across the network:
- Worker Pool Management - Multiple workers are distributed and assigned based on user tier and subscription level. Each worker instance handles dedicated analysis tasks with load balancing to prevent bottlenecks.
- Queue System - Submitted files enter a priority queue system where they are distributed to available workers based on:
- User subscription tier (Premium/Standard/Beta)
- Worker availability and current load
- File analysis complexity and required modules
- Geographic location and latency optimization
- Horizontal Scaling - As demand increases, additional worker instances are provisioned to maintain performance standards. This allows the platform to handle concurrent scans without degradation.
- Worker Communication Protocol - Workers communicate through a centralized message broker, ensuring reliable task distribution and result aggregation back to the user interface.
- Redundancy & Failover - Multiple workers run in parallel for critical analysis tasks, providing redundancy and ensuring service continuity.
Platform Screenshots
Home Dashboard:
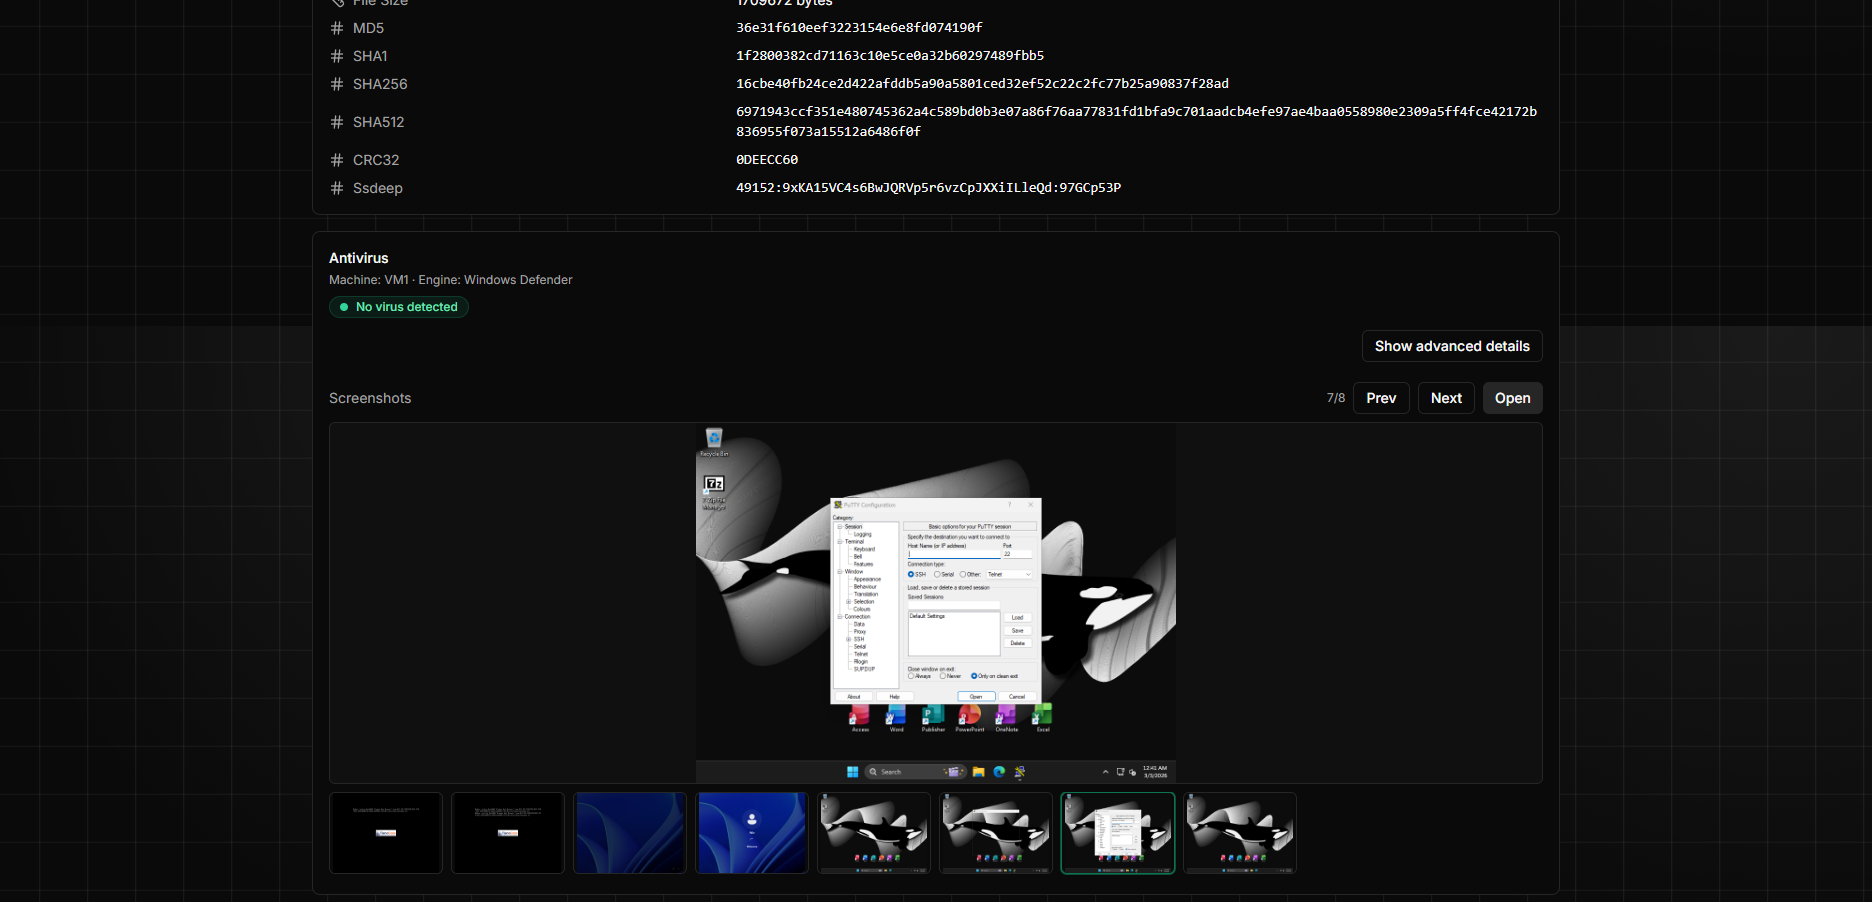 Share Options: 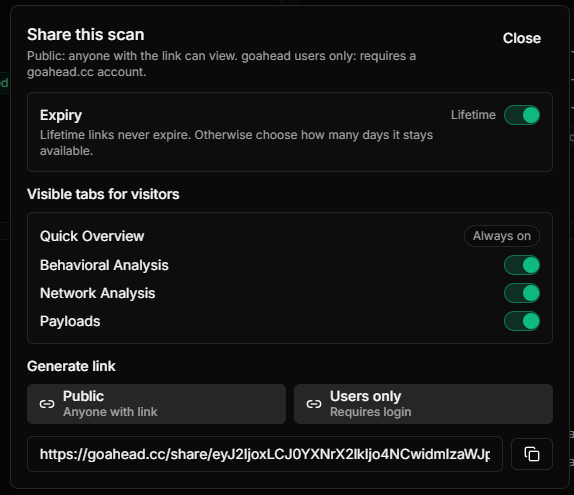 Network Analysis Module: 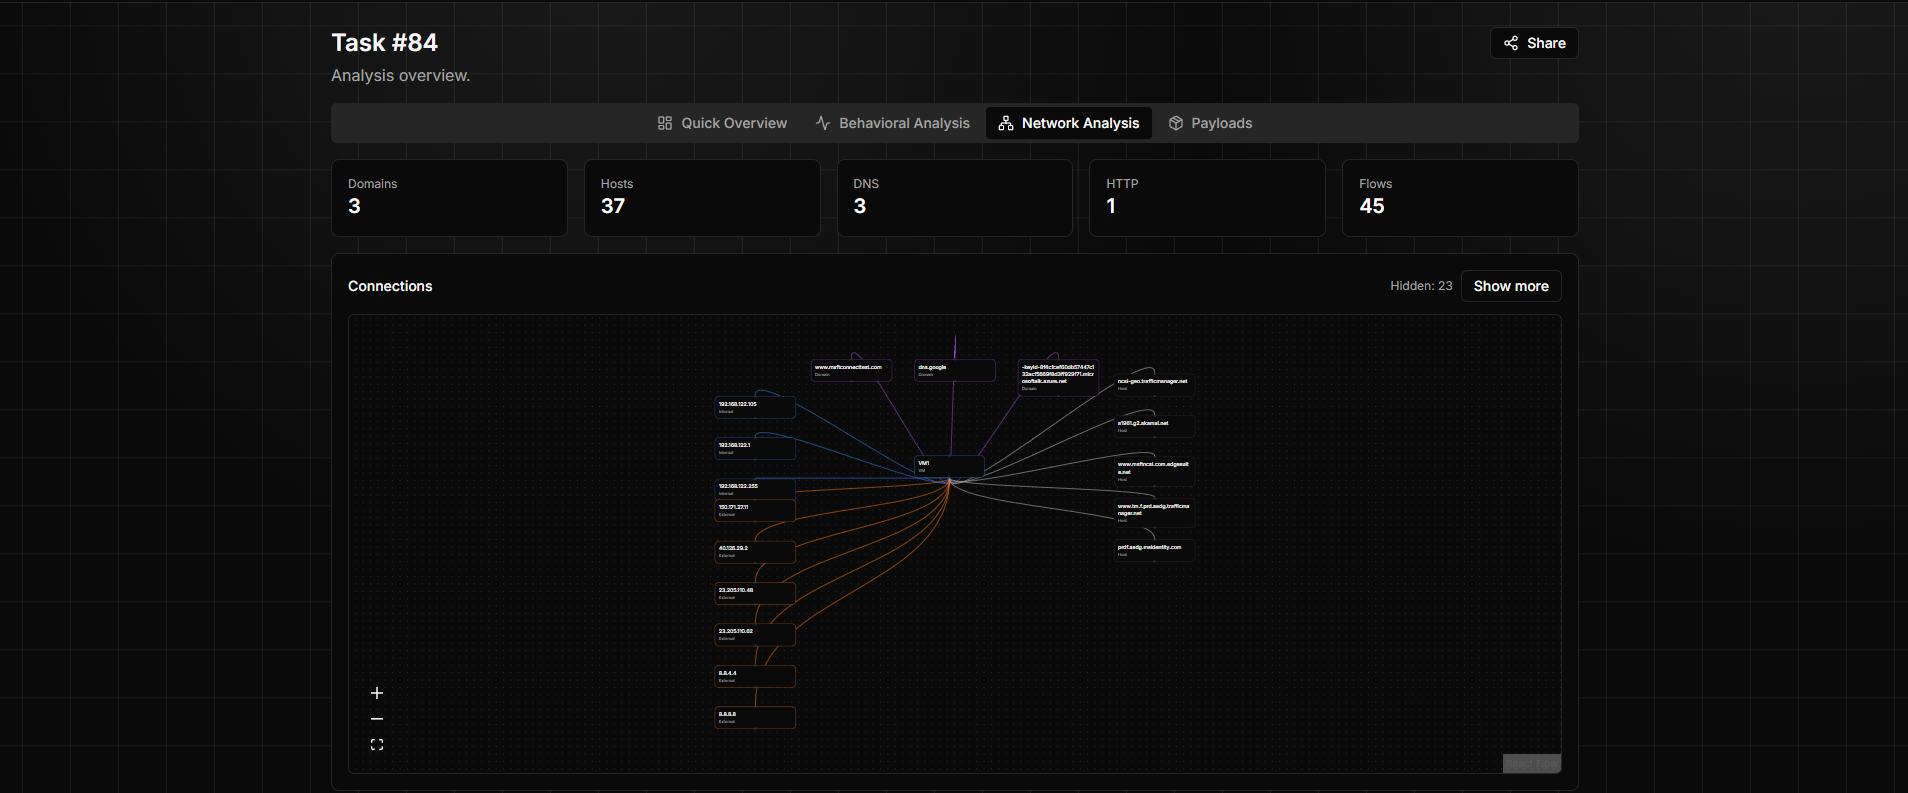 Behavioral Analysis Module: 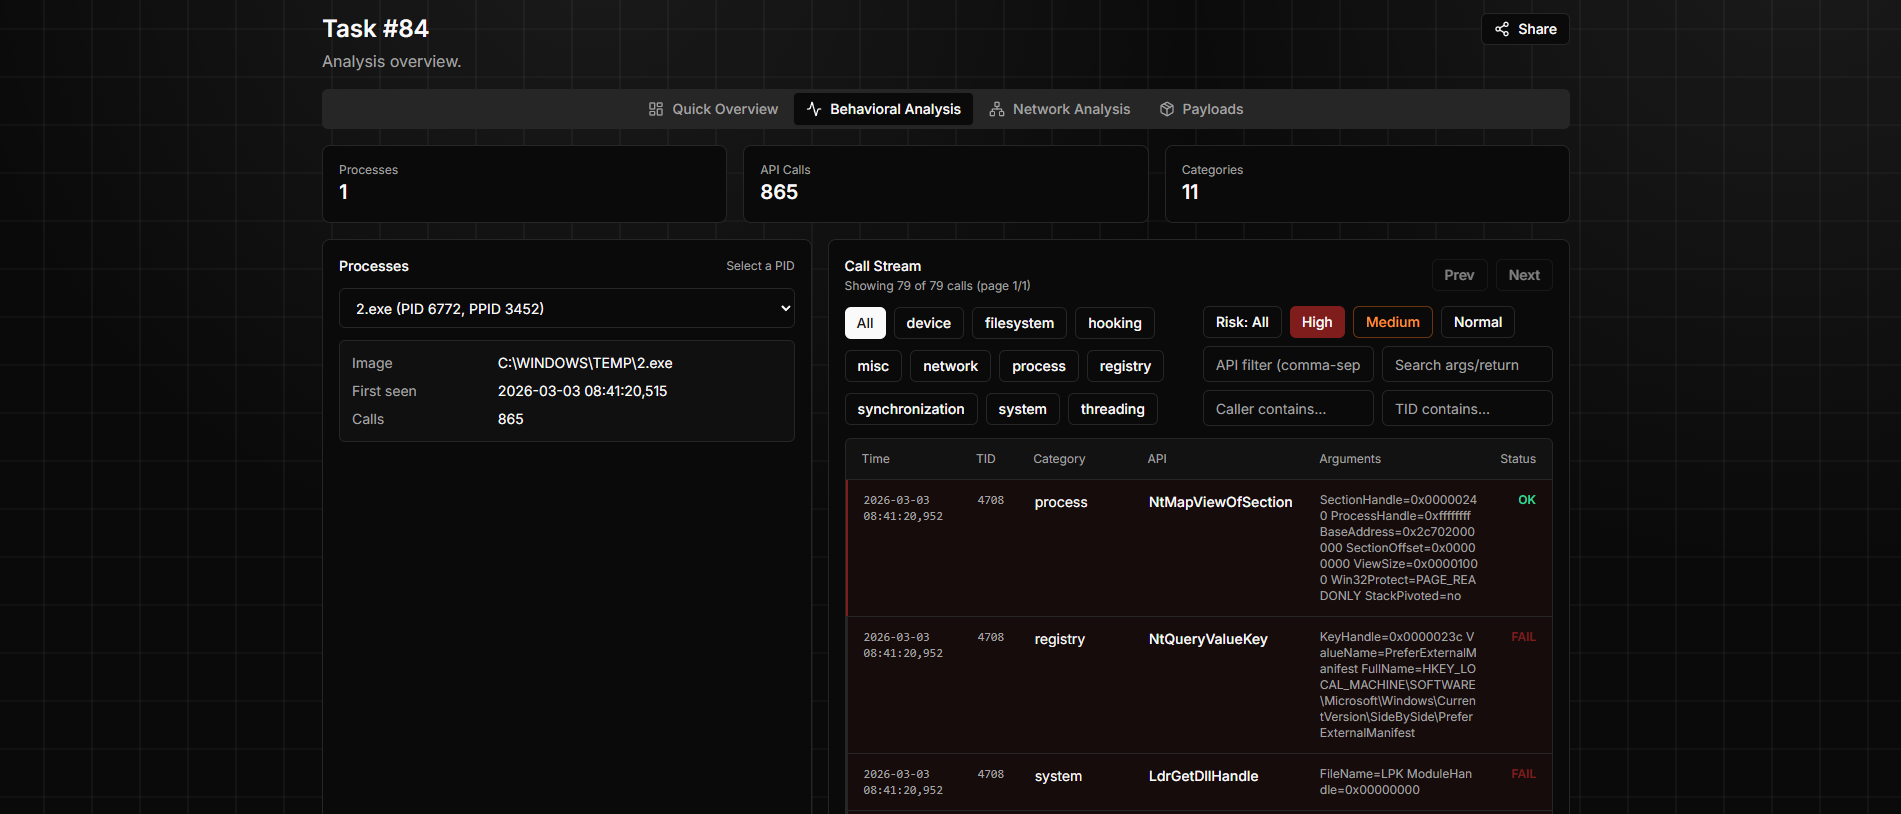
Register now to participate in the beta testing phase and help shape the future of our security platform.
# Security Update - 03.03.26
Improvements & Fixes- Report Generation System - Corrected reports returning only "Unknown" status. Analysis results now properly categorize findings and threat classifications.
- Real-Time Backend Communication - Reports UI updated to communicate with backend in real-time, displaying average waiting time for analysis, current initialization state and progress, and task queue position with estimated completion.
- Screenshot System Optimization - Optimized screenshot capture to exclude BIOS and firmware-level screenshots, focusing only on behavioral evidence within the operating system environment.
- Concurrent Task Limitation - Implemented per-user task queue limitation system:
- Maximum 1 file scan per user simultaneously
- After scan completion (approximately 5 minutes), user can submit next file
- Fair resource distribution across all users
- Recent Tasks Display - Fixed issue where pending tasks were not displayed in Recent tab. All active and pending submissions now properly visible.
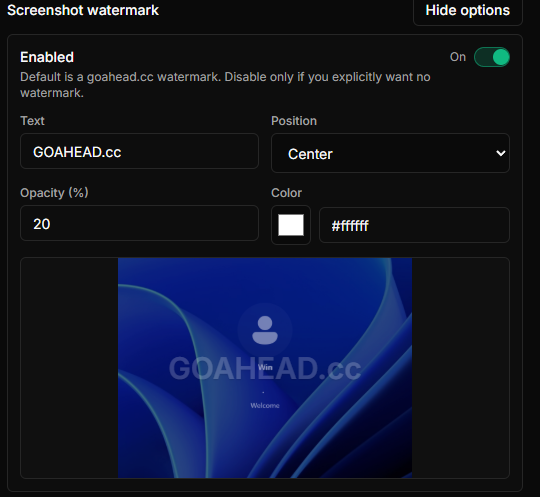
- Screenshot Watermark System - Added customizable watermark feature for all captured screenshots:
- Fully personalizable by user
- Custom text, logos, and styling options
- Currently enabled for all users during testing phase
- File String Extraction - Added feature to extract and retrieve strings from analyzed files with detailed string library analysis. (Only .exe now.)
- Custom String Filtering - Implemented advanced custom filter system allowing users to filter extracted strings by type, length, encoding detection, pattern matching, and entropy analysis.
Known Issues- .BAT/.VBS/.JS script files are not executing correctly within the sandbox environment. Proper execution context and interpreter integration is in development.
Testing Phase Notice:
All implemented features are currently undergoing active testing. While we have thoroughly validated core functionality, minor errors and edge cases may occur. These will be corrected over time as we continue development and receive user feedback.
Scan Example:
https://goahead.cc/share/eyJ2IjoxLCJ0YXN...9FmWKpUoGY
Screenshot Watermark:
 Strings: 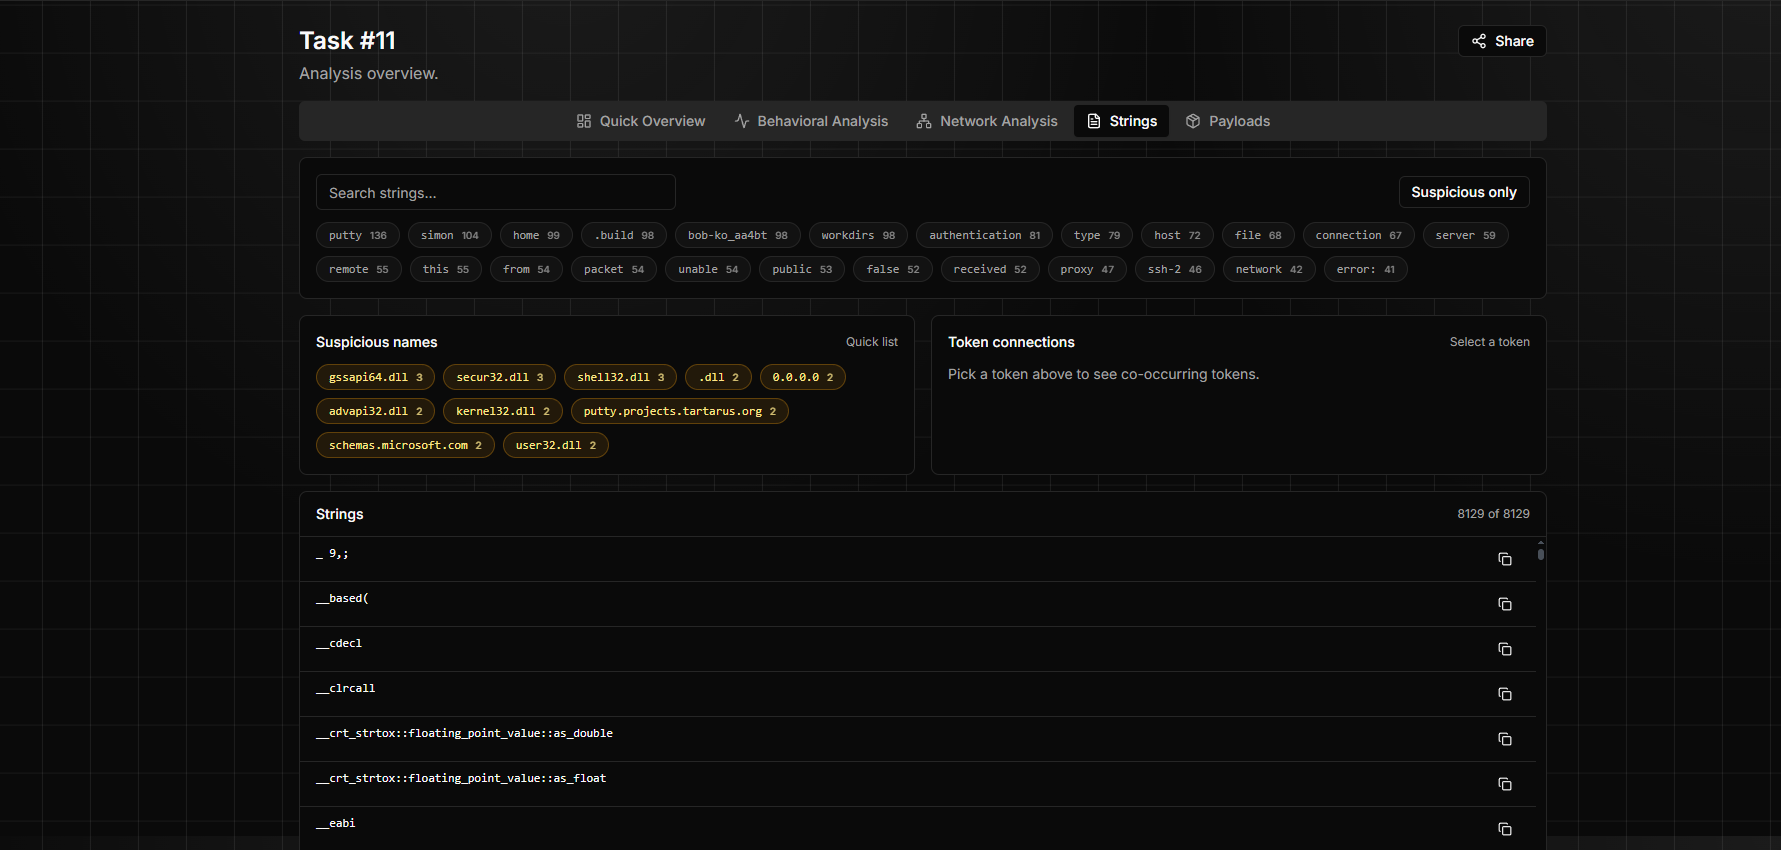
DO NOT DEAL WITH THIS MEMBER
# Security Update - 03.04.26
Improvements & Fixes- SCOOBE Error Resolution - Corrected Second Chance Out-of-Box Experience (SCOOBE) initialization error in Windows 11 sandbox environment. Platform now properly handles system recovery procedures without affecting analysis integrity.
- Execution Timeout Adjustment - Optimized maximum execution time parameters for improved analysis performance and resource allocation across worker nodes. (120S Default)
- Script File Execution - Corrected execution errors with .VBS, .JS, and .BAT script files. Proper interpreter integration and execution context now enabled for accurate behavioral analysis.
- Windows System Integration - Fixed errors related to Windows Update and Windows Services initialization. System stability and service availability now properly maintained during analysis tasks.
- Share Links UI Alignment - Corrected Share Links interface layout. UI elements now properly centered and aligned for improved visual consistency and user experience.
- Extracted Text Tab - Added new tab for Extracted Text analysis:
- Dedicated tab for viewing extracted text from .VBS, .BAT, .JS and other script files
- Automatic text extraction from all files dropped to system by any parent file
- Comprehensive analysis of dropped file contents for threat intelligence
- Ideal for identifying obfuscated code, hidden commands, and payload inspection
- String Data Correction - Fixed error with string data extraction and processing. String analysis now returns accurate and complete results.
- VM File Execution Naming - Executed files within virtual machine environment now retain original filename for improved traceability and analysis consistency:
- Files are extracted to desktop for enhanced icon visualization
- Original filename preservation allows easier identification of malware behavior
- Improves correlation between executed files and behavioral analysis logs
- Feature currently under active development for refinement
UI Updates & Known Issues
Interface Refinement In Progress:
We are currently updating the user interface for several analysis pages including Strings Tab, Text Extractor, and related features. During this ongoing update phase, please be aware that minor visual inconsistencies and functional errors may occur on these pages. We appreciate your patience as we work to enhance the user experience and interface stability.
Affected Pages:- Strings Analysis Tab
- Text Extractor Module
- Related analysis panels
Testing Phase Notice:
All implemented features are currently undergoing active testing. While we have thoroughly validated core functionality, minor errors and edge cases may occur. These will be corrected over time as we continue development and receive user feedback.
This sounds sus reliable,will see
DO NOT DEAL WITH THIS MEMBER
(Mar 5, 2026 12:42 AM)MadScientist Wrote: This sounds sus reliable,will see
Thank you for your support, I intend to regularly update the project so that we can start sales soon :)
Very cool. Did you base it on something like Cuckoo Sandbox or similar? Or is it made completely from scratch?
DO NOT DEAL WITH THIS MEMBER
(Mar 5, 2026 03:16 PM)5chn4pp Wrote: Very cool. Did you base it on something like Cuckoo Sandbox or similar? Or is it made completely from scratch?
Hi buddy, I use Cuckoo as a base because it has greater customization possibilities, but I've included some small excerpts from CAPE that I believe are more optimized (malware extraction). Here are some of the sources, enjoy!
Cuckoo Github:
https://github.com/cuckoosandbox/cuckoo
Cape:
https://capev2.readthedocs.io/en/latest/...grade.html
Note: The scantime scanner, which will be released soon, will be made from scratch.
(Mar 5, 2026 03:20 PM)am00 Wrote: Hi buddy, I use Cuckoo as a base because it has greater customization possibilities, but I've included some small excerpts from CAPE that I believe are more optimized (malware extraction). Here are some of the sources, enjoy!
Cuckoo Github:
https://github.com/cuckoosandbox/cuckoo
Cape:
https://capev2.readthedocs.io/en/latest/...grade.html
Note: The scantime scanner, which will be released soon, will be made from scratch.
No problem, both of those are good tools. I am sure some people on here would enjoy private malware scanners rather than the current public ones available.
If you have any questions you can PM me if you want. I have over 4000 posts in the malware removal section since 2014.
DO NOT DEAL WITH THIS MEMBER
Mar 5, 2026 03:30 PM
(This post was last modified: Mar 5, 2026 06:48 PM by am00.)
(Mar 5, 2026 03:27 PM)5chn4pp Wrote: No problem, both of those are good tools. I am sure some people on here would enjoy private malware scanners rather than the current public ones available.
If you have any questions you can PM me if you want. I have over 4000 posts in the malware removal section since 2014.
Thank you for your availability, I'll let you know if I need anything ^^
# Security Update - 03.05.26
Improvements & Fixes- Strings Page Optimization - Enhanced performance and responsiveness of the Strings analysis interface for faster string data retrieval and filtering operations.
- Payloads UI Correction - Fixed user interface layout and visual consistency issues on the Payloads analysis page. Improved readability and data presentation.
- TaskID Randomization - Implemented randomized Task ID generation to prevent security vulnerabilities and potential ID enumeration attacks. Each analysis task now receives a unique randomized identifier.
- Extracted Text Correction - Fixed errors and improved functionality in the Extracted Text module. Text extraction from dropped files and script analysis now operates reliably.
- Compressed File Compatibility - Enhanced support for compressed archive formats (.ZIP, .RAR):
- Compressed files can now be submitted directly for analysis
- Archives are automatically extracted to desktop environment
- Enables execution of archived files with their dependencies intact
- Improved behavioral analysis accuracy for packed malware samples
- UserID Randomization - Implemented randomized User ID generation across the platform to prevent security vulnerabilities and unauthorized user enumeration. Each user session receives a unique randomized identifier for enhanced privacy and security.
Known Issues- Windows Defender False Positives - Occasional false positive detections reported by Windows Defender during analysis execution. We are actively working on improving detection accuracy and will address this issue in the next update.
Testing Phase Notice:
All implemented features are currently undergoing active testing. While we have thoroughly validated core functionality, minor errors and edge cases may occur. These will be corrected over time as we continue development and receive user feedback.
I'm Stanley HF's helper bot. The OP (original poster) of this thread wants everyone to see this page and has elected to bump it to the top of the showthread listing. Since HF doesn't want a ton of LQP (Low Quality Posts) this is the best method of bumping your content. There is a small βyte fee for each bump. Any OP can bump any of their threads on HF from the linked icon on the top of their first post.
If you haven't already read the first post of this thread we encourage you to do so.
Thanks,
Stanley
I am the official HF Help Bot. You might get an automated PM from me with some helpful information.
Please read our Help Docs.
DO NOT DEAL WITH THIS MEMBER
Mar 8, 2026 05:16 PM
(This post was last modified: Mar 9, 2026 09:41 AM by am00.)
# Security Update - 03.08.26
New Features- Dynamic Video Recording (WebM) - Redesigned analysis visualization system. Every submission now generates and displays complete execution recording within the virtual machine environment. Implemented native Video Player on results page with timeline controls, allowing users to advance and rewind through video playback to inspect exact behavioral patterns without requiring file downloads.
Improvements & Fixes- Clean and Intelligent Interface - Reports tab now automatically hides empty tables and sections from display (such as Payloads, Dropped Files, or Suspicious Names when malware does not generate them), eliminating visual clutter and improving focus on relevant data.
- Optimized Reading Design - Large data blocks (such as File Details and Connection Lists) now appear minimized by default with smooth expansion animations when required. Behavior tab has been simplified for significantly faster loading performance.
- Stable Page Loading - Improved page rendering during live analysis processing. Now utilizes Skeleton Loader components to maintain screen stability and prevent layout shifts when final data arrives.
- Windows Defender False Positives Resolution - Resolved the known issue from previous build. Adjusted internal detection engine to prevent broad system rules from generating false alerts on clean files. Detection accuracy significantly improved.
- Script File Execution (.VBS) - Fixed chronic error that caused VBS file submissions to fail prematurely and result in failed_analysis status. Script execution now operates reliably.
- Core Engine Stability - Resolved critical performance bugs related to unknown status returns and processor shutdown loops that in rare cases prevented report finalization (Hard Timeouts) or left interface frozen awaiting data.
Known Issues- Video Timeline Navigation - Users are unable to skip or jump to specific timestamps during video playback. Timeline seeking functionality is currently non-functional and will be fixed in the next update.
- .NET Framework Dependency for Native Files - Analysis of native C++ files and compiled executables requires .NET Framework installation on the analysis machine. We are implementing automatic dependency resolution to streamline this process in upcoming releases.
- Scan Processing Performance - Average analysis completion time is approximately 3.5 minutes per submission. We are actively optimizing worker resource allocation, parallel processing, and behavioral analysis pipeline to significantly reduce completion times in the next update.
Testing Phase Notice:
All implemented features are currently undergoing active testing. While we have thoroughly validated core functionality, minor errors and edge cases may occur. These will be corrected over time as we continue development and receive user feedback.
Hey everyone, just a quick update — this project is moving to the marketplace section for better visibility and organization.
You can follow all future updates, changelogs, and discussion here:
https://hackforums.net/showthread.php?tid=6321541
Thanks for the support so far — see you there.
goahead.cc — runtime malware analysis
|