


So there might be a better way of doing this on windows but while I work on my project, this is the best you will get out of me.
You will need
Cain and abel http://www.oxid.it/cain.html
Wireshark https://www.wireshark.org/download.html
Please note the first part of this tutorial is taken from the following site to save me from editing pictures and uploading, all credit goes to the author.
https://neelpathak.wordpress.com/2013/05...abel-tool/
To start what you need to do is open Cain and abel
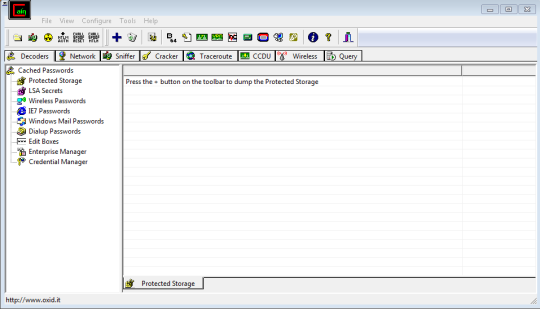
Goto -> Sniffer Tab and click Configure in the main menu to configure your packet listening adapter.
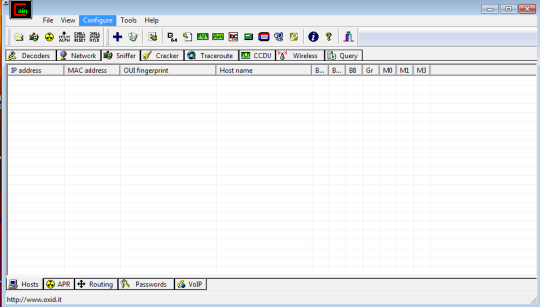
Select the appropriate network adapter for your network that you want to sniff the packets for plain-text passwords. And Click Ok.

Click the Green Adapter icon as shown below. This means that you just configured the adapter and now you are turning it ON.

Now select the APR tab below as shown and now first click on the right side upper pane area. When you click that area the blue plus (“+”) icon will get enabled. Press that blue plus (“+”) icon.
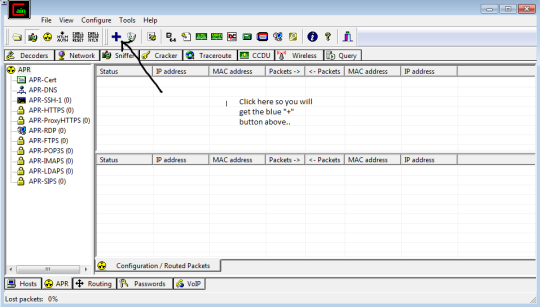
This is very interesting step. Now we need to select the router`s IP address and click ok. This means that we want to listen to every packet that is sent to router. If we select any other IP address in our LAN network then we can listen to only that particular HOST on the network. Since the router responds to all the request of HOSTS connected in a LAN. Thus we can listen to all the HOSTs.

Now click the Yellow Circle icon as shown. This means that we are starting ARP poisoning.

We can see that in the upper right panel there is an IP address of our router and when we press that Yellow Circle icon (button), it performs ARP poisoning.
Now click the password tab which is at the bottom. We can see that we are getting passwords of HTTP i.e. plain text session in our LAN network.

Note: While performing this practical you will notice that there is significant reduction in he network speed. This is due to the fact that ARP spoofing on the LAN network creates many fake packets advertising other`s host identity.
==============================================
Now open Wireshark.
Press the circle button at the top, "Capture options" Then choose your network card that is running on cain and abel, then hit start.

Let that run for a while, and when you are done, hit file - then hit export objects, http...

Then hit save all and choose a place to save the images.
Now you can open that folder and view all the images your network has been viewing.
If you are unable to choose "Export objects" you may need to hit file, save as first then choose export objects.
You will need
Cain and abel http://www.oxid.it/cain.html
Wireshark https://www.wireshark.org/download.html
Please note the first part of this tutorial is taken from the following site to save me from editing pictures and uploading, all credit goes to the author.
https://neelpathak.wordpress.com/2013/05...abel-tool/
To start what you need to do is open Cain and abel
Goto -> Sniffer Tab and click Configure in the main menu to configure your packet listening adapter.
Select the appropriate network adapter for your network that you want to sniff the packets for plain-text passwords. And Click Ok.
Click the Green Adapter icon as shown below. This means that you just configured the adapter and now you are turning it ON.
Now select the APR tab below as shown and now first click on the right side upper pane area. When you click that area the blue plus (“+”) icon will get enabled. Press that blue plus (“+”) icon.
This is very interesting step. Now we need to select the router`s IP address and click ok. This means that we want to listen to every packet that is sent to router. If we select any other IP address in our LAN network then we can listen to only that particular HOST on the network. Since the router responds to all the request of HOSTS connected in a LAN. Thus we can listen to all the HOSTs.
Now click the Yellow Circle icon as shown. This means that we are starting ARP poisoning.
We can see that in the upper right panel there is an IP address of our router and when we press that Yellow Circle icon (button), it performs ARP poisoning.
Now click the password tab which is at the bottom. We can see that we are getting passwords of HTTP i.e. plain text session in our LAN network.
Note: While performing this practical you will notice that there is significant reduction in he network speed. This is due to the fact that ARP spoofing on the LAN network creates many fake packets advertising other`s host identity.
==============================================
Now open Wireshark.
Press the circle button at the top, "Capture options" Then choose your network card that is running on cain and abel, then hit start.
Let that run for a while, and when you are done, hit file - then hit export objects, http...
Then hit save all and choose a place to save the images.
Now you can open that folder and view all the images your network has been viewing.
If you are unable to choose "Export objects" you may need to hit file, save as first then choose export objects.


