Jun 21, 2018 11:35 AM
(This post was last modified: Jun 21, 2018 12:06 PM by CleanCarrot.)
Hello everyone, ever wanted to learn some cryptography and decrypting basics? Here you are on the right place, you'll learn it in a progressive way.
INTRODUCTION
This part isn't the most important but it's a important part for understanding this tutorial. Cryptography is the art to hide messages and phrases. You'll need some informatic and mathematic knowledge to undesrtand this tutorial. Why does cryptography exists? To keep messages secret, but why would anyone keep them secret? For example to prevent from a war or just send someone a secret message. In this tutorial I will only talk about the "new" cryptography methods, the methods that are used in our society since the second war. I won't talk about decryption, I will soon make another tutorial about it. But to begin I'll still talk about the ceasar Cipher, the base of the whole cryptography...
1] Ceaser Cipher
The ceasar Cipher, named "rotation encryption" too is the easyiest way to encrypt a message. It's named "ceasar Cipher" because ceaser himself used it (atleast it's said in the mythology haha). This cryptography method is based on alphabetic substitution:
Here ROT1 is used. A becomes B, B becomes C etc...
For example: Hello becomes ifmmp
Still today, this encryption type is used and often used for ROT13 (13 rotations). Decrypt messages encypted with the ceasar cipher is very easy. You only need to do the inverse rotation to the encrypt-rotation number and you get the clear text. A not so safe method to hide messages.
2] Vigenère cipher
This second encryption method I will show you is like the ceasar cipher (a letter becomes another letter) but this time, an "A" can for example become a "F" the first time it's written and a "T" the second time. For this encryption, a passphrase is used, you'll see it's a bit more interesting concerning security but still very easy to crack.
Okay imagine you want to crypt "hello" with the passphrase "Carrot".
You need to imagine:
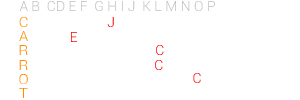
Here you can see the passphrase "CARROT" and with the alphabet in line 1 and the table I just created you can find the encrypted "HELLO", here "JECCC".
With every Caracter of the password, a new alphabet is started at position "1" from this caracter. For example "B" -> "B-C-D....."
This passphrase is repeated as many times as there are caracters in the message that has to be encrypted. With the normal alphabet at the top of the table, you can easily encrypt your message with the passphrase you chose.
Even if it's a bit stronger than the ceasar cipher, it's still very easy to decrypt this encryption method.
1] The symetric-key algorithm system
To understant this part you'll need to understand what an encryption function is:
Code
f : M -> CWhere M is the whole clear message and C the whole encrypted message. This means that by using the function f on the clear message, you'll get the encrypted message. This applies to all symetric-key algorithms.
Symetric-key algorithm: A algortihm that uses the same key for the encryption and for the decryption.
To decrypt the message crypted with f:
Code
f^(-1) C -> MThis means that you can't get two different clear messages with one encrypted message. To decrypt the encrypted message, you'll need the inverse function of the function you used to encrypt the clear message. That makes the decryption very easy if you know the key.
2] The Vernam Cipher
1917, Vernam invents an encryption algorithm that was so secured, that it was even used to encrypt the messages between the USA and the URSS during the cold war.
How to use :
- The key has the same size as the message to encrypt
- The caracters of this key are generated randomly
- The key can't be used more than one time
How it works:
First of all the message, currently "hello" is converted to binary :
Code
Hello: 01001000 01100101 01101100 01101100 01101111(read this tutorial if you have no idea how to do this : https://en.wikipedia.org/wiki/Binary_code)
Than the key is generated. Lets imagine the key is "Carro"
Code
Carro: 01000011 01100001 01110010 01110010 01101111Than you need the logical operator XOR to encrypt this message with the help of the key.
XOR is used like this:
Code
1 XOR 1 = 0

1 XOR 0 = 1

0 XOR 0 = 0

0 XOR 1 = 1
The encryption algorithm is this:
Code
E-> M XOR KWith K the key, here "Carro", M the message, here "hello" and E the encrypted result.
It works like this:
Code
M: 01000011 01100001 01110010 01110010 01101111

K: 01001000 01100101 01101100 01101100 01101111

E: 00001011 00000100 00011110 00011110 00000000
The encrypted message is "00001011 00000100 00011110 00011110 00000000"
To decrypt you take again the encryption key, here "Carro" and you apply the same alogrithm with the same key to the encrypted message:
Code
M = K (*)^(-1) E

Here, (*) is the encryption algorithm that is used: here XOR

(*)^(-1) is the inverse function of the encryption algorithm used: here the inverse function of XOR is still XOR (cool ^^)
So we can decrypt E with K using XOR
Code
E: 00001011 00000100 00011110 00011110 00000000

K: 01001000 01100101 01101100 01101100 01101111

M: 01000011 01100001 01110010 01110010 01101111
Okay, now we finished the easy part haha
Quote:Whaaaat? This was the easy part?
Yeah, this was the easy part haha, now we'll talk about the...
3] The FEISTEL SCHEMA
Okay we now know how to encrypt a string with a key that has the size of the string. But how about a short key, but still with optimal security? Therefore, some searches found a way to encrypt strings with 80 to 120 bits keys.
How does it work?
Okay let's imagine we take the key "0010" and we want to encrypt the message "0110 0001" with it.
our argument dor the function f is "0010", our key.
We take the number of bits in the key, here n=4, and we split our message into blocks that are 2n bits large.
Here "0110 0001" is already 8 bits, so we won't need to split it.
This block we split it into two other blocks with n bits. Here our message is splitten into:
Code
G: 0110

D:0001


(G and D are variables)
with this two blowks we will generate two encrypted blocks containing each n bits:
In this schema you can see the working of the FEISTEL Schema.
the left encrypted block here, the block "L" contains the data from our right not-encrypted block, "D"
The right encrypted block contains G XOR f(D)
That means:
Code
D = 0001

K = our key, here 0010

f(D) = D XOR K

f(D) = 0001 XOR 0010 = 0011


and G XOR f(D) = 0110 XOR 0011 = 0101
Our encrypted message is "0001 0101".
Here you can see that the left part is the same as the right part of the clear message, but to prevent this, we create a loop, looping this FEISTEL Schema. For example the DES encryption algorithm uses this loop 16 times.
The f function varies between the different encryption methods, I was quite simple I just used the Fx: -> K XOR x function.
Normally, new keys are generated from the official key every loop, this is named the "key shedule" :
exmple K1, K2, K3 ... K16 for 16 loops.
To decrypt a message crypted with this schema it's quite easy, you just need to begin from the encrypted message and do the same loops but beginning with the K16 if you had 16 loops.
Many modern cryptography use the Feistel cipher like:
- AES
- DES
- Blowfish
- ICE
- And many other
Conclusion
So, this mini tutorial for beginners is finished, but don't worry here is just the basis of cryptography I will do some other tutorials if I get some nice feedback haha! I hope you enjoyed and feel free to ask me any questions or to correct some little details if you find errors!
Thanks for reading!
Cheers 🤝