DO NOT DEAL WITH THIS MEMBER
(Jan 3, 2020 02:56 PM)Gizmo Wrote: All clear, thank you for the reply.
Not a problem, any issues just hit me up.
veryyyyyy nice i like it .. but can we do a rainbow crack instead of sending the specimen to that website ?, how can we really effective when using rainbow tables ?
DO NOT DEAL WITH THIS MEMBER
(Jan 4, 2020 10:57 AM)SchwererGustav Wrote: veryyyyyy nice i like it .. but can we do a rainbow crack instead of sending the specimen to that website ?, how can we really effective when using rainbow tables ?
You can however it's much easier to pay a few dollars and get a lot cracked than run it on a single GPU.
What is your recommendation ?
Dual booting Kali with other OS or Virtualisation
DO NOT DEAL WITH THIS MEMBER
(Jan 5, 2020 01:31 AM)ETH Wrote: What is your recommendation ?
Dual booting Kali with other OS or Virtualisation
Either works just fine, even live boot is fine. Depends on your main system specs and how it can handle virtualization.
DO NOT DEAL WITH THIS MEMBER
Jan 6, 2020 06:56 AM
(This post was last modified: Jan 6, 2020 06:57 AM by dhragon11.)
(Jan 2, 2020 12:41 PM)Mr. Robot Wrote: Here is my job, I posted a really low price on it for this just to show for this thread.
https://hashes.com/escrow/item/?id=471

[/color][/align]
You can also use https://www.onlinehashcrack.com/ it is basically the same with the site you suggested, not sure which one is cheaper to use.
DO NOT DEAL WITH THIS MEMBER
(Jan 6, 2020 06:56 AM)dhragon11 Wrote: You can also use https://www..com/ it is basically the same with the site you suggested, not sure which one is cheaper to use.
DO NOT USE THAT SITE. Getting your hash cracked by others vs a site charging money ? fuck that.
DO NOT DEAL WITH THIS MEMBER
Got some updates for the people DMing me.
DO NOT DEAL WITH THIS MEMBER
Jan 11, 2020 05:42 AM
(This post was last modified: Jan 11, 2020 05:42 AM by erotic.)
(Jan 2, 2020 12:41 PM)Mr. Robot Wrote:
So let's just get into it. What will you achieve through this thread? You will be able to gain access to WiFi almost anywhere in the world in the same day.
You're traveling the world but you don't have WiFi? You have your laptop and a wireless adapter that is compatible? In just a few hours if not sooner you will have access to AT LEAST 1 network and if you need more, well just let it run a bit longer.
How easy is it? Well you could automate the entire process like I have or just run it manually when you need too.
>> I'll be adding changes with frequently asked questions if anyone has issues.
I've been able to get access to 1,000+ networks in the same day.
Process color coded and split into 3 categories.
1. Installation and setup
2. Running the tool and stopping the tool.
3. Upload text file online and wait.
What equipment do I need?
1. A wireless adapter that supports monitor mode.
2. A laptop OR Desktop OR Raspberry PI
3. A USB with Kali Linux (or install it if using laptop) (Copy of Kali Linux download if using Desktop) (Kali Linux on Raspberry PI if using PI)
Wireless adapters that work:
https://www.amazon.com/gp/product/B00NAXX40C/
https://www.amazon.com/gp/product/B003EVO9U4/
https://www.amazon.com/gp/product/B00EQT0YK2/
https://www.amazon.com/gp/product/B00JDVRCI0/
https://www.amazon.com/gp/product/B073J3HXZH/
I'd highly recommend a laptop for this due to the fact you can carry it in a backpack while walking in range of WiFi networks.
This set here, you can type in line by line exactly how they are written and it will all install perfectly for you. No stress. Make sure you have an internet connection when first installing. Remember if you are live booting, the entire distro will be wiped when you reboot so you will need to copy the final file off the device before rebooting it.
Code sudo apt-get update
sudo su
sudo apt install libssl-dev libcurl4-openssl-dev libpcap0.8-dev zlib1g-dev
sudo git clone https://github.com/ZerBea/hcxdumptool.git
sudo git clone https://github.com/ZerBea/hcxtools.git
sudo git clone https://github.com/hashcat/hashcat.git
cd hcxdumptool
sudo make
sudo make install
cd ..
cd hcxtools/
sudo make
sudo make install
cd ..
cd hashcat
sudo make
sudo make install
Commands we used if you want an explanation
sudo su // this command makes sure your entire session inside this terminal is run as Super User. It's not needed as we are running everything as sudo anyway for installation it just helps avoid any problems you might have with specific hardware.
apt install // this command runs "Advanced Package Tool" to install the packages listed after it. Each one is needed and if you have an issue where one isn't found, you will need to edit the file containing your 'known packages' which is where it looks online (urls) for the files to install.
git clone // this command clones the repository from github which is where the creator of this tool keeps their code and files.
cd hcxdumptool // after cloning from github in the previous command, a folder is made with the name of the tool (hcxdumptool.git into hcxdumptool folder) by using the cd command it enters that folder so we can now access it directly in terminal.
make // the make command looks at your systems layout and then decides if anything needs to be altered/changed and if everything it needs is installed to places it can find.
make install // now that make has made sure and configured file locations depending on your setup (in this case Kali Linux) the make install command will install and create binaries if necessary to put everything in its place. This is so you can run a tools name usually without being in that folder (cd) from anywhere inside the terminal.
cd .. // this command moves you up one directory. At this stage you will be inside the hcxdumptool folder and have already configured it, so now you need to go back to the root directory and this command will shift you one folder previous.
As soon as we run the following, the wireless adapter will go down, be put into monitor mode, be brought back online, check for any interfering processes - then start the attack. Any WiFi networks vulnerable in range will drop like flies and you will have a pmkid. This will be the command list you will run every time once it is already installed to your device. If you type in "iwconfig" and don't see wlan0 but another wireless device name, replace wlan0 with that - it could be wlan1, or something else entirely.
While this is running, feel free to walk around or go for a drive - collect as many as you can then get home and ctrl+c to stop
Code ifconfig wlan0 down
iwconfig wlan0 mode monitor
ifconfig wlan0 up
airmon-ng check kill
hcxdumptool -o yourcityname.pcapng -i wlan0 --enable_status 1
Remember to hit ctrl+c on your keyboard when it is done.
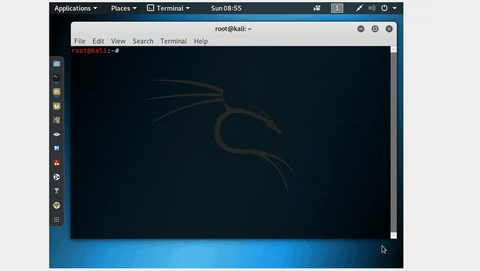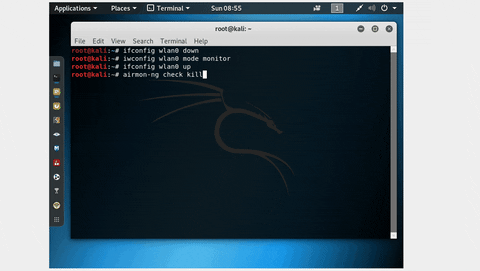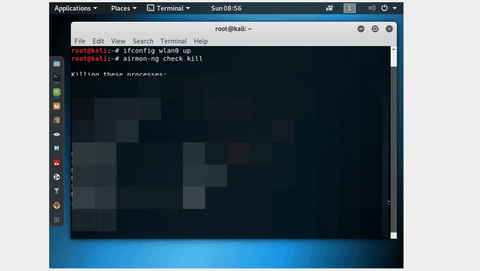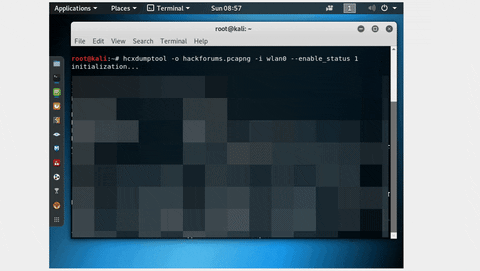
Now what we need to do is convert that file we made "yourcityname.pcapng" to a file type we can read and crack. We can do that by typing in the following. It will output a few files but we only want the one ending in 16800. The other files will contain other information you can look at like WiFi names but we can obtain those directly from the 16800 file too.
Code hcxpcaptool -E essidlist -I identitylist -U usernamelist -z yourcitynameoutputs.16800 yourcityname.pcapng
Go to Hashes.com and register for an account. Once logged in - head to "profile" and "add bitcoin"
Send like $10 or more to the bitcoin address depending on how bad you want it cracked.

>Then click Escrow - Upload new list.
This is my list - you can watch it get cracked in real time:
https://pastebin.com/7xsXGDjW
https://hashes.com/escrow/item/?id=471
>Now select your file (.16800) and choose the Algorithm "PMKID"
>Input a price in USD Per hash. The more you put in, the more the users out there will try and crack. I'd recommend judging it by total price rather than individual hash. The minimum you can offer is "0.00000050" which currently as of writing this is $0.003 USD. So at that price it would cost $3 to crack them all. I'd increase that to at least $0.009 per for your first run ($9 total for 1,000 hashes) otherwise if it's a specific network you want cracked offer as much as you would like for both speed and likelihood of getting it cracked!
If it isn't cracked, you can always cancel it and increase the price you are offering for it which in turn will speed up the rate it's cracked due to more people trying to get it done.
Any money left on your account you can withdraw later.
Here is my job, I posted a really low price on it for this just to show for this thread.
https://hashes.com/escrow/item/?id=471
Don't mind me just commenting to save this for later.
I love the Raspberry Pi idea, then you can literally just put it in a hoodie pocket.
DO NOT DEAL WITH THIS MEMBER
(Jan 11, 2020 05:42 AM)erotic Wrote: Don't mind me just commenting to save this for later.
I love the Raspberry Pi idea, then you can literally just put it in a hoodie pocket.
Sure can, makes it easy as fuck.
Nice, dude! Thank you so much for this tutorial.
DO NOT DEAL WITH THIS MEMBER
(Jan 11, 2020 11:42 AM)JamalNazamAli Wrote: Nice, dude! Thank you so much for this tutorial.
No problem, hope it helps. If you get stuck at any point hit me up or post here
(Jan 11, 2020 10:56 PM)Mr. Robot Wrote: No problem, hope it helps. If you get stuck at any point hit me up or post here
Okey, thanks. I'll keep that in mind =))
DO NOT DEAL WITH THIS MEMBER
(Jan 12, 2020 11:55 AM)JamalNazamAli Wrote: Okey, thanks. I'll keep that in mind =))
Going to be adding some other information based on any issues people have.
(Jan 14, 2020 08:18 PM)Mr. Robot Wrote: Going to be adding some other information based on any issues people have.
Do it, sounds good. Good luck!
|


