Home Upgrade Search Memberlist Extras Hacker Tools Award Goals Help Wiki Contact

C 

Manual DLL mapping. Crash on load a system DLL.

Hello Hackforums.

I'm coding in C++ a manual DLL mapper with a custom GetProcAddress.

I tried to load a DLL I created, and all works fine. I can resolve an exported function, and call it.
But when I try with user32.dll to call MessageBoxW, it crashes.


To manual map, I follow these steps :

Reading file and putting in memory
Find and check headers
Allocate memory for mapping DLL (virtual alloc)
Copy headers and sections
Fix relocations
Fix imports
Call entry point


Even on user32, everything works fine, and I'm able to get a handle that looks valid, i can even find a valid address for my function from GetProcAddress, but when I call it, I get a crash.


Is there something to do in addition on Windows DLL ? It works perfectly on my owns dlls.


Thank you very much :)
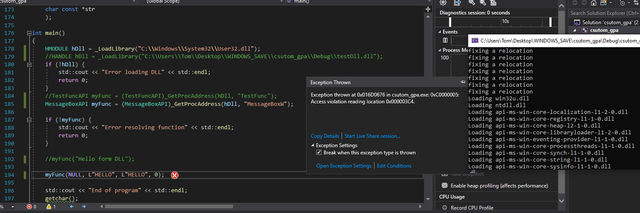
Can you provide more info on the crash?
[Image: Annotation-2020-01-14-124512.png]
you get access violation error cuz the dll is in system dir
copy it to your exe path and try it
[Image: bitcoin.png] Be Nice For Once 15hVUVz7xA4kazHdk2BuErENGCskVwjYXP
I copied the DLL to my working directory, and i get the same error.

Here a screenshot of the formats of all the executables I use

[Image: Annotation-2020-01-15-105647.png]
seems you have other problem with your mapping code
also check you are using the right code for your os 32 \ 64 and dll also can be problem using debug option over release ...
[Image: bitcoin.png] Be Nice For Once 15hVUVz7xA4kazHdk2BuErENGCskVwjYXP
I just tried with OutputDebugStringA from kernel32, and it works great.....

I don't know why my User32 is broken....
The memory address that visual studio debugger is giving to you is f*d up, like it is supposed to be a valid memory address and obviously it isnt. This means that you are passing a value instead of a pointer somewhere or your relocation is incorrect. That's why we have an access violation error, a function is trying to read memory from that address and it's invalid. Can you dive deeper and show us where the error is occuring? I think that would help
The address of my resolved function looks valid: MessageBoxA 0x013C0CD0
(Jan 14, 2020 05:54 AM)HFDone Wrote:  you get access violationerror cuz the dll is in system dir
copy it to your exe path and try it

Shut up you don't know what you are talking about.

For the user having problems:
1. Is this for 64 it or 32?
2. Show the prototype for MessageBoxAPI
3. Show disassembly of where it crashes.
4. Show callstack where it crashes.

If you don't know how to do the last 2 things use Google.
(Jan 16, 2020 05:04 AM)LivelyToerag Wrote:  Shut up you don't know what you are talking about.

For the user having problems:
1. Is this for 64 it or 32?
2. Show the prototype for MessageBoxAPI
3. Show disassembly of where it crashes.
4. Show callstack where it crashes.

If you don't know how to do the last 2 things use Google.

(Jan 15, 2020 06:19 AM)HFDone Wrote:  seems you have other problem with your mapping code
also check you are using the right code for your os 32 \ 64 and dll also can be problem using debug option over release ...
[Image: bitcoin.png] Be Nice For Once 15hVUVz7xA4kazHdk2BuErENGCskVwjYXP
the way you asked that in the first place shows that you have no reason to be trying to help others when you can't tell the difference between a memory access and opening a file.

skids gonna skid, asking more stupid questions doesn't make you look smart
Yes it's definitly very hard to understand what is going on without a detailed crash report. Maybe you should provide the full source to someone, so he can run it and see what's going on..


Possibly Related Threads...
Thread / Author Replies Views Last Post
[C] by _redbaron_Jun 14, 2024 04:56 PM 16 658 Jun 14, 2024 04:56 PM
Last Post: secret_code
[.NET] by SIM-4062753Dec 14, 2020 05:50 AM 1 371 Dec 14, 2020 05:50 AM
Last Post: HFDone
[C] by oh9odDec 7, 2020 04:55 AM 0 171 Dec 7, 2020 04:55 AM
Last Post: oh9od