


Hey guys,
is it possible to set Random IP in Metasploit Options like nmap -iR?
is it possible to set Random IP in Metasploit Options like nmap -iR?
MSF RHOST Random IP |
 (Aug 4, 2021 02:29 AM)PingByte1337 Wrote: Hey guys, the RHOST should be the ip who will receive the reversed connection so if u put random ip you will not get the reversed tcp connection
Aug 4, 2021 03:26 AM
(This post was last modified: Aug 4, 2021 03:26 AM by PingByte1337.)
(Aug 4, 2021 03:08 AM)Volcan Wrote: the RHOST should be the ip who will receive the reversed connection so if u put random ip you will not get the reversed tcp connection for a scanner u dont need a reverse connection... (Aug 4, 2021 03:26 AM)PingByte1337 Wrote: for a scanner u dont need a reverse connection... your talking about MSF RHOST and i answer about that not about scanner (Aug 4, 2021 03:08 AM)Volcan Wrote: the RHOST should be the ip who will receive the reversed connection so if u put random ip you will not get the reversed tcp connection Isn't LHOST the one you need to receive reverse connection? RHOST is the target where u wana exploit and LHOST to receive shell if target vulnerable. (Aug 4, 2021 02:29 AM)PingByte1337 Wrote: Hey guys, I think I have a rough or dumb idea to do it without any googling. You can write a bash script to generate random IPs with whatever method you want , nmap or whatever. Then in the bash script you can write a " for loop " on the list of random IPs and chain them with the MSF command in it example " set RHOST $randomIPs " via the for loop. then with the bash script write the MSF command into a " .rc " file which can be read via metasploit and execute the full MSF module u wana run. https://docs.rapid7.com/metasploit/resource-scripts/ Well some coding is needed tho , this is how I automate my MSF scans with the RC file method. I don't know if MSF have the ability to do it dint google much about it, but try typing " show advanced " command on the MSF module you are running to see if there is a settings that allows it.  (Aug 4, 2021 03:55 AM)Money- Wrote: Isn't LHOST the one you need to receive reverse connection? RHOST is the target where u wana exploit and LHOST to receive shell if target vulnerable. 100% true i mixed things up 😁 thanks for correcting me
Aug 4, 2021 07:18 AM
(This post was last modified: Aug 4, 2021 07:21 AM by PingByte1337.)
If i use an exploit i need a lhost of course but not for scan plugin.....
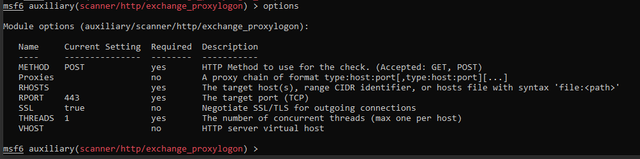 Okay, best way is script or with nmap export (Aug 4, 2021 07:18 AM)PingByte1337 Wrote: If i use an exploit i need a lhost of course but not for scan plugin..... How does nmap export works? Export nmap xml results and import into MSF? (Aug 4, 2021 07:29 AM)Money- Wrote: How does nmap export works? Export nmap xml results and import into MSF? Yes, install zenmap then u can export it with gui to csv and in msf u can set rhost the file contains the ips  |
|
|
| Possibly Related Threads... | |||
| Thread / Author | Replies | Views | Last Post |
| by PingByte1337Nov 19, 2021 01:09 PM | 3 | 345 |
Nov 19, 2021 01:09 PM Last Post: MysticNetworks |
| by PingByte1337Jul 30, 2021 09:29 AM | 4 | 261 |
Jul 30, 2021 09:29 AM Last Post: PingByte1337 |
| by oshwaishMar 3, 2020 10:48 PM | 1 | 222 |
Mar 3, 2020 10:48 PM Last Post: CyberStrike |

