And it doesn't even require a 12-year-old version of Adobe Reader. The exploit downloads and executes malicious payloads when the infected PDF file is opened with current versions of Foxit PDF Reader (<2024.3) and users accept the warning messages. Read the details here. No PoC is available.
[Fallen] Actual PDF exploit that works |
 
May 29, 2024 06:59 PM
(This post was last modified: May 29, 2024 07:27 PM by Scrubspoof.)
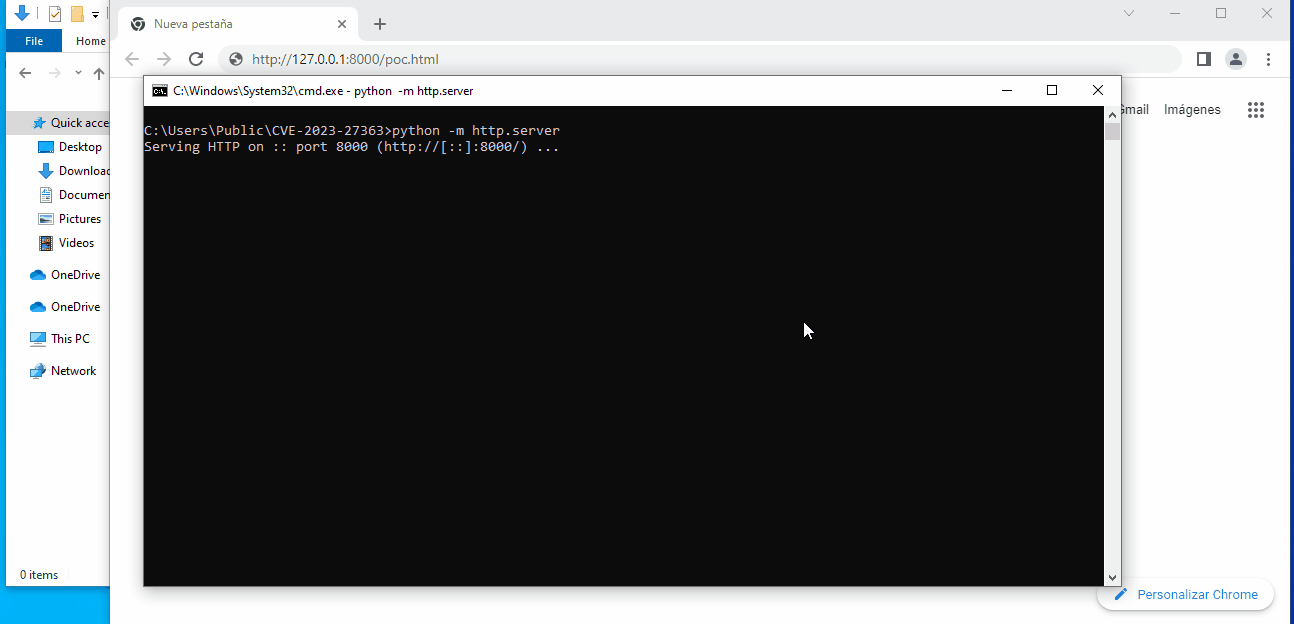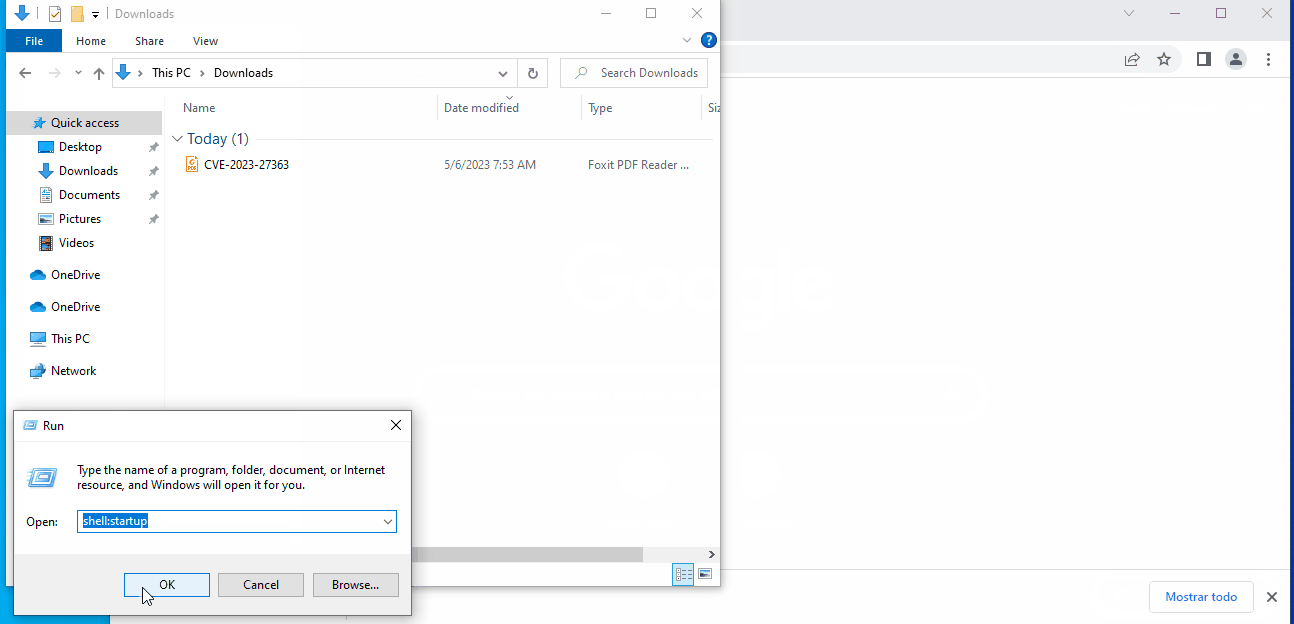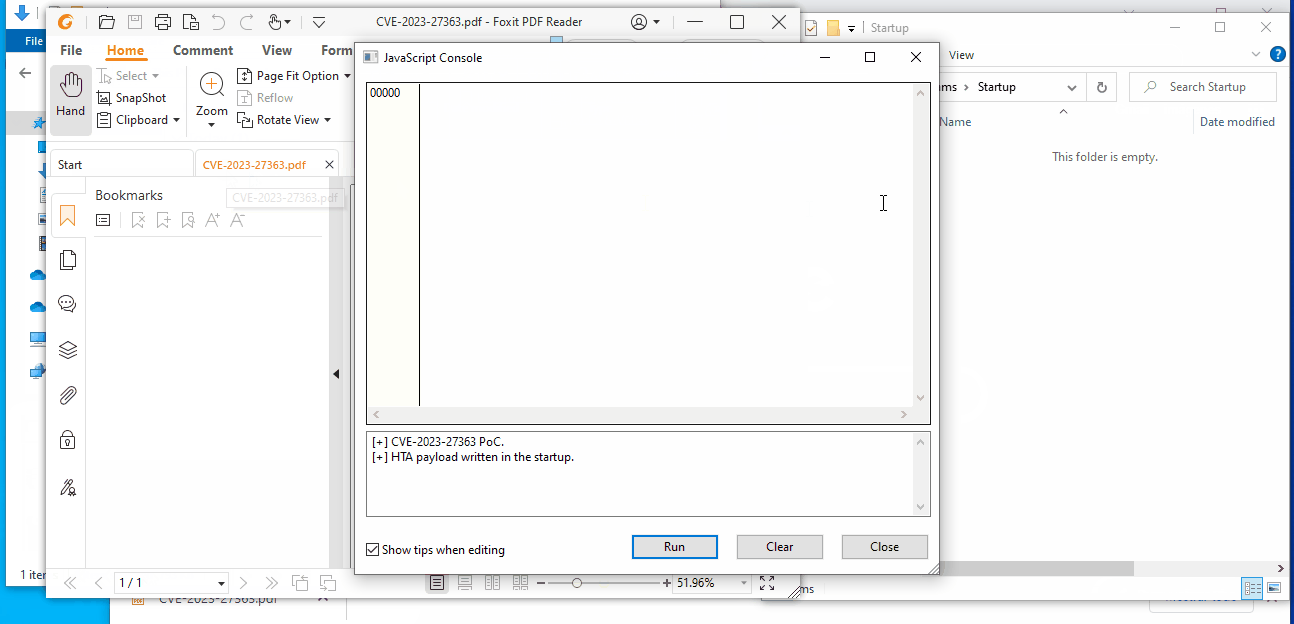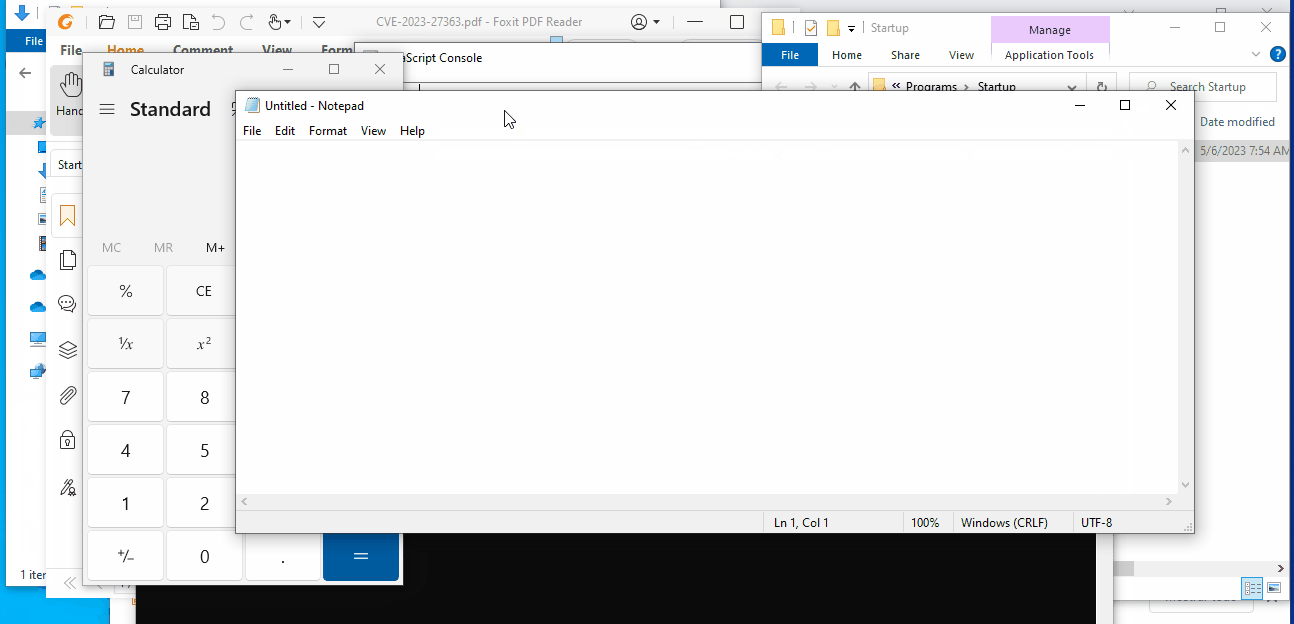 Why would anyone not use a standard browser to open/edit/print PDFs in 2024?
I know that the government has me on a list
I got my own list that has the government on it I'm on my best behavior in the key of a major Making all this money change my name and see you later
I had to show this to my Security Team at my work because we use Foxit PDF on almost every system deployed for employees. We only open PDFs mainly with our business however some folks use it for metrics and share between other companies and such so I made sure they were aware of this CVE.
Long story short my security team loves me because I bring new CVEs to them weekly that could affect us as a whole. I would like to think I'm very secure person and have good security measures put in place either physically or within my own brain. But if someone in my company got infected then it could affect me so I take it very seriously. (May 29, 2024 07:45 PM)Burger Wrote: I had to show this to my Security Team at my work because we use Foxit PDF on almost every system deployed for employees. We only open PDFs mainly with our business however some folks use it for metrics and share between other companies and such so I made sure they were aware of this CVE. As security, why use external software to open PDFs in 2024?
I know that the government has me on a list
I got my own list that has the government on it I'm on my best behavior in the key of a major Making all this money change my name and see you later (May 29, 2024 07:53 PM)Scrubspoof Wrote: As security, why use external software to open PDFs in 2024? I do not control the stack of what we use at my Company. I am not in the control group for any of that, I have my own specialized team I lead however we follow what the man above says to do and use. Honestly yes we can use Chrome or whatever as a PDF Viewer however we do a lot of signing and such with Forms for ISP, Client contracts, etc. (May 29, 2024 08:21 AM)DramaKing Wrote: It exploits the PDF reader. There's literally an illustration of the exploit chain at the top of that article. isn't fallen supposed to be a 1337 hacker group. go ahead and explain to him how it works considering your post is nothing more than a glorified headline. no need to get passive aggressive due to a response in your brainrot thread 'a pdf exploit that works' there's many methods that work on a plethora of readers. this is not new nor uncommon. hence the long list of cves published in 2024 targeting foxit alone https://www.cvedetails.com/vulnerability...eader.html takes 2 seconds to find technical details regarding this exploit (assuming you have any knowledge about what you create these glorified headlines about, which in your defence is rare on hf these days)  (May 29, 2024 11:20 PM)Yung Zel Wrote: Aren't you just a good little soldier helping out your boss! Yeah burger, I agree with Yung Zel. In my work or people I work with, I never share CVEs to them since I believe it wouldn't affect my paycheck or salary. I guess you just happen to be the typical good white hat who wants to keep things at bay. 🙃 (May 31, 2024 05:36 PM)happygonutty Wrote: Yeah burger, I agree with Yung Zel. In my work or people I work with, I never share CVEs to them since I believe it wouldn't affect my paycheck or salary. I guess you just happen to be the typical good white hat who wants to keep things at bay. 🙃 Your company getting hit with a cyber attack is never good. Even if nothing happens, you could make a good impression as to your value as a worker. (May 31, 2024 05:51 PM)DramaKing Wrote: Your company getting hit with a cyber attack is never good. Even if nothing happens, you could make a good impression as to your value as a worker. Well you are right but sometimes its best that you also benefit from it if it is not your role in the company or you are asked to do it. But if cyber attacks are your responsibilities (I believe OP is responsible for this) then sure why not, I would definitely report new CVEs weekly as well regardless if it goes to paycheck or not. 
Oct 2, 2024 01:05 AM
(This post was last modified: Oct 4, 2024 02:22 AM by Bastille.)
found this video myb still working [deleted] how test it ?
Oct 2, 2024 04:45 AM
(This post was last modified: Oct 2, 2024 05:04 AM by DramaKing.)
(Oct 2, 2024 01:05 AM)choucha3dz Wrote: found this video myb still working youtu.be/o9UIlS3Sxjk how test it ? Hack-Tools.net is a scam. I think that @Snyke@ put it well on something similar. RE: inquiry |
|
|