Jul 14, 2025 08:20 PM
(This post was last modified: Jul 14, 2025 08:21 PM by ·CHESTER·.)
I am using Shellter to embed a meterpreter payload into an EXE. It doesn't get caught when statically checked, but it does get caught when I run it. It says WD catches it based on behavior. How do I bypass this?

I assume that you didn't pay for it (HF rules specifically forbid discussion of cracks/warez), and therefore you won't receive the upcoming version with enhanced runtime evasion. It's proprietary software, so you're stuck sifting through the Marketplace, looking for a crypter that's reasonably legit. Then you have to spread it in such a way that people will download and run it. Finally, you'll be able to hack people while jumping at every knock on your door.
(Jul 14, 2025 09:15 PM)DramaKing Wrote: I assume that you didn't pay for it (HF rules specifically forbid discussion of cracks/warez), and therefore you won't receive the upcoming version with enhanced runtime evasion. It's proprietary software, so you're stuck sifting through the Marketplace, looking for a crypter that's reasonably legit. Then you have to spread it in such a way that people will download and run it. Finally, you'll be able to hack people while jumping at every knock on your door.
I am using the free version of Shellter (not cracked version). But the main thing I am trying to achieve is to do everything for free. I don't want to buy rats or crypters. I want to use free and open source products or make it myself. But all the online guides tends to be outdated and its a random mixture of stuff. And when you come up against AV block, there is no guide for how to evade it.
(Jul 15, 2025 12:42 AM)·CHESTER· Wrote: I am using the free version of Shellter (not cracked version). But the main thing I am trying to achieve is to do everything for free. I don't want to buy rats or crypters. I want to use free and open source products or make it myself. But all the online guides tends to be outdated and its a random mixture of stuff. And when you come up against AV block, there is no guide for how to evade it.
if you head over kali linux, there is tools to create payload, rat, crypting and more for free. Like Byob, routersploit and more than could be great to make you something. Yeah defender will block any suspicious files or exploit that try to run malicious files. you can use batch or powershell script to bypass this, get the file crypted what is a must do to make it easier and or use exploit. with bat2exe, a bat to turn off defender and download it could work. with physical acces BADusd are terrible tool to do this.
Jul 15, 2025 01:22 AM
(This post was last modified: Jul 15, 2025 01:23 AM by ·CHESTER·.)
(Jul 15, 2025 12:56 AM)DeathPenalty666 Wrote: if you head over kali linux, there is tools to create payload, rat, crypting and more for free. Like Byob, routersploit and more than could be great to make you something. Yeah defender will block any suspicious files or exploit that try to run malicious files. you can use batch or powershell script to bypass this, get the file crypted what is a must do to make it easier and or use exploit. with bat2exe, a bat to turn off defender and download it could work. with physical acces BADusd are terrible tool to do this.
crypting is not going to get past runtime behaivor detection, which is what the case is here
(Jul 15, 2025 12:49 AM)MarlboroMan Wrote: Sigh...
https://maldevacademy.com/
holy shit can you stop shilling your dumb course? i read it the first time. now i am definitely not going to sign up for it because i know your scamming ass is involved.
(Jul 15, 2025 12:42 AM)·CHESTER· Wrote: I am using the free version of Shellter (not cracked version). But the main thing I am trying to achieve is to do everything for free. I don't want to buy rats or crypters. I want to use free and open source products or make it myself. But all the online guides tends to be outdated and its a random mixture of stuff. And when you come up against AV block, there is no guide for how to evade it.
Oh, okay. I saw the news about the leak and jumped to conclusions. Certainly the free version won't bypass behavioral/heuristic/AI detection. Open source crypters are good only for learning. Yeah, online guides are quickly outdated.
(Jul 16, 2025 12:35 AM)MarlboroMan Wrote: Pretty much the only course that teaches skids (like you) the ropes off offensive security and helps you understand C/C++.

(Jul 16, 2025 12:35 AM)MarlboroMan Wrote: WTF. I'm not involved at ALL.
M4ldev happens to be one of the most legendary, beginner friendly courses. Pretty much the only course that teaches skids (like you) the ropes off offensive security and helps you understand C/C++.
This reply you just made shows how little input your putting in this. And btw calling me scammer is fucking stupid too, one glance at my contract stats would've learned you that too.
Just 1 hour of deep diving in the database would've expanded your horizon and knowledge.
https://search.maldevacademy.com/search?q=evasion
My advice: Stop making yourself loo
PS: Stop posting weird stuff like "Crypting doesn't get past runtime detections"
Why don't you go mind your own business. Stop replying to my threads.
Jul 16, 2025 02:25 AM
(This post was last modified: Jul 16, 2025 02:29 AM by ·CHESTER·.)
(Jul 16, 2025 02:02 AM)MarlboroMan Wrote: Perhaps if you'd ask; I'd respect that.
You're making public threads with questions to which anyone including me can answer to.
I'd also like to remind you that you need to follow The Academy's their rules when it comes to interacting with others on the forum if you're repping the group.
Shut the fuck up. No one asked for your opinion.
You are a dumb retard who doesn't read and just spams your scam course across every one of my threads. You don't ever read my issue or comment on that. You just make assumptions and start spamming your scam course. My thread about windows privilege escalation. Did you read it at all before spamming your dumb course? There is absolutely nothing on maldevscamademy that is about privilege escalation. Do you understand that there is no technique that will get you to privilege escalate on a fully updated windows 10 machine on factory settings, you dumb fuck? You couldn't hack your way out of a paper bag.
And also on maldevscamademy, half the course is like basic encrypting of payloads. If you ever read any of my posts, which you never do, you would know I have gone well past that long ago.
You have to sell your crypter for pennies because its dog shit, doesn't work, and no one wants it.
You are a dumb retard who needs to be banned of this site.
DO NOT DEAL WITH THIS MEMBER
Instead of spamming your courses maybe show him some understanding rather promoting your shitty courses Marlboro
this is peak content

DO NOT DEAL WITH THIS MEMBER
Jul 16, 2025 02:57 AM
(This post was last modified: Jul 16, 2025 02:58 AM by Jeep.)
(Jul 16, 2025 02:51 AM)MarlboroMan Wrote: 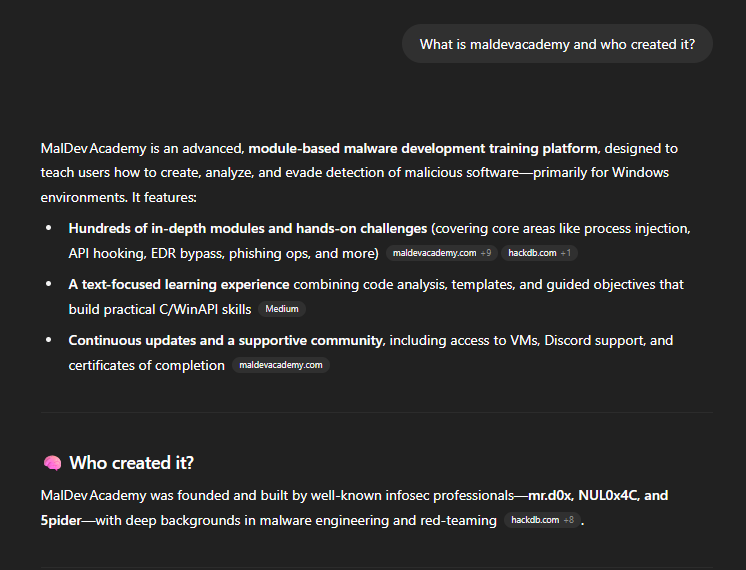
You guys have no idea how funny this is. The skids are putting it on their foreheads.
This is a legendary course.. which truly gives you the keys to offensive security.
Yet the skids (who clearly aren't invested at all) say this is my shitty scammy course? HILARIOUS.
[censored] course are OK for starters but instead of promoting it many times since not everyone here will pay for the knowledge, your could help the OP with your knowledge rather then keep posting where to buy knowledge. He is asking for help not where to buy answers
Jul 16, 2025 04:05 AM
(This post was last modified: Jul 16, 2025 04:06 AM by Dystortion.)
(Jul 16, 2025 03:05 AM)MarlboroMan Wrote: Him reading the course able it trough cracking it is 200x times more useful than me trying to explain it. If you'd actually know you'd know.
What I don't get it why you guys don't bother taking the time to actually invest yourself in what a clearly more knowledgeable figure is telling you on the manner. Instead you respond out of your neck with completely self mockery (trust me saying m4ldev academy is mine and calling it scammy is one of the dumbest things you can state as an "hacker") without even fact checking yourself!
Even in the days of AI these skids don't bother to THINK.
What kind of immaturity is that?
This is pure quality lmao, MaldevAcademy produces some of the best content their is around Malware creation. And you, almighty [mention=5616027] should know that since you are the creator :PPP
(Jul 16, 2025 12:35 AM)MarlboroMan Wrote: WTF. I'm not involved at ALL.
M4ldev happens to be one of the most legendary, beginner friendly courses. Pretty much the only course that teaches skids (like you) the ropes off offensive security and helps you understand C/C++.
This reply you just made shows how little input your putting in this. And btw calling me scammer is fucking stupid too, one glance at my contract stats would've learned you that too.
Just 1 hour of deep diving in the database would've expanded your horizon and knowledge.
https://search.maldevacademy.com/search?q=evasion
My advice: Stop making yourself loo
PS: Stop posting weird stuff like "Crypting doesn't get past runtime detections"
hhahahaha this one made me chuckle. I legit thought this goofy name maldeva was actually yours lmaooooooo. Mabolo.
This is a very explosive thread. But at least for once hackforums is arguing a about something intelligent.
Good advice MarlboroMan

The Brotherhood Vibe Legends
|