(Sep 23, 2025 11:44 AM)terminator777777 Wrote: Hello. Does the crypto work with Pulsar RAT?
Also, does it use a shared stub? I wouldn't want to lose my work because some idiot mass emails links with exe's to people
I could buy the 270$ package but would need to test with the starter pack.
Does it bypass WD and Smart screen?
How long will the FUD last if no spreading is involved? (for my exe)
I tried Mutliple crypts with Pulsar and all of them were shown undetected at scantime on kleenscan at first. However running them on an actual windows device caused it to get detected. Owner (I assume) told me it was my fault cause somehow I sent the file to AV Vendors even though I only transferred files locally. it could work but you'd have to get lucky I guess. And good luck getting a credit refund if its not fud.
(Sep 23, 2025 08:14 PM)DieterName Wrote: I tried Mutliple crypts with Pulsar and all of them were shown undetected at scantime on kleenscan at first. However running them on an actual windows device caused it to get detected. Owner (I assume) told me it was my fault cause somehow I sent the file to AV Vendors even though I only transferred files locally. it could work but you'd have to get lucky I guess. And good luck getting a credit refund if its not fud.
Thanks for the heads up mate
(Sep 23, 2025 11:44 AM)terminator777777 Wrote: Hello. Does the crypto work with Pulsar RAT?
Also, does it use a shared stub? I wouldn't want to lose my work because some idiot mass emails links with exe's to people
I could buy the 270$ package but would need to test with the starter pack.
Does it bypass WD and Smart screen?
How long will the FUD last if no spreading is involved? (for my exe)
As per the response to your ticket on the site:
I. Yes it works with Pulsar RAT.
II. No, each stub is unique and undetected upon generation.
III. Our crypts are undetected for WD, but DLL Sideloading is required for Smart Screen.
IV. The file will remain undetected until shared/distributed to AV vendors. Please note that simply having the file on your disk with internet connectivity may prompt your antivirus to submit the file for review due to its low trust score - Windows Defender is notorious for this. Also, uploading the crypted file to common file hosts without encryption / passworded zip file may also result in the file being distributed to AV vendors.

(Sep 24, 2025 05:30 PM)Tyrone Johnson Wrote: As per the response to your ticket on the site:
I. Yes it works with Pulsar RAT.
II. No, each stub is unique and undetected upon generation.
III. Our crypts are undetected for WD, but DLL Sideloading is required for Smart Screen.
IV. The file will remain undetected until shared/distributed to AV vendors. Please note that simply having the file on your disk with internet connectivity may prompt your antivirus to submit the file for review due to its low trust score - Windows Defender is notorious for this. Also, uploading the crypted file to common file hosts without encryption / passworded zip file may also result in the file being distributed to AV vendors.
Hi mate. I've created two support tickets. The file was not FUD, i've used the. persistence module, and it gets detected by windows defender
Please give me the credit back so I can test without persistence module
Oct 4, 2025 05:10 PM
(This post was last modified: Oct 4, 2025 05:12 PM by Tyrone Johnson.)
(Oct 2, 2025 08:09 AM)colombotiger Wrote: can we get your contact
PMs are open. If it is related to this project, please open a ticket on our website.
(Oct 3, 2025 05:49 PM)terminator777777 Wrote: Hi mate. I've created two support tickets. The file was not FUD, i've used the. persistence module, and it gets detected by windows defender
Please give me the credit back so I can test without persistence module
I don't believe we got the file to investigate. I tried pulling up the screenshot you shared but it has since expired.
Looking forward to resolving any issues if anyone else here has similar problems.
(Oct 4, 2025 05:10 PM)Tyrone Johnson Wrote: PMs are open. If it is related to this project, please open a ticket on our website.
I don't believe we got the file to investigate. I tried pulling up the screenshot you shared but it has since expired.
Looking forward to resolving any issues if anyone else here has similar problems.
Hello mate
I've uploaded the screenshot to filebin.net again
If you need the crypted file, I can provide that one too, I believe I still have the archive
Replied to support ticket too, thanks
Oct 10, 2025 06:51 PM
(This post was last modified: Oct 10, 2025 08:45 PM by Tyrone Johnson.)
(Oct 7, 2025 10:46 AM)terminator777777 Wrote: Hello mate
I've uploaded the screenshot to filebin.net again
If you need the crypted file, I can provide that one too, I believe I still have the archive
Replied to support ticket too, thanks
We are updating our service right now. I'll add a credit back to your account in good faith once we are done. Please keep receipts so we can mitigate issues like these in the future - we do not store uploaded files.
(Oct 8, 2025 11:15 PM)edstarly Wrote: does this work for #?
I'm assuming R3mc0s? Our automated system does not support R3mc0s, but staff can manually crypt if you open a ticket.
Updated with x64 support!
Scans - 11/10/25
Scantime (0/36): https://kleenscan.com/scan_result/000479...b7b6c75ee5
Runtime (0/18): https://kleenscan.com/runtime/scan_resul...300f801db8
Runtime scans show that execution was successful with a message box.
Oct 21, 2025 07:09 PM
(This post was last modified: Oct 21, 2025 09:35 PM by Black Jacket.)
(Oct 10, 2025 06:51 PM)Tyrone Johnson Wrote: We are updating our service right now. I'll add a credit back to your account in good faith once we are done. Please keep receipts so we can mitigate issues like these in the future - we do not store uploaded files.
I'm assuming R3mc0s? Our automated system does not support R3mc0s, but staff can manually crypt if you open a ticket.
Updated with x64 support!
Scans - 11/10/25
Scantime (0/36): https://kleenscan.com/scan_result/000479...b7b6c75ee5
Runtime (0/18): https://kleenscan.com/runtime/scan_resul...300f801db8
Runtime scans show that execution was successful with a message box.
i paid for a credit and got nothing in return
i paid for a credit, it was finally added to my account after a long wait, then the first file u uploaded did not function at all and after no response from support i paid mone more time in good faith, and the second file connected however it was instantly flagged and removed from any and all systems
Oct 22, 2025 09:19 AM
(This post was last modified: Oct 22, 2025 08:28 PM by Tyrone Johnson.)
(Oct 21, 2025 07:09 PM)Black Jacket Wrote: i paid for a credit and got nothing in return
i paid for a credit, it was finally added to my account after a long wait, then the first file u uploaded did not function at all and after no response from support i paid mone more time in good faith, and the second file connected however it was instantly flagged and removed from any and all systems
You did not provide us with your files in your ticket. Staff will examine your files when we have time. Whenever a runtime detection occurs, it is likely due to user error such as crypting a file that drops detected files or software configuration (uac bypasses or powershell commands being detected). If you have a specific software in mind, we will crypt it and report runtime detections and recommended settings.
EDIT: Here is the entire ticket conversation with this user.
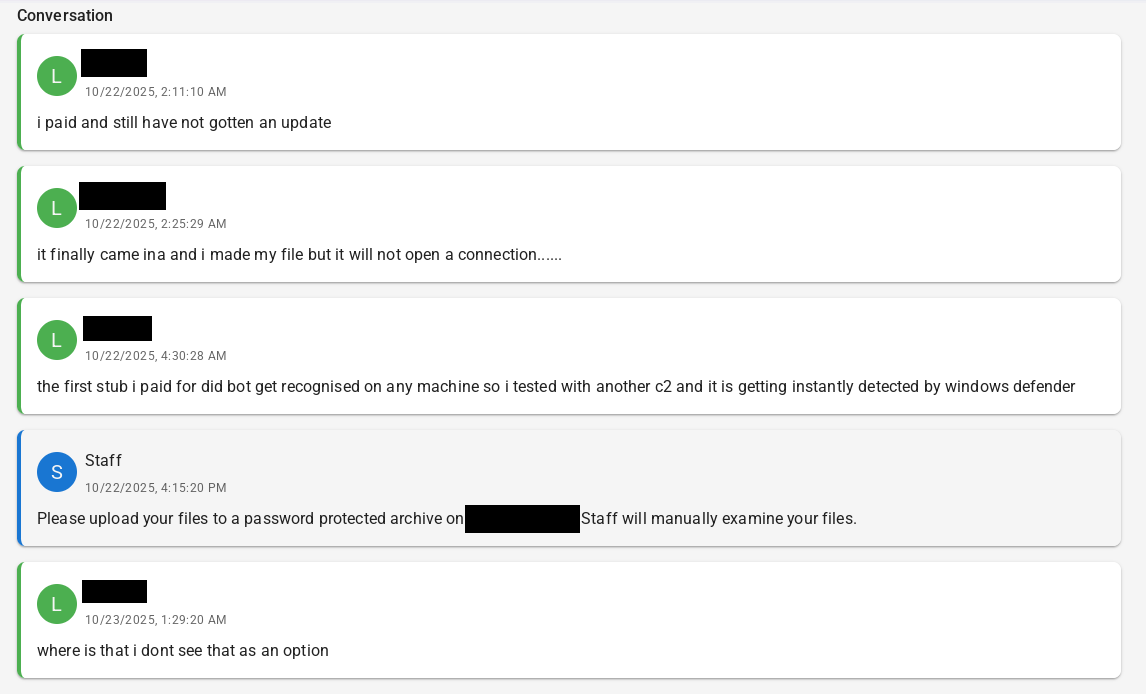
I. The user is shown to be uncooperative with staff when files were requested to verify and resolve claims.
II. Staff quickly responded to the ticket as shown in the timestamps from beginning to end.
III. Our payment processing is automatic and awaits confirmations on the transaction. The user was credited within ~30 minutes of his purchase.
I'm not sure if this is incompetence on behalf of the user, or just behavior of a grifter.
(Oct 22, 2025 09:19 AM)Tyrone Johnson Wrote: You did not provide us with your files in your ticket. Staff will examine your files when we have time. Whenever a runtime detection occurs, it is likely due to user error such as crypting a file that drops detected files or software configuration (uac bypasses or powershell commands being detected). If you have a specific software in mind, we will crypt it and report runtime detections and recommended settings.
i have sent in everything requested, i am waiting for a response to get it fixed
(Oct 22, 2025 08:26 PM)Black Jacket Wrote: i have sent in everything requested, i am waiting for a response to get it fixed
We cannot access your link/file still. Please keep support through our website - this is a sales thread solely.
(Oct 22, 2025 08:32 PM)Tyrone Johnson Wrote: We cannot access your link/file still. Please keep support through our website - this is a sales thread solely.
i was ain a ticket getting help and after i did everything i was told to do my account was logged out and i cant log back in and now i lost $60 do not waste time or money on this scam
(Oct 24, 2025 02:23 PM)Black Jacket Wrote: i was ain a ticket getting help and after i did everything i was told to do my account was logged out and i cant log back in and now i lost $60 do not waste time or money on this scam
Why post misinformation? We never locked your account, or reset your password. At this point, we are most likely going to reserve the right to no longer serve you.
|


