All content is for educational purposes only, information in this thread has been withheld to keep the software in question private.
The Problem
I have got a WaveShare bit of Hardware that I needed to interface with, the joys of China1 means the manual was not that much help, and logical reasoning didn't get me that far. So we're going to fast forward some level of headache, but the long and the short of it is, I am connecting a sensor to the Input side, and I want to use ModBus to query the input status, and have the Relay on the other side go High2. Back on the fact the manual wasn't much help, and not wanting to write my own ModBus communication client to just configure the hardware, I was told that we needed to purchase the software in the manual and on the website of the software in question, but of course we're on HackForums, so you should know by now that's not what I did, so let's get on with the fun times.
Reconnaissance
When you launch specific programs, you can usually tell what programming language they're made in just by their look and feel, or this could just be me. Often .NET Programs have that look and feel about that them where you move the form around and it just kinda slugs, or a C++ Program has that look like the person who wrote it went through the Win32 Message Pump hell to get it to where it is today, and looks and operates good because of it.
Introducing Windowse, in their words - "WinDowse is an extremely convenient tool for obtaining necessary technical information about any window". No this isn't the software I'm talking about, not that cheeky to drop it in casually.
This tool is actually pretty helpful to have in your Swiss Army Knife of tools, even if it is seldom used over other things. Obligatory mention of it's commercial software so ensure you abide by the license and its restrictions.
When focus on the Class Tab and hover the mouse over the target application we did get a handy little mention that tells us what de-compiler we're going to open the target in to have a poke around.

Could you figure it out from that smidge of information? No? I'll give you a hint it isn't any of the numbers... Still no? Well that's okay, it's AfxWnd.
Innocuous? Yes. Revealing? Also yes. Typically VC++ and MFC use Afx as a prefix for things, so that helps a lot to tell me it is not a .NET Application, so we're going to load up Ghidra and start looking.
The Work
Ah, this is where the Pod Racing starts. First we start at the logic step first. Looking for strings relating to our Activation Message, so let's get the software to prompt us for a key, and have a look at what it tells us.
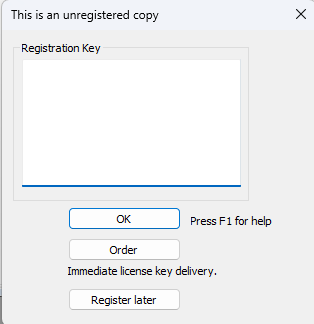
The first instance of redacting had to happen there, the application logo was on the activation screen, hopefully my awesome GIMP skills don't blind you that much, anyway...
That's a pretty standard activation screen, "Give us the Key, you get the Software". Right. Easy. Let's look in Ghidra to see if we can spot anything obvious, such as "Registration Key" as that is the title of the Box, so I'd assume there would be strings with at least "Registration" in the area, if only I knew how right I was before I got side tracked, that of course will be left out for brevity.
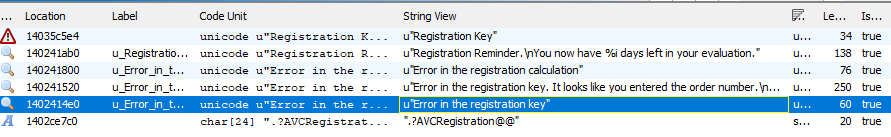
Bonus Quiz moment has been cancelled, the String I am interested in is the highlighted one, this is because I'd hope there is a simple ASM instruction around the code that pushes it to the stack that is checking if the call to the activation method has passed or not.
The pseudo-code from Ghidra comes up with;
That is scarily accurate to what we wanted...
Green Grass
Next time on Dragon Ball Z... Nah, I ain't going to do that to you, but I bet you were worried I was just going to leave it there saying that's what we wanted.
Let's go look into the function "0x1400874b0", and.... wait hold on? Is that a redacted license? It can't be? But the fact there is a reference to Education?
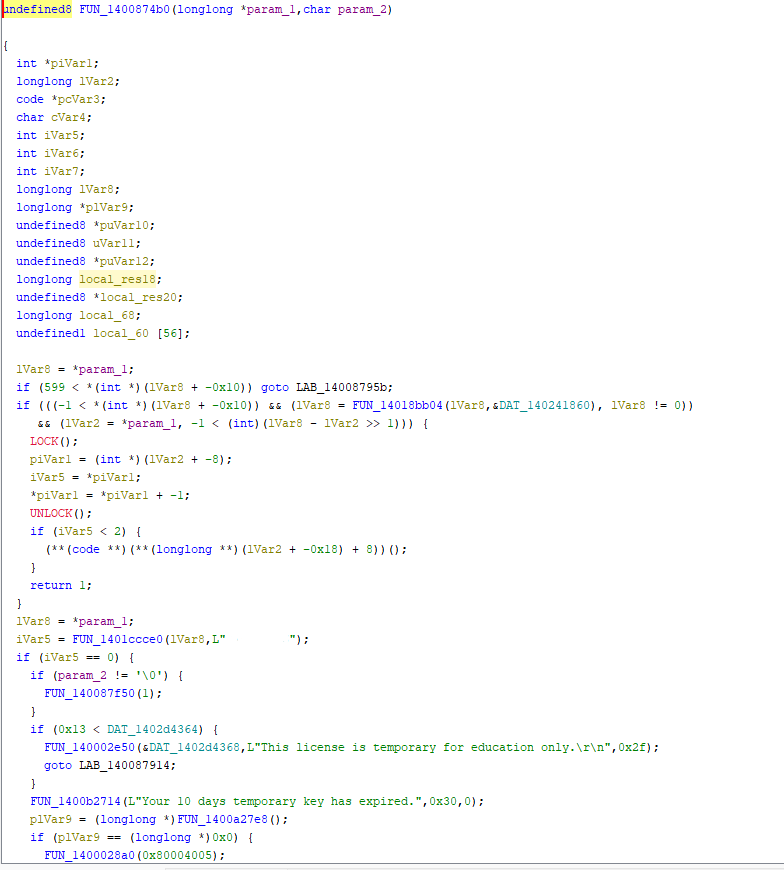
Well before we go off and test it, why does the conditional stuff below it check for a null terminated empty string? Is that just a weird Ghidra quirk or something in this software? I am unsure, not that clever, but we'll see what it's doing before we get too excited, so we'll go look at "140087f50" as I suspect "param_2" is something passed through from the program as if it's "Activated" or some sort of message that is telling the program it needs to check the activation status ofthe program. So we might need to patch it out to ensure we're not getting nagged for an activation code again.
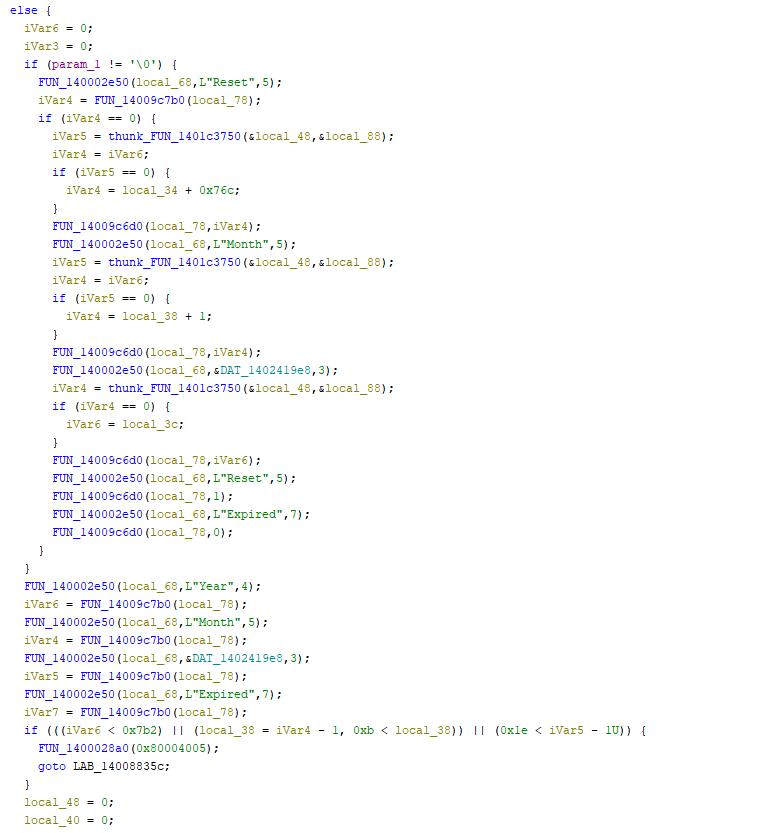
Well, look at that. The spidey-sense of hindsight tingled the way we wanted! That sure looks like a timer check to see if our key is still valid!
Redacted out of this screenshot was the bit about what Registry key it opens, but it's obviously been omitted, so we'll just carry on.
Let's go check out our key in the program;
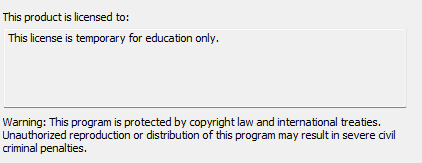
Well fuck, all of that, and to find an educational key in the program? Probably not the first time something like this has happened, but it is one of the easier ways to activate a product without paying...
Last Call
What an odd time, finding a product key just like that off a handful of string searches, weird. But we're not done yet, we need to work out what are the quirks to this new found license that they use an expiry method.
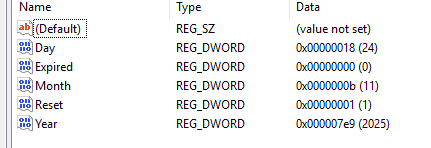
That's what it's in the Registry as of activation, I'll save breaking the thread up with yet another image, and just tell you.
There is a 10 day period at which this license is active, it compares the date in the Registry with what the local PC time is, and I am sure you know where the rest of this goes. We can either change the date in the Registry to be close to us, or change the Expired value from "1" to "0" then change the ACLs only allow Read but no change, then we'll never get the nag again. How good.
Foot Notes
You might wonder why some words are italics, or have a little number after them, this little section will explain some of the words I've elected to use for simplicity, or I just thought it helps flow better to allow you to flick to this to figure out later.
1: China - I acquired the WaveShare hardware through AliExpress, in this instance, I mean cheap, or as with most things from China you're usually left on your own with no technical support from a reputable company. (Or in this instance their wiki was not overly helpful to for finding what I needed.)
2: On/Active - I use this to describe a Binary Truth, it's performing the operation I expect it to, the positive outcome.
I thought I'd use this more, but apparently, I am just lazy.
The Problem
I have got a WaveShare bit of Hardware that I needed to interface with, the joys of China1 means the manual was not that much help, and logical reasoning didn't get me that far. So we're going to fast forward some level of headache, but the long and the short of it is, I am connecting a sensor to the Input side, and I want to use ModBus to query the input status, and have the Relay on the other side go High2. Back on the fact the manual wasn't much help, and not wanting to write my own ModBus communication client to just configure the hardware, I was told that we needed to purchase the software in the manual and on the website of the software in question, but of course we're on HackForums, so you should know by now that's not what I did, so let's get on with the fun times.
Reconnaissance
When you launch specific programs, you can usually tell what programming language they're made in just by their look and feel, or this could just be me. Often .NET Programs have that look and feel about that them where you move the form around and it just kinda slugs, or a C++ Program has that look like the person who wrote it went through the Win32 Message Pump hell to get it to where it is today, and looks and operates good because of it.
Introducing Windowse, in their words - "WinDowse is an extremely convenient tool for obtaining necessary technical information about any window". No this isn't the software I'm talking about, not that cheeky to drop it in casually.
This tool is actually pretty helpful to have in your Swiss Army Knife of tools, even if it is seldom used over other things. Obligatory mention of it's commercial software so ensure you abide by the license and its restrictions.
When focus on the Class Tab and hover the mouse over the target application we did get a handy little mention that tells us what de-compiler we're going to open the target in to have a poke around.
Could you figure it out from that smidge of information? No? I'll give you a hint it isn't any of the numbers... Still no? Well that's okay, it's AfxWnd.
Innocuous? Yes. Revealing? Also yes. Typically VC++ and MFC use Afx as a prefix for things, so that helps a lot to tell me it is not a .NET Application, so we're going to load up Ghidra and start looking.
The Work
Ah, this is where the Pod Racing starts. First we start at the logic step first. Looking for strings relating to our Activation Message, so let's get the software to prompt us for a key, and have a look at what it tells us.
The first instance of redacting had to happen there, the application logo was on the activation screen, hopefully my awesome GIMP skills don't blind you that much, anyway...
That's a pretty standard activation screen, "Give us the Key, you get the Software". Right. Easy. Let's look in Ghidra to see if we can spot anything obvious, such as "Registration Key" as that is the title of the Box, so I'd assume there would be strings with at least "Registration" in the area, if only I knew how right I was before I got side tracked, that of course will be left out for brevity.
Bonus Quiz moment has been cancelled, the String I am interested in is the highlighted one, this is because I'd hope there is a simple ASM instruction around the code that pushes it to the stack that is checking if the call to the activation method has passed or not.
The pseudo-code from Ghidra comes up with;
Code
iVar3 = FUN_1400874b0(&local_res10,1);

    if (iVar3 == 0) {

      pwVar7 = L"Error in the registration key";


      FUN_1400b2714(pwVar7,0x30,0);


      if (DAT_1402d4360 == '\0') goto LAB_140087dd0;

    }
That is scarily accurate to what we wanted...
Green Grass
Next time on Dragon Ball Z... Nah, I ain't going to do that to you, but I bet you were worried I was just going to leave it there saying that's what we wanted.
Let's go look into the function "0x1400874b0", and.... wait hold on? Is that a redacted license? It can't be? But the fact there is a reference to Education?
Well before we go off and test it, why does the conditional stuff below it check for a null terminated empty string? Is that just a weird Ghidra quirk or something in this software? I am unsure, not that clever, but we'll see what it's doing before we get too excited, so we'll go look at "140087f50" as I suspect "param_2" is something passed through from the program as if it's "Activated" or some sort of message that is telling the program it needs to check the activation status ofthe program. So we might need to patch it out to ensure we're not getting nagged for an activation code again.
Well, look at that. The spidey-sense of hindsight tingled the way we wanted! That sure looks like a timer check to see if our key is still valid!
Redacted out of this screenshot was the bit about what Registry key it opens, but it's obviously been omitted, so we'll just carry on.
Let's go check out our key in the program;
Well fuck, all of that, and to find an educational key in the program? Probably not the first time something like this has happened, but it is one of the easier ways to activate a product without paying...
Last Call
What an odd time, finding a product key just like that off a handful of string searches, weird. But we're not done yet, we need to work out what are the quirks to this new found license that they use an expiry method.
That's what it's in the Registry as of activation, I'll save breaking the thread up with yet another image, and just tell you.
There is a 10 day period at which this license is active, it compares the date in the Registry with what the local PC time is, and I am sure you know where the rest of this goes. We can either change the date in the Registry to be close to us, or change the Expired value from "1" to "0" then change the ACLs only allow Read but no change, then we'll never get the nag again. How good.
Foot Notes
You might wonder why some words are italics, or have a little number after them, this little section will explain some of the words I've elected to use for simplicity, or I just thought it helps flow better to allow you to flick to this to figure out later.
1: China - I acquired the WaveShare hardware through AliExpress, in this instance, I mean cheap, or as with most things from China you're usually left on your own with no technical support from a reputable company. (Or in this instance their wiki was not overly helpful to for finding what I needed.)
2: On/Active - I use this to describe a Binary Truth, it's performing the operation I expect it to, the positive outcome.
I thought I'd use this more, but apparently, I am just lazy.