




Dec 3, 2025 09:39 AM
(This post was last modified: Feb 11, 2026 12:25 PM by JoseMar.)
WordPress Elementor CVE-2025-8489
Critical Admin Takeover Vulnerability
Critical Admin Takeover Vulnerability
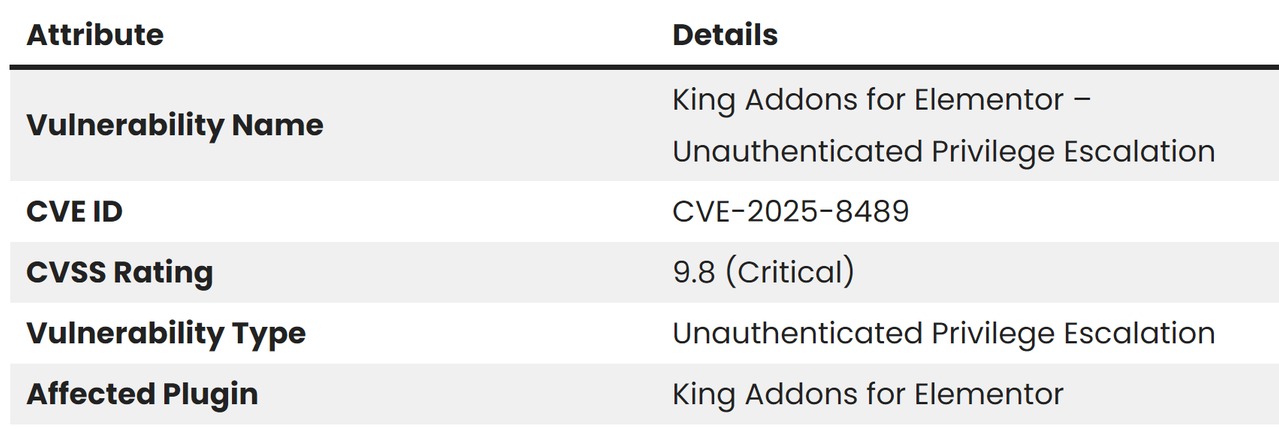
Anyone Else Watching This King Addons Mess?
Honestly, I wasn’t even planning to post today, but this whole King Addons for Elementor thing has me side-eying my installs harder than usual. Like, I know WordPress plugins are basically random loot boxes of “hope this doesn’t nuke your site”, but man, CVE-2025-8489 feels like someone pulled the You Lose Everything card.
I was reading through the notes and, yeah, unauthenticated admin creation. Of course. Because apparently the plugin just kinda shrugs and lets anyone toss “administrator” into a request like it’s ordering a pizza. No login, no proof, just vibes. And with 10k+ installs? Great.
Just check this how stupidly simple the attack is. The hacker can send a crafted request to the WordPress admin-ajax.php endpoint and set the “user_role” field to “administrator” boom. I mean, who thought that was a good idea? Did someone just forget a permission check on a Friday and push it live anyway? I’ve done my share of sloppy deploys, but this is wild.🙄
Attack Traffic Going Nuts🕵️
Wordfence is apparently blocking like 48k+ attempts already, which, okay, impressive numbers I guess, but also terrifying? Especially seeing specific IPs hammering the vuln like they’re trying to speedrun a takeover. 45.61.157.120 pulling almost 30k on its own feels… obsessive.
Kinda makes me think about all the abandoned sites still running version 24.whatever because the owner got bored around 2022 and never logged in again. Those poor things don’t stand a chance. The patch dropped late September 2025, but attackers waited until public disclosure in late October then immediately went feral. Well, still annoying.
If You’re Running This Plugin, Seriously…
Update it. Like now, not “when I have time”. And maybe check your admin list for random “Mario” or whatever. Anyway, I’m curious if anyone here actually saw live exploitation on their logs. I’m half expecting more waves later this month. Or maybe I’m being dramatic, I don’t know. Just feels like one of those things that’s gonna keep popping up in cleanup requests for a while.
Drop your stories if you’ve had to deal with this plugin chaos yet. Might as well compare notes before the next plugin decides to implode.


