Aug 10, 2026 11:17 AM
(This post was last modified: Aug 16, 2026 10:42 AM by •^v^–[ bLacKn3x ]–^v^•.)
SQLiBar – Pentesting & SQLi Firefox Addon
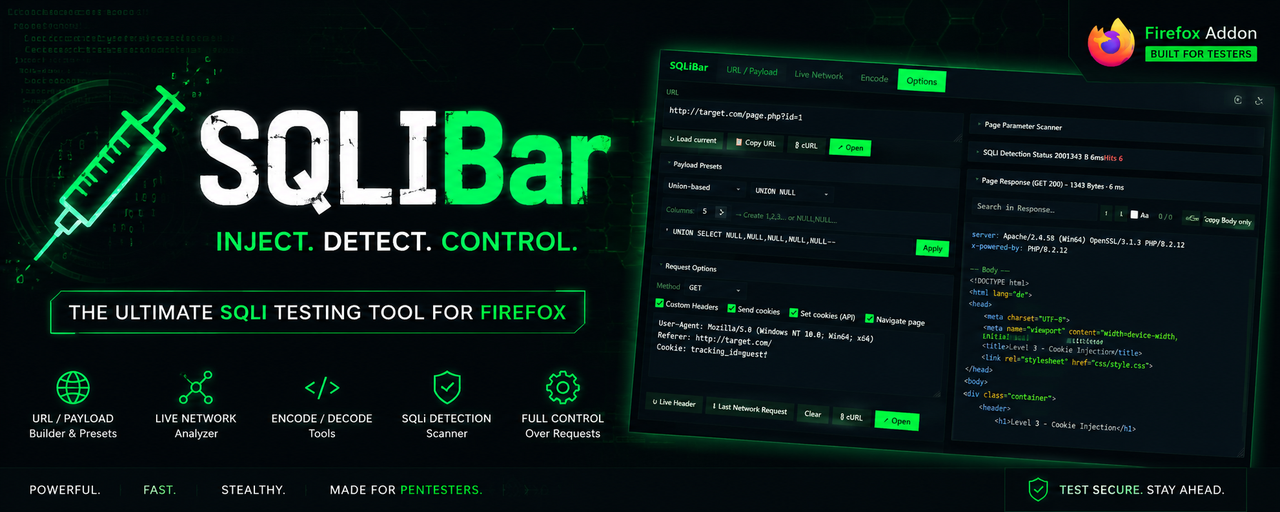
A Developer Tools extension for security testing, real-time SQL injection pattern detection, request manipulation, parameter discovery, advanced payload encoding, and multi-language UI support.
Description
SQLiBar is an advanced web penetration testing tool built into Firefox Developer Tools. Designed for security researchers, penetration testers, and web developers, it streamlines parameter analysis, HTTP request building, SQL injection vulnerability testing, and response inspection directly from your browser.
SQL Injection Detection & Pattern Analysis

Automated response analysis against 100+ database-specific error patterns (MySQL, MariaDB, PostgreSQL, MSSQL, Oracle, SQLite, DB2, Sybase, Access, H2, Firebird, and common ORMs such as PDO, SQLAlchemy, Django, Laravel, Hibernate, Entity Framework, Prisma, and more)
Baseline comparison: set response length and timing baselines to catch subtle anomalies (Boolean-based, Union-based, Error-based, and Time-based indicators)
Reflection detection: highlights payload fragments that appear in the response
Diff view: line-based comparison against the stored baseline body
Visual severity indicators (high / medium / low) with code snippet context for identified error signatures

Header SQLi Mass-Test
One-click batch testing of custom headers for SQL injection
Sends one request per header, injecting the payload into that header only while leaving the rest unchanged
Options: risky only (limit to known high-risk headers such as X-Forwarded-For, Cookie, Authorization, etc.) or test all headers from the textarea
Current payload mode uses your Payload field; otherwise a built-in detection set is used (error-based and time-based probes)
Live progress, abort support, and a results list with status, timing, body size, and badges (`clean` / `HIGH` / `TIME` / `error`)
Load any result back into the tester for manual follow-up

JSON Key SQLi Mass-Test
Automatic SQLi testing of every value in a JSON request body
Walks nested objects and arrays and tests one leaf value at a time
Append mode: the original value is kept and the payload is concatenated — nothing is replaced, and all other fields stay intact
Options: use the current payload or the built-in detection set; optionally restrict to leaf values only
Progress indicator, abort, and a detailed results panel (path, original value, payload, status, timing, badges)
→ Body loads the single injected JSON for that test into the Body field for further manual testing
`Content-Type: application/json` is set automatically when missing

Smart Page Parameter Scanner
Scans the current page DOM to discover form fields, hidden inputs, URL query parameters, link parameters, data-* attributes, and cookies
Instantly push discovered parameters to the URL query, request body, or payload field with a single click

Live Network Capture & Parameter Aggregator
Real-time monitoring and capturing of HTTP / XHR / Fetch requests
Automatic extraction and aggregation of parameters from headers, query strings, URL-encoded bodies, and nested JSON payloads
Inspect raw request/response headers, bodies, and response previews directly
Filter by All / XHR / Documents / POST and search by URL or method
One-click send to Tester, Replay, cURL export, and parameter copy

Payload Presets & Request Manipulation
Built-in payload preset manager with dynamic column generator for UNION-based SQLi tests
Interactive JSON body tree examiner for navigating and selecting deeply nested keys (copy path, push to Payload / URL)
Custom HTTP header injector (X-Forwarded-For, Authorization, custom cookies, Host rewrite, and more)
Method selection (GET, POST, PUT, PATCH, DELETE, HEAD, OPTIONS), body editor, and optional page navigation
One-click cURL export of the current request

Response Viewer
Syntax highlighting for JSON and HTML response bodies
Search within the response (case-sensitive option, next/previous match)
Copy full response or body only

Boolean Blind Mini-Test
A quick True vs False comparison to help spot boolean-based blind SQL injection without leaving the panel.
Sends two requests in sequence: one with a True expression and one with a False expression
Compares status, response length, timing, and a simple body hash
Shows a clear verdict when responses differ (possible boolean-blind) or look the same
Feeds the True response into the existing SQLi detector and response view

Multi-Format Encoder / Decoder
Live preview – encode/decode updates as you type
2-step chain – optional second encoding stage (e.g. URL → Base64 in one step)
Swap Input ↔ Output for rapid multi-pass encoding
Push results directly into Payload, URL, or Request Body
Formats: URL, Double URL, Triple URL, Selective URL (SQLi-focused), Base64, Base64 URL-Safe, Hex (spaced / 0xAABB… / \x.. / 0xAA,0xBB), Binary, ASCII/Decimal, SQL CHA*R(), SQL CHA*R(0x…), SQL CON*CAT(CHAR…), Unicode \u, Unicode %u, Fullwidth Unicode, HTML Entities, JSON, JWT Decode (header / payload / signature), ROT13

Themes & Localization
Multiple built-in color schemes (Neon Green, Cyber Cyan, Violet, Amber, Hot Pink, Electric Blue, Matrix Lime, Mono) plus custom accent color picker
Multi-language interface: English, Deutsch, Español, Français, Português, Русский, 日本語, 中文, Türkçe, العربية (saved preference)

Permissions Justification
devtools: Integrates natively into Firefox DevTools for a seamless workflow
webRequest / cookies / activeTab: Required to capture live network traffic, inspect response headers, inject payload parameters, and manage cookies for security testing
Disclaimer
SQLiBar is strictly intended for authorized security testing, educational purposes, and vulnerability research on systems you own or have explicit permission to test.
https://github.com/blackn3x/SQLIBar
https://addons.mozilla.org/addon/sqlibar/
A Developer Tools extension for security testing, real-time SQL injection pattern detection, request manipulation, parameter discovery, advanced payload encoding, and multi-language UI support.
Description
SQLiBar is an advanced web penetration testing tool built into Firefox Developer Tools. Designed for security researchers, penetration testers, and web developers, it streamlines parameter analysis, HTTP request building, SQL injection vulnerability testing, and response inspection directly from your browser.
SQL Injection Detection & Pattern Analysis
Automated response analysis against 100+ database-specific error patterns (MySQL, MariaDB, PostgreSQL, MSSQL, Oracle, SQLite, DB2, Sybase, Access, H2, Firebird, and common ORMs such as PDO, SQLAlchemy, Django, Laravel, Hibernate, Entity Framework, Prisma, and more)
Baseline comparison: set response length and timing baselines to catch subtle anomalies (Boolean-based, Union-based, Error-based, and Time-based indicators)
Reflection detection: highlights payload fragments that appear in the response
Diff view: line-based comparison against the stored baseline body
Visual severity indicators (high / medium / low) with code snippet context for identified error signatures
Header SQLi Mass-Test
One-click batch testing of custom headers for SQL injection
Sends one request per header, injecting the payload into that header only while leaving the rest unchanged
Options: risky only (limit to known high-risk headers such as X-Forwarded-For, Cookie, Authorization, etc.) or test all headers from the textarea
Current payload mode uses your Payload field; otherwise a built-in detection set is used (error-based and time-based probes)
Live progress, abort support, and a results list with status, timing, body size, and badges (`clean` / `HIGH` / `TIME` / `error`)
Load any result back into the tester for manual follow-up
JSON Key SQLi Mass-Test
Automatic SQLi testing of every value in a JSON request body
Walks nested objects and arrays and tests one leaf value at a time
Append mode: the original value is kept and the payload is concatenated — nothing is replaced, and all other fields stay intact
Options: use the current payload or the built-in detection set; optionally restrict to leaf values only
Progress indicator, abort, and a detailed results panel (path, original value, payload, status, timing, badges)
→ Body loads the single injected JSON for that test into the Body field for further manual testing
`Content-Type: application/json` is set automatically when missing
Smart Page Parameter Scanner
Scans the current page DOM to discover form fields, hidden inputs, URL query parameters, link parameters, data-* attributes, and cookies
Instantly push discovered parameters to the URL query, request body, or payload field with a single click
Live Network Capture & Parameter Aggregator
Real-time monitoring and capturing of HTTP / XHR / Fetch requests
Automatic extraction and aggregation of parameters from headers, query strings, URL-encoded bodies, and nested JSON payloads
Inspect raw request/response headers, bodies, and response previews directly
Filter by All / XHR / Documents / POST and search by URL or method
One-click send to Tester, Replay, cURL export, and parameter copy
Payload Presets & Request Manipulation
Built-in payload preset manager with dynamic column generator for UNION-based SQLi tests
Interactive JSON body tree examiner for navigating and selecting deeply nested keys (copy path, push to Payload / URL)
Custom HTTP header injector (X-Forwarded-For, Authorization, custom cookies, Host rewrite, and more)
Method selection (GET, POST, PUT, PATCH, DELETE, HEAD, OPTIONS), body editor, and optional page navigation
One-click cURL export of the current request
Response Viewer
Syntax highlighting for JSON and HTML response bodies
Search within the response (case-sensitive option, next/previous match)
Copy full response or body only
Boolean Blind Mini-Test
A quick True vs False comparison to help spot boolean-based blind SQL injection without leaving the panel.
Sends two requests in sequence: one with a True expression and one with a False expression
Compares status, response length, timing, and a simple body hash
Shows a clear verdict when responses differ (possible boolean-blind) or look the same
Feeds the True response into the existing SQLi detector and response view
Multi-Format Encoder / Decoder
Live preview – encode/decode updates as you type
2-step chain – optional second encoding stage (e.g. URL → Base64 in one step)
Swap Input ↔ Output for rapid multi-pass encoding
Push results directly into Payload, URL, or Request Body
Formats: URL, Double URL, Triple URL, Selective URL (SQLi-focused), Base64, Base64 URL-Safe, Hex (spaced / 0xAABB… / \x.. / 0xAA,0xBB), Binary, ASCII/Decimal, SQL CHA*R(), SQL CHA*R(0x…), SQL CON*CAT(CHAR…), Unicode \u, Unicode %u, Fullwidth Unicode, HTML Entities, JSON, JWT Decode (header / payload / signature), ROT13
Themes & Localization
Multiple built-in color schemes (Neon Green, Cyber Cyan, Violet, Amber, Hot Pink, Electric Blue, Matrix Lime, Mono) plus custom accent color picker
Multi-language interface: English, Deutsch, Español, Français, Português, Русский, 日本語, 中文, Türkçe, العربية (saved preference)
Permissions Justification
devtools: Integrates natively into Firefox DevTools for a seamless workflow
webRequest / cookies / activeTab: Required to capture live network traffic, inspect response headers, inject payload parameters, and manage cookies for security testing
Disclaimer
SQLiBar is strictly intended for authorized security testing, educational purposes, and vulnerability research on systems you own or have explicit permission to test.
https://github.com/blackn3x/SQLIBar
https://addons.mozilla.org/addon/sqlibar/