Jun 27, 2017 10:34 AM
(This post was last modified: Jun 27, 2017 11:52 AM by Xphile.)
Incident Summary
According to multiple sources, a new variant of Petya ransomware, also known as Petwrap, is spreading rapidly with the help of same Windows SMBv1 vulnerability that the WannaCry ransomware abused to infect 300,000 systems and servers worldwide in just 72 hours last month.
( Source: The Hacker News)
Damages Caused
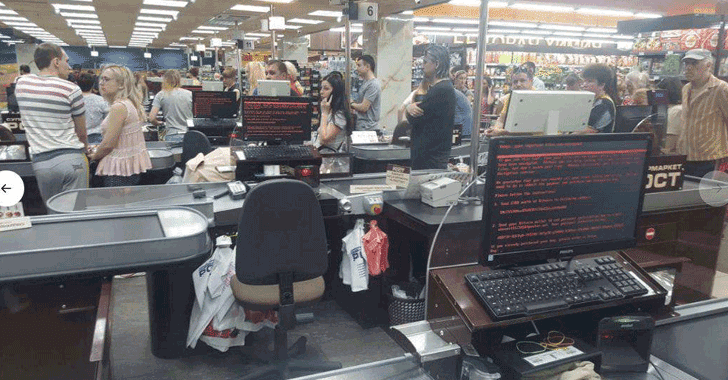
( Above: Supermarket in Kharkiv, East Ukraine)
Petya ransomware has already infected — Russian state-owned oil giant Rosneft, Ukrainian state electricity suppliers, "Kyivenergo" and "Ukrenergo," in past few hours.
Kyivenergo's Press Service Wrote:"We were attacked. Two hours ago, we had to turn off all our computers. We are waiting for permission from Ukraine's Security Service (SBU) to switch them back on"
Additional Information & Further Reading
Petya Ransomware Spreading Rapidly Worldwide, Just Like WannaCry - TheHackerNews
Petya Analysis / Detection Rate - VirusTotal
Petya Ransomware Bitcoin Address - Blockchain
Updates
(Jun 27, 2017 11:20 AM)User1999 Wrote: All those people that paid won't be getting their files back either. The company that the email is associated with shut down the email.
https://posteo.de/blog/info-zur-ransomwa...g-gesperrt
Google translate shows
At noon today we learned that Ransomware blackmail is currently providing a posteo address as a contact option.
Our abuse team checked this immediately - and the mailbox immediately blocked. We do not tolerate any misuse of our platform: The intermittent blocking of abused mailboxes is a normal procedure of providers in such cases. At the time of the blocking, there was no reporting on the Ransomware.
https://mobile.twitter.com/GossiTheDog/s...9015072769
(Jun 27, 2017 11:26 AM)MeanGene69 Wrote: Source email address
The source email address is reported [2] as [email protected] with a filename Order-20062017.doc (RTF із CVE-2017-0199) [3]
Network Indicators of Compromise
The document results in a connection to 84.200.16.242 [3] and specifically /myguy.xls which is an HTA file. This results in connection to french-cooking[.]com. This drops another binary which results in:
111.90.139[.]247 80
COFFEINOFFICE[.]XYZ 80
Thanks for reading. 🤝
Jun 27, 2017 10:36 AM
(This post was last modified: Jun 27, 2017 10:38 AM by Papa Cuda.)
Damn, they've docked quite the profit so far

Went up another $300 in the time it took to post this

again....

Earning for the year 2017:
super spooky
(Jun 27, 2017 10:36 AM)Papa Cuda Wrote: Damn, they've docked quite the profit so far
Went up another $300 in the time it took to post this
2 bitcoins so far, I mean in the time frame maybe that's good but that's like $4,600 right there. Definitely not worth it compared to the severity of the crime. Yes the people behind this are probably well tracked and it's Ukraine so maybe there in a nearby country with non extradition but still. Fuck ransomware lmao
(Jun 27, 2017 10:39 AM)Mr.Peanut Wrote: 2 bitcoins so far, I mean in the time frame maybe that's good but that's like $4,600 right there. Definitely not worth it compared to the severity of the crime. Yes the people behind this are probably well tracked and it's Ukraine so maybe there in a nearby country with non extradition but still. Fuck ransomware lmao
I agree, but I have a feeling in the next 24 hours that it will far surpass 2 BTC.
My guess................
21 BTC
Earning for the year 2017:
super spooky
(Jun 27, 2017 10:36 AM)Papa Cuda Wrote: - snip -
Shows the cost of not patching your machines before exposing them to the damn Internet. 🤦♂
Gonna watch this closely, I'm interested as to how it will playout
Earning for the year 2017:
super spooky
Jun 27, 2017 10:45 AM
(This post was last modified: Jun 27, 2017 10:47 AM by jawsh33.)
Holy. Fuck. This shit is getting out of hand.
I remember making a crypto locker about a year ago, never intended to release it, but completely deleted the source code, because I didn't want to risk anything.
Edit: oh, and targeting supermarkets its fucking stupid, their computers are worth <300 & they have no info on it, it's all usually cloud based db's etc on their software.
Man this shit getting out of hand.
(Jun 27, 2017 10:41 AM)Xphile Wrote: Shows the cost of not patching your machines before exposing them to the damn Internet. 🤦♂
The costs are a lot more than that. Some businesses just adopt a "we will never pay" policy and refuse to foot the bill for company embarrassment.
Jun 27, 2017 10:51 AM
(This post was last modified: Jun 27, 2017 10:56 AM by Xphile.)
(Jun 27, 2017 10:47 AM)Riggs Wrote: The costs are a lot more than that. Some businesses just adopt a "we will never pay" policy and refuse to foot the bill for company embarrassment.
Very true, I assume it's mainly down to goodwill of the company and also the fact that the ransomware has no guarantee of sending a decryption key at all after payment.
I'm sure it's happened in the past where ransomware devs have no intentions of restoring systems after the ransom is paid.
Two more transactions, they've accumulated roughly $ 5,951.78 (2.54183193 BTC) as of now.
Waiting to see how much this grows after 24 hours.
(Jun 27, 2017 10:51 AM)Xphile Wrote: Very true, I assume it's mainly down to goodwill of the company and also the fact that the ransomware has no guarantee of sending a decryption key at all after payment.
I'm sure it's happened in the past where ransomware devs have no intentions of restoring systems after the ransom is paid.
I mean the wannacry dudes seemed to be rather kind. I saw some thing were some guy in some third world country didn't have the money to pay so they gave him a key to unlock his computer anyway.
But yeah I would imagine that's not the case 99% of the time.
Earning for the year 2017:
super spooky
Jun 27, 2017 11:20 AM
(This post was last modified: Jun 27, 2017 11:21 AM by User1999.)
All those people that paid won't be getting their files back either. The company that the email is associated with shut down the email.
https://posteo.de/blog/info-zur-ransomwa...g-gesperrt
Google translate shows
At noon today we learned that Ransomware blackmail is currently providing a posteo address as a contact option.
Our abuse team checked this immediately - and the mailbox immediately blocked. We do not tolerate any misuse of our platform: The intermittent blocking of abused mailboxes is a normal procedure of providers in such cases. At the time of the blocking, there was no reporting on the Ransomware.
https://mobile.twitter.com/GossiTheDog/s...9015072769
Source email address
The source email address is reported [2] as [email protected] with a filename Order-20062017.doc (RTF із CVE-2017-0199) [3]
Network Indicators of Compromise
The document results in a connection to 84.200.16.242 [3] and specifically /myguy.xls which is an HTA file. This results in connection to french-cooking[.]com. This drops another binary which results in:
111.90.139[.]247 80
COFFEINOFFICE[.]XYZ 80
(Jun 27, 2017 11:20 AM)User1999 Wrote: All those people that paid won't be getting their files back either. The company that the email is associated with shut down the email.
https://posteo.de/blog/info-zur-ransomwa...g-gesperrt
Google translate shows
At noon today we learned that Ransomware blackmail is currently providing a posteo address as a contact option.
Our abuse team checked this immediately - and the mailbox immediately blocked. We do not tolerate any misuse of our platform: The intermittent blocking of abused mailboxes is a normal procedure of providers in such cases. At the time of the blocking, there was no reporting on the Ransomware.
https://mobile.twitter.com/GossiTheDog/s...9015072769
Yeah, I was so confused as to why they were using a posteo email adress haha.
So, they're just fucking stupid or what? RIP, this ransomware is fucking retarded.
(Jun 27, 2017 11:20 AM)User1999 Wrote: All those people that paid won't be getting their files back either. The company that the email is associated with shut down the email.
https://posteo.de/blog/info-zur-ransomwa...g-gesperrt
Google translate shows
At noon today we learned that Ransomware blackmail is currently providing a posteo address as a contact option.
Our abuse team checked this immediately - and the mailbox immediately blocked. We do not tolerate any misuse of our platform: The intermittent blocking of abused mailboxes is a normal procedure of providers in such cases. At the time of the blocking, there was no reporting on the Ransomware.
https://mobile.twitter.com/GossiTheDog/s...9015072769
(Jun 27, 2017 11:26 AM)MeanGene69 Wrote: Source email address
The source email address is reported [2] as [email protected] with a filename Order-20062017.doc (RTF із CVE-2017-0199) [3]
Network Indicators of Compromise
The document results in a connection to 84.200.16.242 [3] and specifically /myguy.xls which is an HTA file. This results in connection to french-cooking[.]com. This drops another binary which results in:
111.90.139[.]247 80
COFFEINOFFICE[.]XYZ 80
Thanks for the responses guys, I've added your contributions to the OP. 🤝
|