


Hashcat is a very important password cracking tools out there. It's among the best and fastest tools available. Hashcat uses the GPU on our graphics card for password cracking. Today I'm going to be cracking 3 MD5 hashes and showing you the steps to using Hashcat. I was going to make a whole wordlist for this but changed my mind and decided to just use "Rockyou.txt". For anyone who doesn't know RockYou.txt is a built in dictionary with over 14 million combos. These hashes and passwords were created by my wife. I DO NOT CONDONE HACKING OR ATTEMPTING TO HACK ANYTHING WITHOUT THE OWNERS CONSENT. Lets Begin..
Lets say you have some md5 hashes you need to crack, start by saving these hashes in your "Documents" file. Once you are in Documents you will see the .txt which contains the hashes you want to crack. When your using Hashcat there are some things you will need
1. It's very important you know the type of hashes you are cracking. Are they MD5, SHA, SHA-3 etc etc. In our case i know they are MD5.
2. The types of attacks (dictionary, combinator, brute-force), in our case we will be using dictionary or "straight" mode.
3. The file that contains the hash. I saved mine as "md5hash.txt" see image 1.
4. The wordlist you plan on using. (RockYou.txt or use your own) I'll be using RockYou.txt
5. An output file for your cracked passwords, i will name mine "crackedmd5.txt"
Image 1

Now lets break down the process of using Hashcat. First we need to designate the type of Hash we are cracking (-m) like i said we will be using MD5 (0-Zero). see image 2.
Image 2.

Next we need to designate the type of attack we will use (-a). In our case it will be "straight" mode (0-Zero) see image 3.
Image 3

Now we want to create an output file for our cracked passwords. For this we are going to use (-o) the letter not zero) then the file name we want. In my case i name the file "crackedmd5.txt". Next we will put the file that contains our md5 hashes which i named "md5hash.txt" Lastly we need to add the path to the RockYou.txt dictionary. "usr/share/wordlists/rockyou.txt". Then hit ENTER. See image 4
Image 4

And just like that Hashcat is done, the passwords have been cracked, and it only took a second. see image 5
Image 5

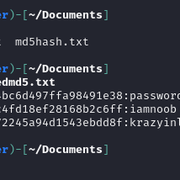
Now our cracked passwords were saved in our Documents and we can run "cat crackedmd5.txt" and look at our passwords. See image 6
Image 6
And that is it!! I will probably create more Threads breaking down different attacks. Thank you for checking out my post. I hope this was informative for the new people who want to see an example of how great hashcat is. Popularity points will help me upgrade grade to UBER. I enjoy reading comments and if you have any questions feel free to ask me. Thank you all for your support.
Lets say you have some md5 hashes you need to crack, start by saving these hashes in your "Documents" file. Once you are in Documents you will see the .txt which contains the hashes you want to crack. When your using Hashcat there are some things you will need
1. It's very important you know the type of hashes you are cracking. Are they MD5, SHA, SHA-3 etc etc. In our case i know they are MD5.
2. The types of attacks (dictionary, combinator, brute-force), in our case we will be using dictionary or "straight" mode.
3. The file that contains the hash. I saved mine as "md5hash.txt" see image 1.
4. The wordlist you plan on using. (RockYou.txt or use your own) I'll be using RockYou.txt
5. An output file for your cracked passwords, i will name mine "crackedmd5.txt"
Image 1
Now lets break down the process of using Hashcat. First we need to designate the type of Hash we are cracking (-m) like i said we will be using MD5 (0-Zero). see image 2.
Image 2.
Next we need to designate the type of attack we will use (-a). In our case it will be "straight" mode (0-Zero) see image 3.
Image 3
Now we want to create an output file for our cracked passwords. For this we are going to use (-o) the letter not zero) then the file name we want. In my case i name the file "crackedmd5.txt". Next we will put the file that contains our md5 hashes which i named "md5hash.txt" Lastly we need to add the path to the RockYou.txt dictionary. "usr/share/wordlists/rockyou.txt". Then hit ENTER. See image 4
Image 4
And just like that Hashcat is done, the passwords have been cracked, and it only took a second. see image 5
Image 5
Now our cracked passwords were saved in our Documents and we can run "cat crackedmd5.txt" and look at our passwords. See image 6
Image 6
And that is it!! I will probably create more Threads breaking down different attacks. Thank you for checking out my post. I hope this was informative for the new people who want to see an example of how great hashcat is. Popularity points will help me upgrade grade to UBER. I enjoy reading comments and if you have any questions feel free to ask me. Thank you all for your support.