 ______________________________________________________________________________________________ 
Disclaimer: This software is only designed to bypass windows defender, no other AVs.
Start Contract
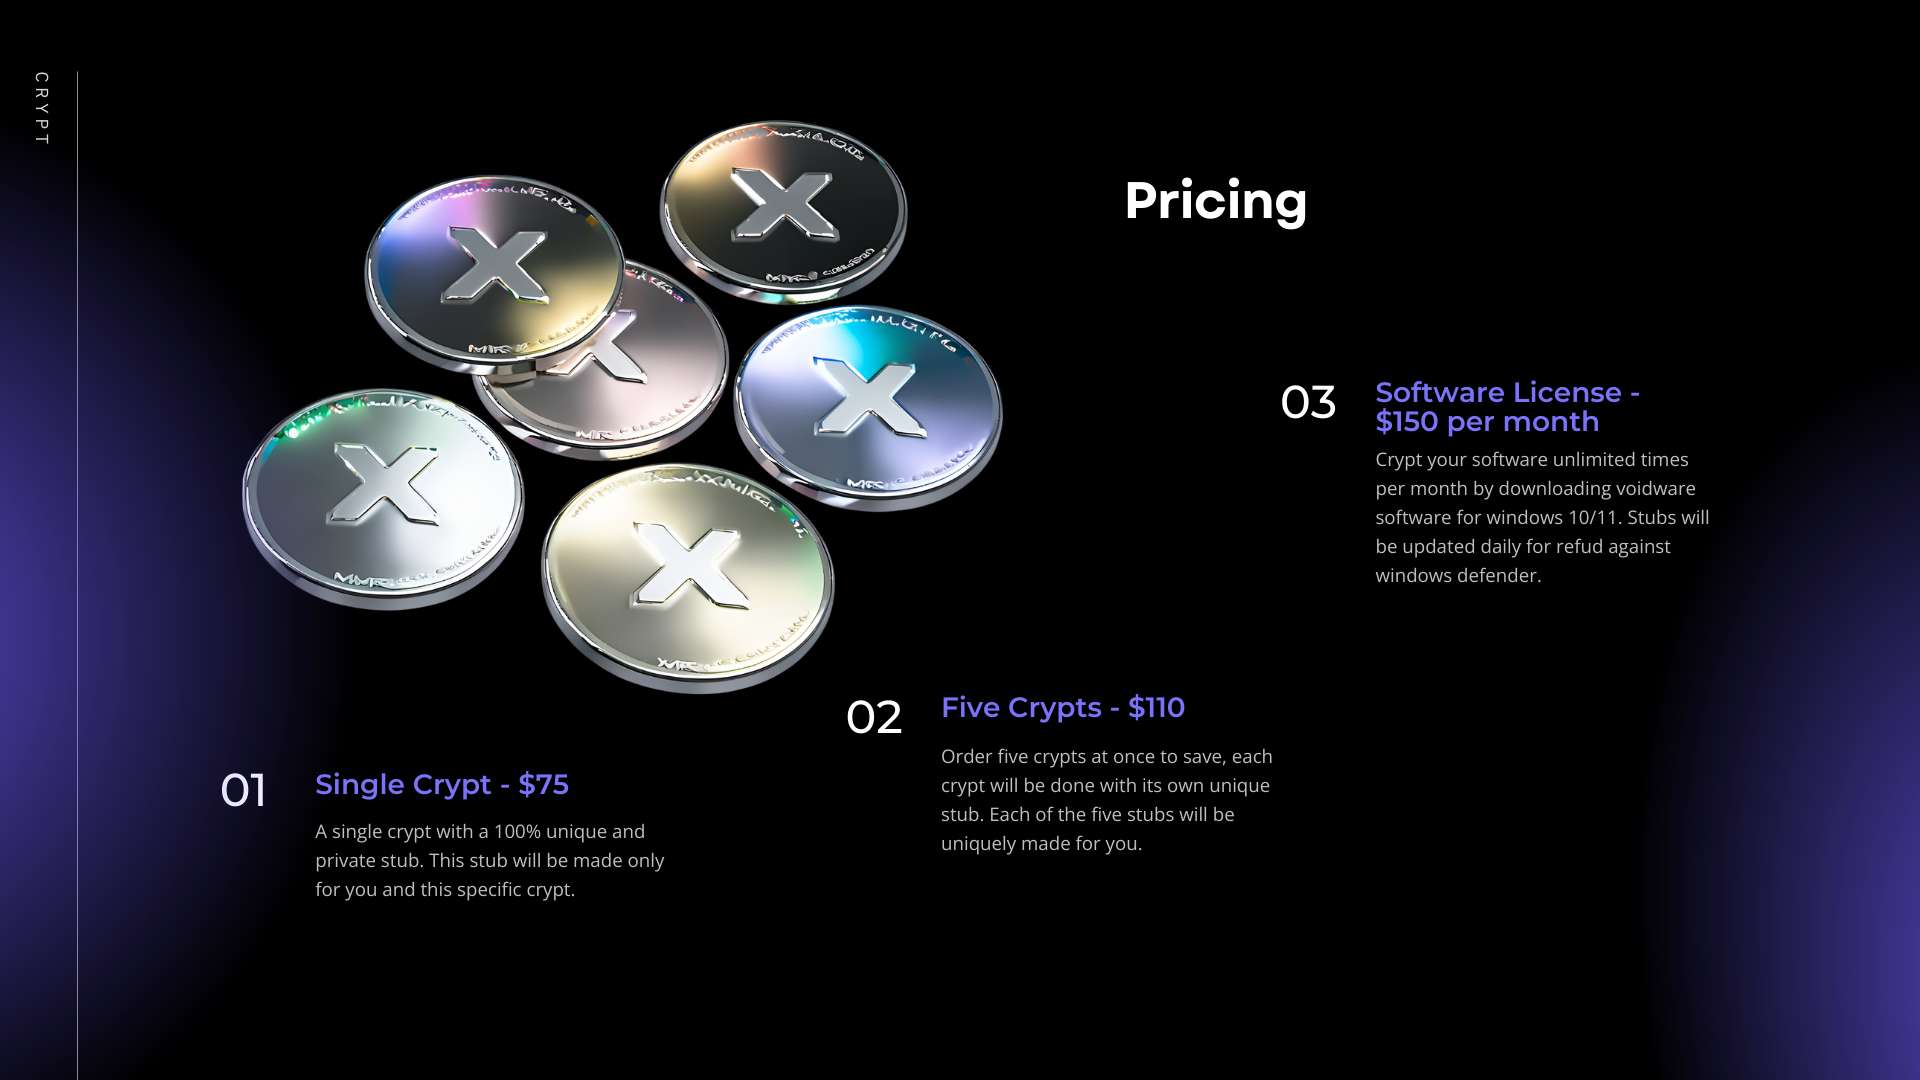
Payments accepted: Most Crypto (XMR Preferred)
Example stub scan:
SCAN
FAQ:
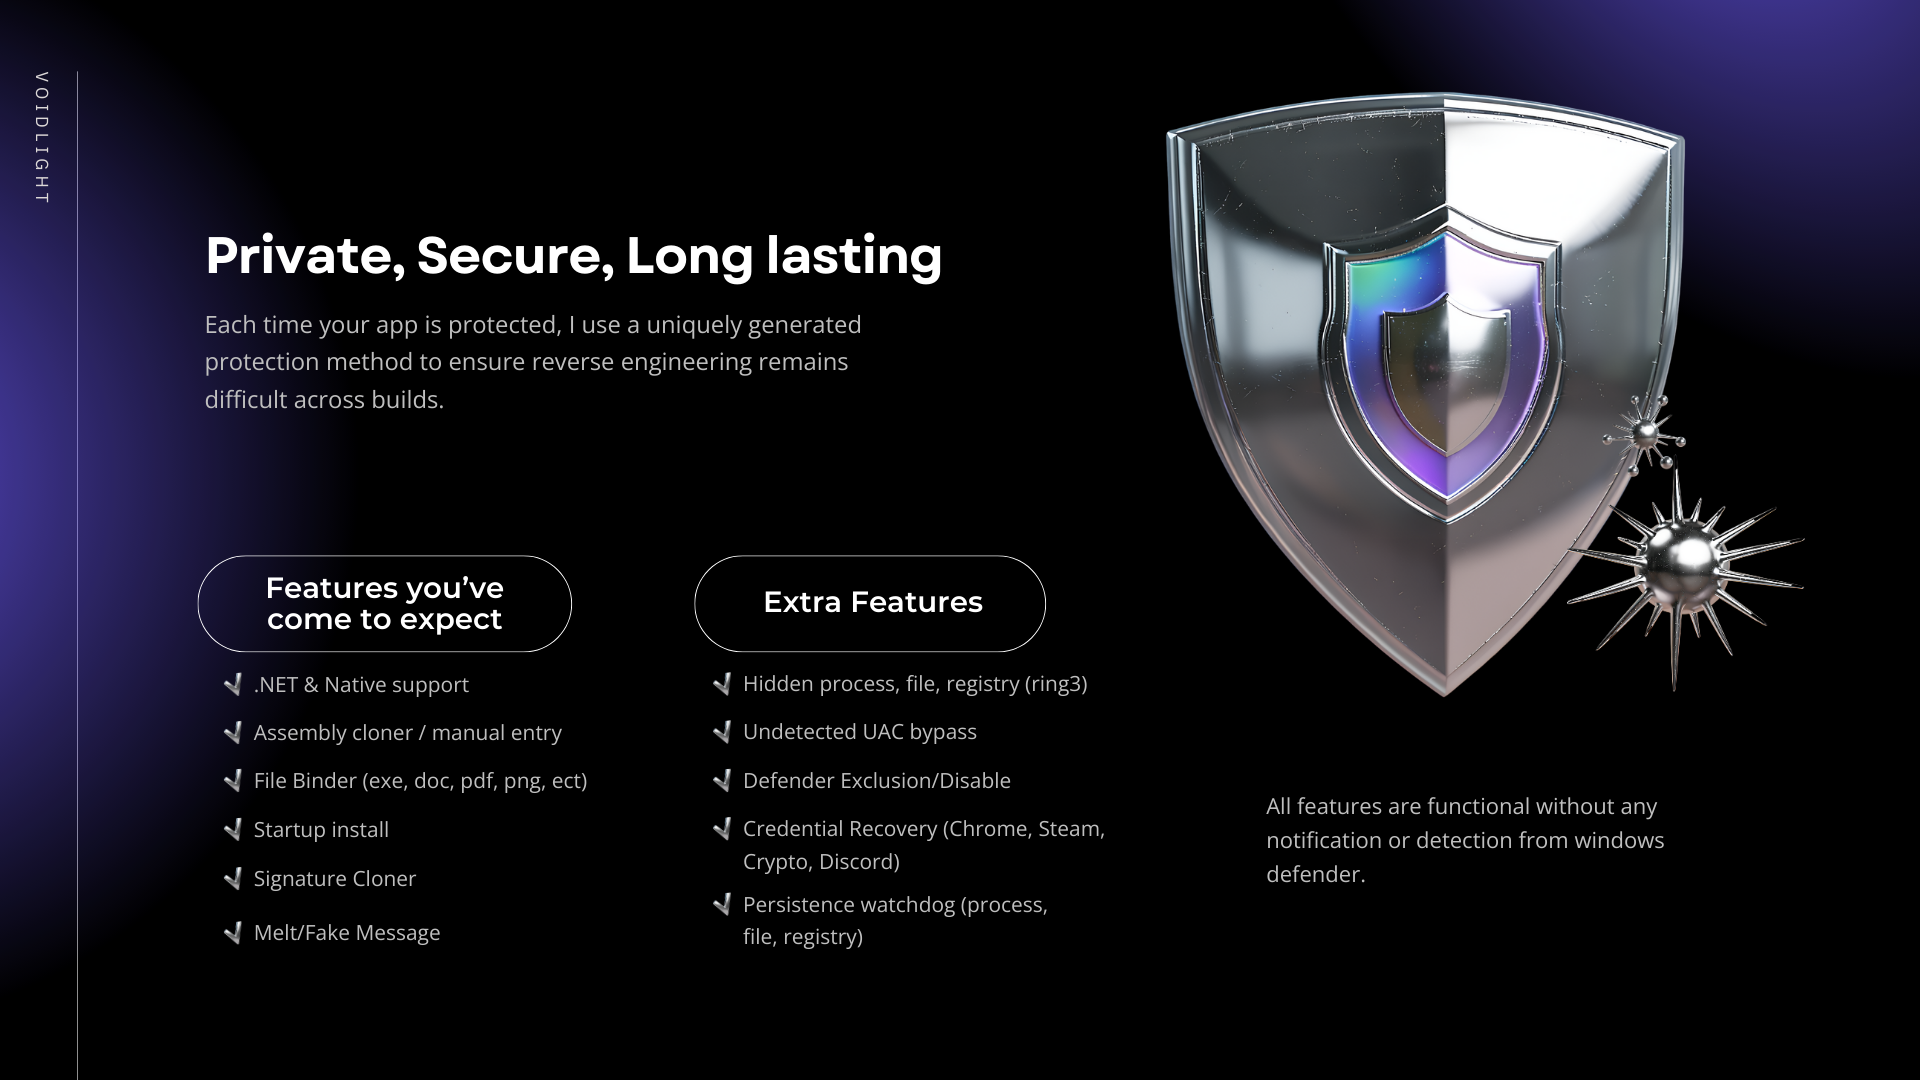
Q: Does the credential recovery execute alongside the crypted app?
A: Yes. credentials will be sent to a discord webhook provided by the user.
Q: Does the ring3 rootkit persist across reboot? How does it work?
A: Yes it does persist across reboots, and runs with system privileges. Any file, process, or registry key containing 'void_' will be hidden from all processes such as task manager, cmd, explorer, sysinternal tools, ect.
Q: Can the bound file be detected?
A: No. Any files bound must be undetected or windows defender will pop up.
Q: Can I use this to spread malware?
A: No. Any mention of spreading, malware, banking trojans, ransomware, or slaves/victims will result in termination of the license agreement. This software is to be used on machines you own or have consent to operate.
License Agreement:
- The sharing of your license is strictly prohibited.
- Encrypting a file will result in the deduction of 1 credit. It is important to note that any errors in configuration or encryption of an incorrect file shall not warrant a refund of the deducted credits.
- You acknowledge this is a Windows Defender Bypass, all other AVs are not prioritized.
- Scanning must take place only within allowed AVs. Scanning on any site that distributes samples is prohibited.
- The utilization of this sales thread for support purposes is not permitted.
- Encryption of files belonging to parties other than yourself is prohibited.
- Use of the product on more than one device simultaneously is prohibited.
- I do not provide a guarantee for the recovery of accounts lost by users.
- Hardware identifier (HWID) resets are offered at no cost provided they are not exploited.
- All transactions are final, and no refunds will be issued.
- Usage of this product with illegal files, such as ransomware or banking trojans, is strictly prohibited.
- This software may be used in conjunction with a remote administration tool under specific circumstances:
-- To monitor employees, children, or manage personal computers.
-- To conduct system audits on networks or individual systems.
- It is prohibited to monitor or execute the crypt on any system without obtaining prior written consent.
- Users are prohibited from causing damage or rendering systems inaccessible.
- Accessing personal accounts on monitored systems that do not belong to you is strictly prohibited.
- Prior to utilizing this product, users are advised to consult their local laws.
- Violation of these Terms of Service will result in termination of the license agreement.
I will be giving out some vouch crypts to Ub3r members only, if they agree to write a review of the product.
DO NOT DEAL WITH THIS MEMBER
Id like to recieve the vouch copy please dm me, ill write a review of product.
(Feb 5, 2025 07:27 AM)Py_Dev Wrote: Id like to recieve the vouch copy please dm me, ill write a review of product.
sent you a message bro
DO NOT DEAL WITH THIS MEMBER
This is new in the market.
Would you be willing to share a vouch copy ?
I work with RATs / Botnets mostly and I can definitely do a through product review for others to see.
DO NOT DEAL WITH THIS MEMBER
(Feb 5, 2025 07:27 AM)Py_Dev Wrote: Id like to recieve the vouch copy please dm me, ill write a review of product.
You are begging for vouch copies everywhere. Have you ever wondered to support a seller and buy a product?
DO NOT DEAL WITH THIS MEMBER
(Feb 6, 2025 12:59 AM)Jebac Wrote: You are begging for vouch copies everywhere. Have you ever wondered to support a seller and buy a product?
Please read the bottom his his thread.
I would like to receive the voucher copy, please send it to me via DM. I’ll make sure to write a review of the product.
Hello, can you check my last message?
|


