Mar 13, 2025 05:12 AM
(This post was last modified: Jun 30, 2025 03:45 PM by JoseMar.)
North Korean Hackers Spreading DocSwap Malware
Disguised as a Security Document Viewer
Disguised as a Security Document Viewer
A modern malware campaign focusing on portable clients in South Korea has been revealed, with clear joins to North Korean danger actors.
The pernicious application is disguised as a “Document Seeing Confirmation App.”
This malevolent app was recognised through VirusTotal on January 21, 2025, and has effectively taken delicate data from compromised devices.
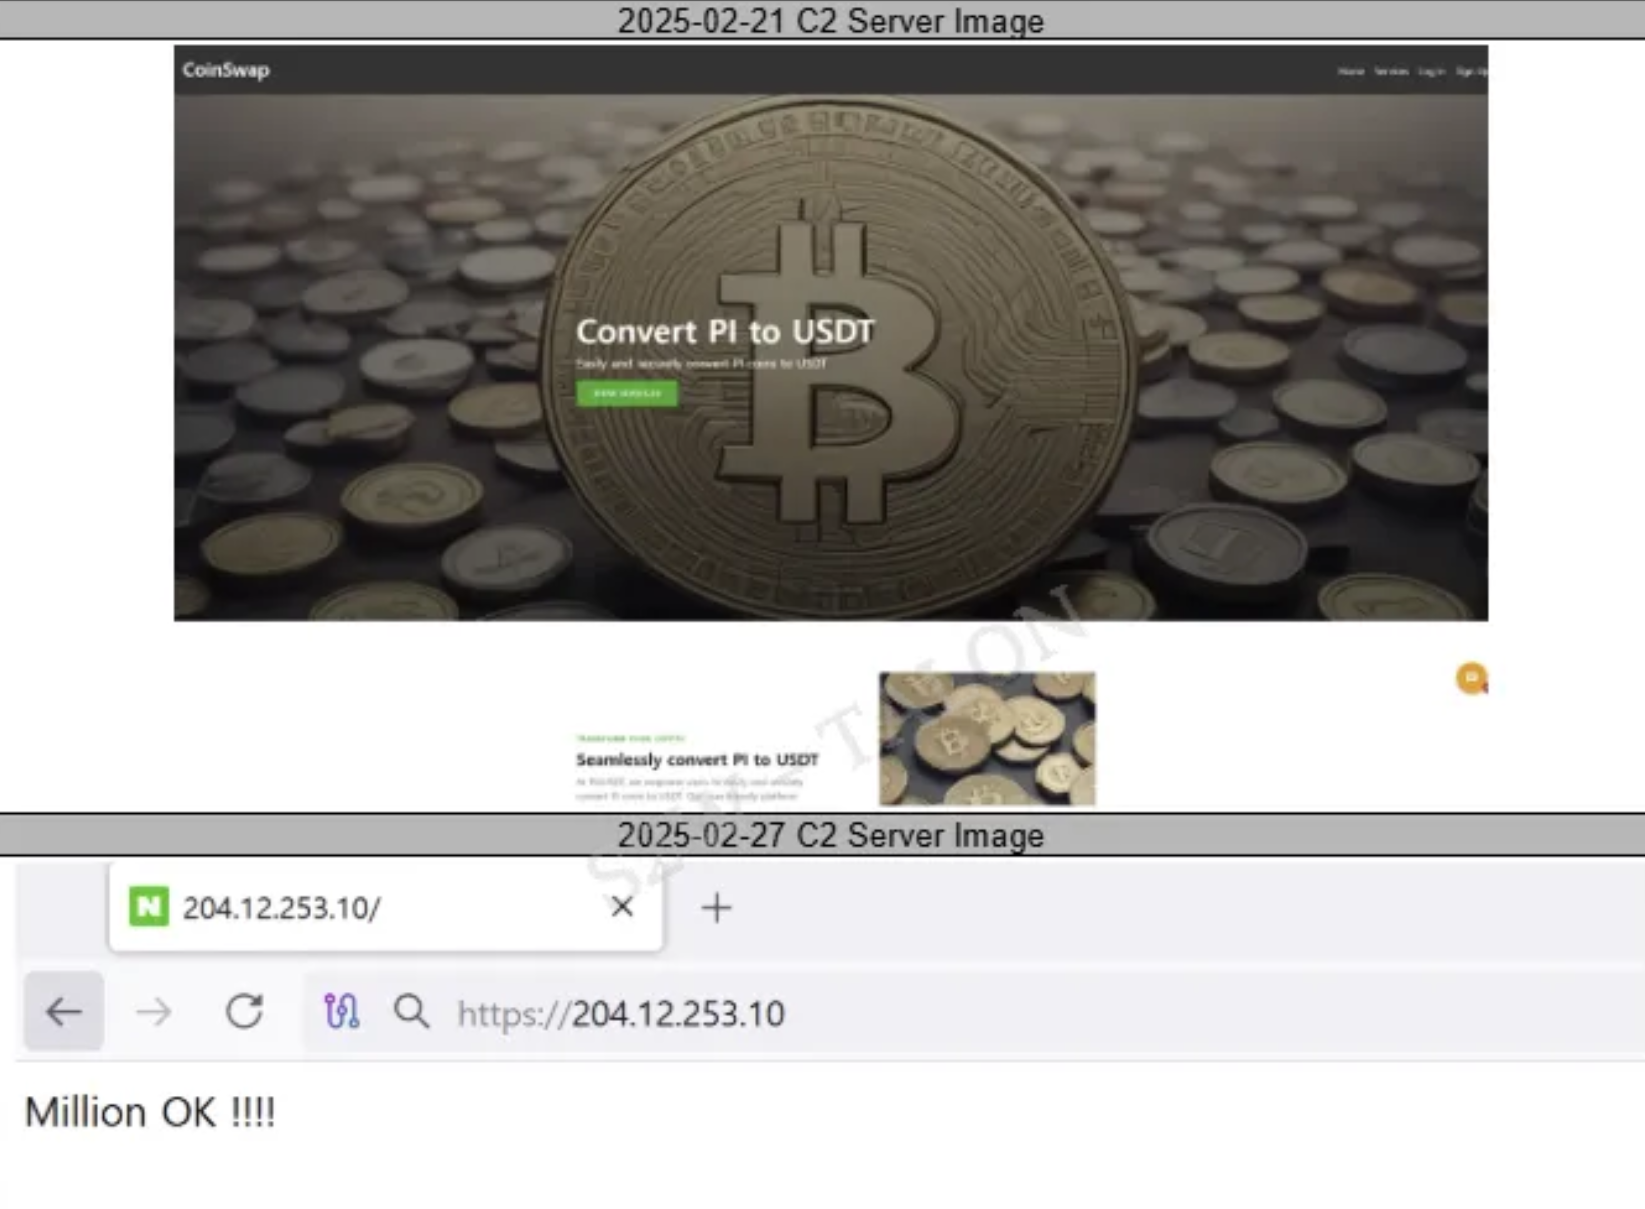
The S2W Danger Investigate and Insights Center analysts identified the malware, which they named “DocSwap”, after finding a phishing page mimicking CoinSwap at the command and control infrastructure.
The analysts know that the pernicious app was malicious on December 13, 2024, and speaks to an already unidentified risk mainly planned to target South Korean users.
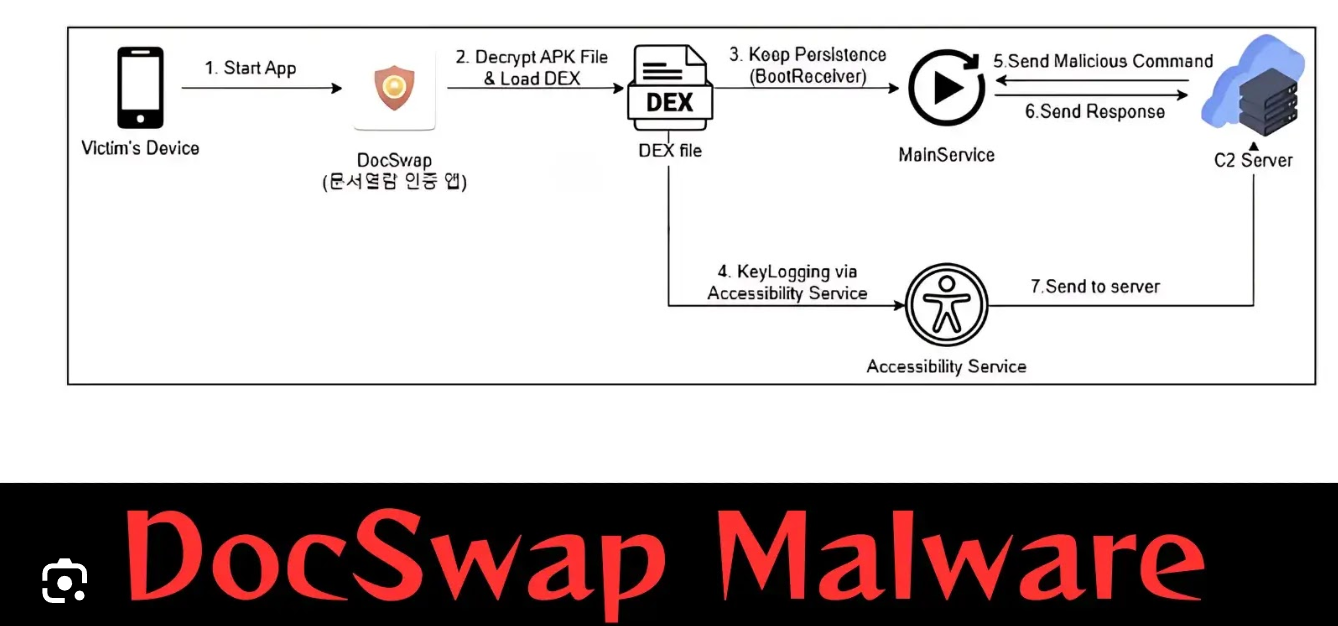
The advanced malware utilises a multi-stage disease preparation that starts with decoding a muddled record inside the package.
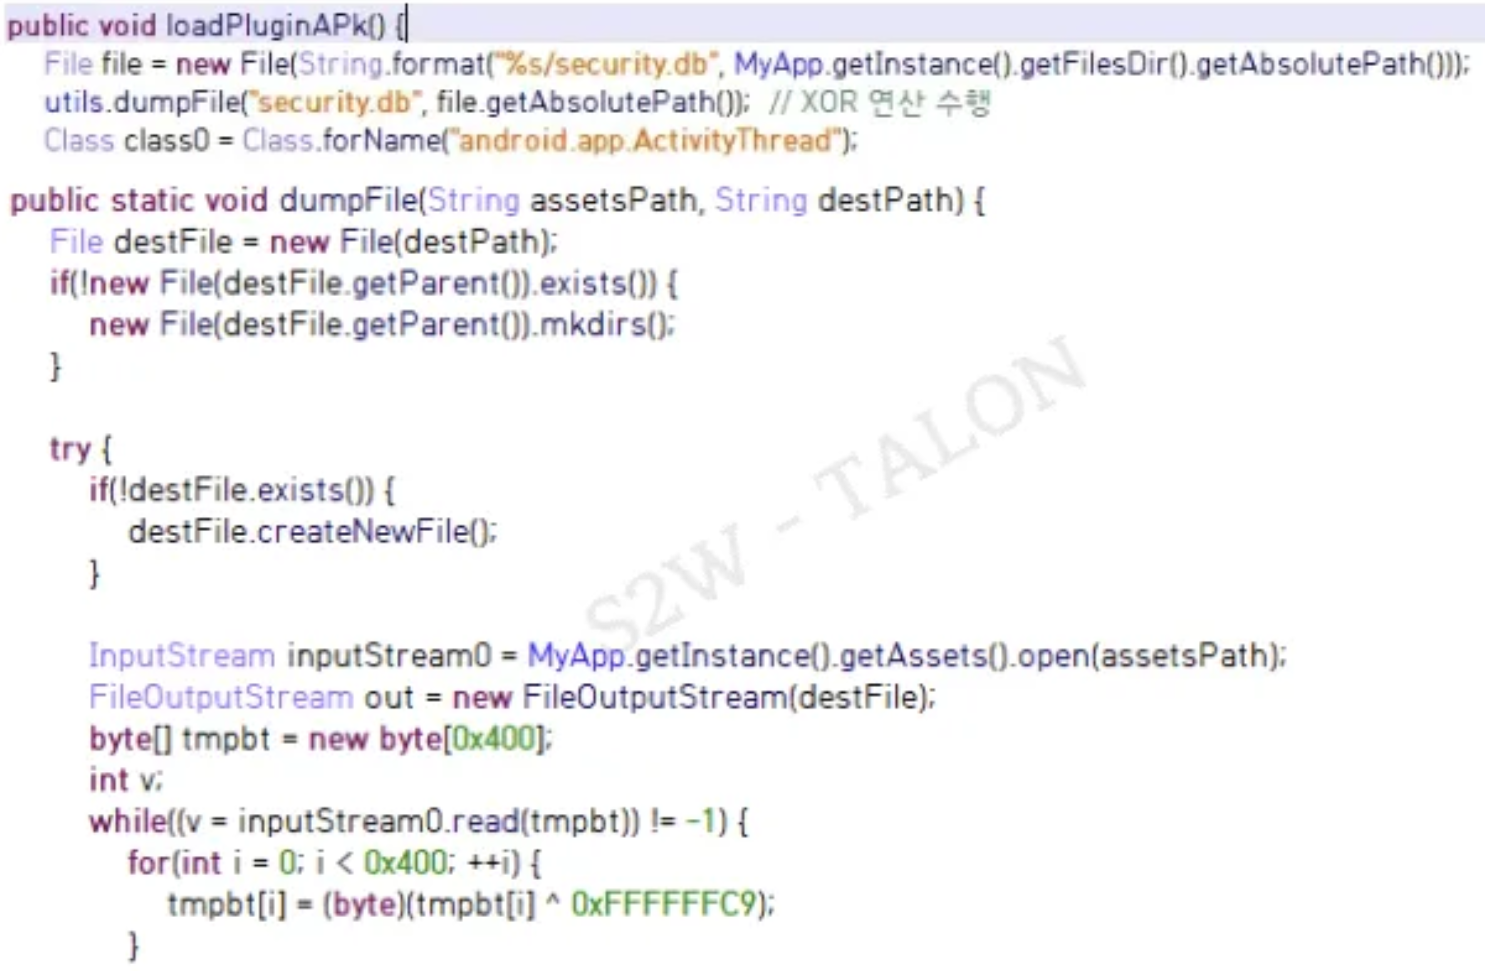
“The malicious app performs an XOR (0xCC) operation on the ‘security.db’ file in a subdirectory, which drops an APK file and loads the DEX file stored within it,” clarified the report enumerating the threat.
The decryption of the security.db Record
It diligently creates notices inquiring clients to empower openness administrations with messages like “To guarantee legitimate usefulness, it would be ideal if you empower availability permissions.”
The application guarantees determination by enrolling for boot-related bury counting BOOT_COMPLETED, ACTION_POWER_CONNECTED, and ACTION_POWER_DISCONNECTED, permitting it to survive gadget restarts.
It employs the StartForeground API to keep a consistent nearness with notices expressing “Tap to see more points of interest or halt the app.”
Technical Capabilities and Command Structure
DocSwap communicates with a hardcoded command and control server at 204.12.253[.]10:6834, I would like to talk through an advanced command structure.
The malware supports 57 commands, enabling extensive surveillance and data exfiltration capabilities.
Key components of the decryption mechanism reveal the attackers techniques:
Code
public static void dumpFile(String assetsPath, String destPath) {

    File destFile = new File(destPath);

    if(!new File(destFile.getParent()).exists())

        new File(destFile.getParent()).mkdirs();

    try {

        if(!destFile.exists())

            destFile.createNewFile();

        InputStream inputStream0 = MyApp.getInstance().getAssets().open(assetsPath);

        FileOutputStream out = new FileOutputStream(destFile);

        byte[] tmpbt = new byte[0x400];

        int v;

        while((v = inputStream0.read(tmpbt)) != -1) {

            for(int i = 0; i < 0x400; ++i) {

                tmpbt[i] = (byte)(tmpbt[i] ^ 0xFFFFFFFC9);

            }

            out.write(tmpbt, 0, readCount);

        }
Malicious App Execution Process
This captured information is transmitted to a Command and Control (C2) server and moreover put away locally utilizing a organized path:
Code
/data/data/com.security.library/Security/download_{dd-mm-yyyy}.datCybersecurity firm S2W has credited this campaign to a North Korean risk performing artist, puNK-004, citing foundation likenesses with past operations by the Kimsuky group.
Security analysts unequivocally exhort caution when introducing portable applications, particularly those asking availability authorizations or posturing as archive confirmation apparatuses from unsubstantiated sources.
Don´t forget to update and stay safe!🕵️
Additional sources to explore: You can also search directly by CVE on Google for more information: