





Mar 18, 2025 05:05 PM
(This post was last modified: Jun 30, 2025 03:45 PM by JoseMar.)
New BitM Attack Allows Hackers to
Hijack User Sessions in Seconds
Hijack User Sessions in Seconds
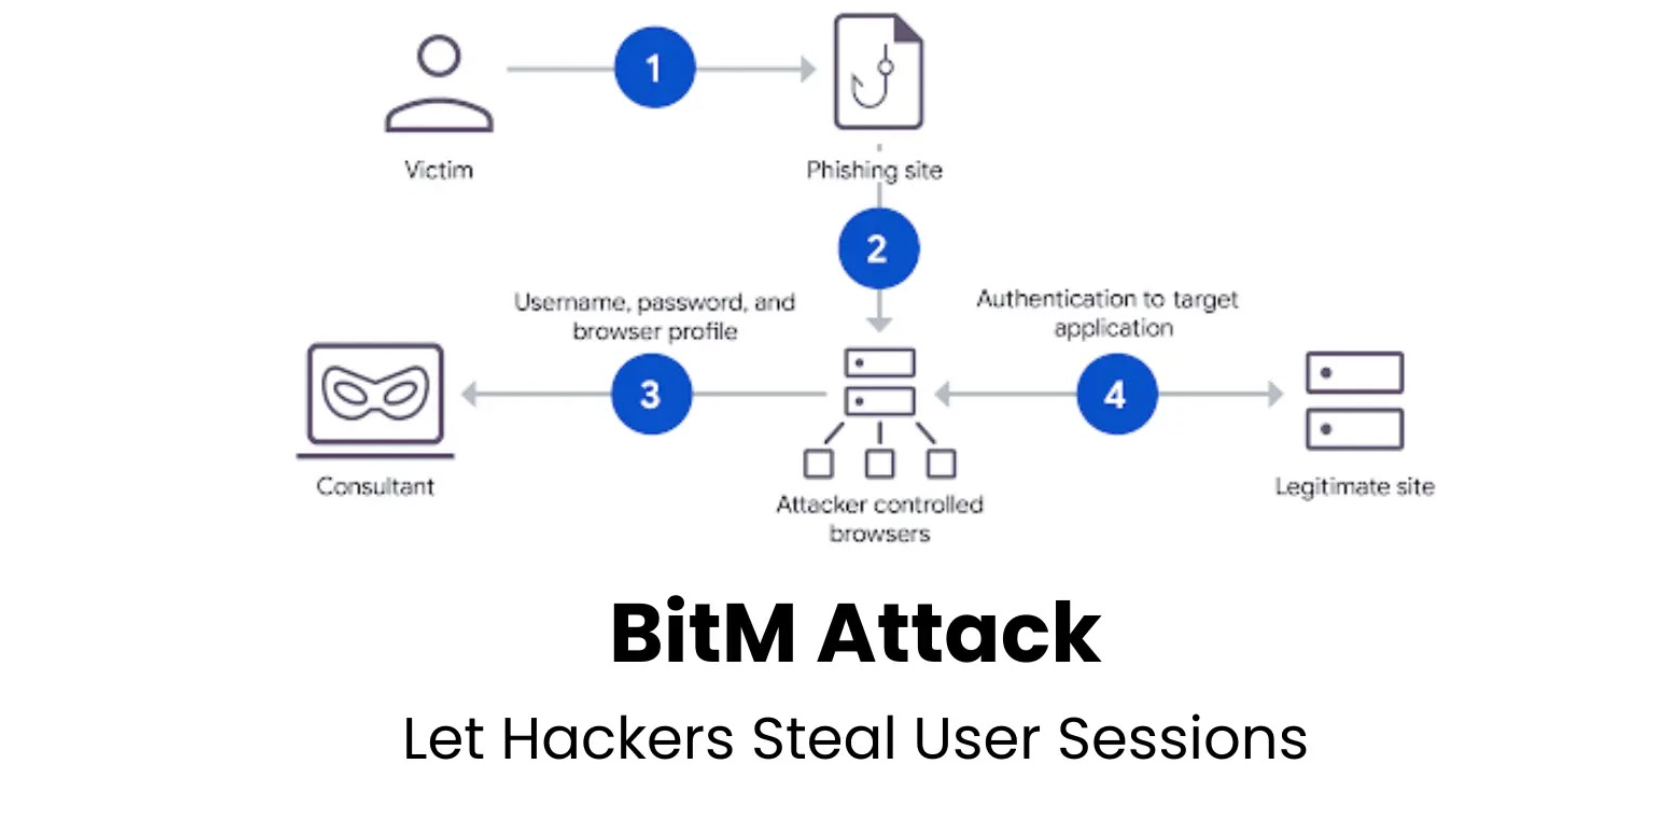
A modern cyberattack procedure known as Browser-in-the-Middle (BitM) has developed, empowering programmers to bypass multi-factor confirmation (MFA) and take client sessions in insignificant seconds.
This strategy abuses web browser functionalities to seize confirmed sessions, posing a critical risk to organizations depending on conventional security measures.
BitM assaults imitate blue browsing encounters by directing casualties through an attacker-controlled browser. When clients visit a pernicious site or take after a phishing interface, their intelligence is funneled through a proxied browser facilitated on the attacker’s server.
This browser mirrors the appearance of the actual blue location, deceiving casualties into entering accreditations and completing MFA challenges. Once confirmed, the assailant captures the session token put away in the browser, viably taking the user’s confirmed state.
Key Components of BitM:
- Transparent Intermediaries: Apparatuses like Evilginx2 or Daydream (Mandiant’s inside instrument) act as middle people between the casualty and the target benefit. These intermediaries alter HTTP reactions to supplant actual blue spaces with phishing spaces, empowering session token extraction.
- Rapid Arrangement: Unlike straightforward intermediaries requiring broad customization, BitM systems like Daydream permit administrators to target any site rapidly. Highlights such as Firefox profile capacity and programmed stack adjusting rearrange large-scale phishing campaigns.
- Real-Time Observing: Aggressors can watch casualty intelligence in real-time, empowering quick session burglary upon fruitful authentication.

This strategy is viable against applications utilizing virtual desktop frameworks (VDI) or cloud administrations, where session seizing can give an advantage to advantaged networks.
- Corporate Security Dangers:
- Speed and Adaptability:
While no framework is entirely invulnerable, organizations can moderate BitM dangers through layered security:
- Hardware-Based MFA (FIDO2): Security keys like YubiKey or Google Titan uphold cryptographic challenges tied to particular spaces. Aggressors cannot replay FIDO2 reactions over distinctive websites, stopping BitM attacks.
- Client Certificates: Official confirmation of device-specific certificates avoids session reuse on unauthorized gadgets. This strategy complements FIDO2 to piece token hijacking1.
- Behavioral Observing: Instruments that distinguish bizarre login designs or browser unique mark disparities can hail potential BitM compromises.
- Security Mindfulness Preparing: Teaching clients to recognize phishing endeavors (e.g., suspicious URLs or spontaneous confirmation demands) remains critical1.
Don´t forget to update and stay safe!🕵️
Additional sources to explore: You can also search directly by CVE on Google for more information:
