





Mar 20, 2025 03:05 AM
(This post was last modified: Jun 30, 2025 03:41 PM by JoseMar.)
New ClearFake Variant Uses Fake reCAPTCHA to Deceive Users
and Deploy Malicious PowerShell Code
and Deploy Malicious PowerShell Code
ClearFake, a noxious JavaScript system recognized in July 2023, has advanced with advanced unused social building tactics.
Originally planned to show fake browser overhaul pages, the system has experienced critical improvements, joining more progressed duplicity procedures to convey malware through compromised websites.
The most recent variation, found in December 2024, utilizes fake reCAPTCHA or Cloudflare Gate confirmation challenges to trap clients into executing noxious PowerShell code.
This speaks to a critical advancement from prior forms that depended on fake browser updates.
Sekoia examiners found that this unused variation utilizes the “EtherHiding” strategy but has presented extra intelligence with the Binance Shrewd Chain.
The system sends different JavaScript codes and assets that uniquely finger impression victims’ frameworks, which have recently been downloading, decoding, and showing beguiling lures.
When clients visit a compromised site, they experience a starting script that loads Web3 libraries and starts communication with the Binance Shrewd Chain.
The pernicious code is concealed inside keen contracts, making the investigation more troublesome and expulsion incomprehensible due to the unchanging nature of blockchain data.
Installation stream
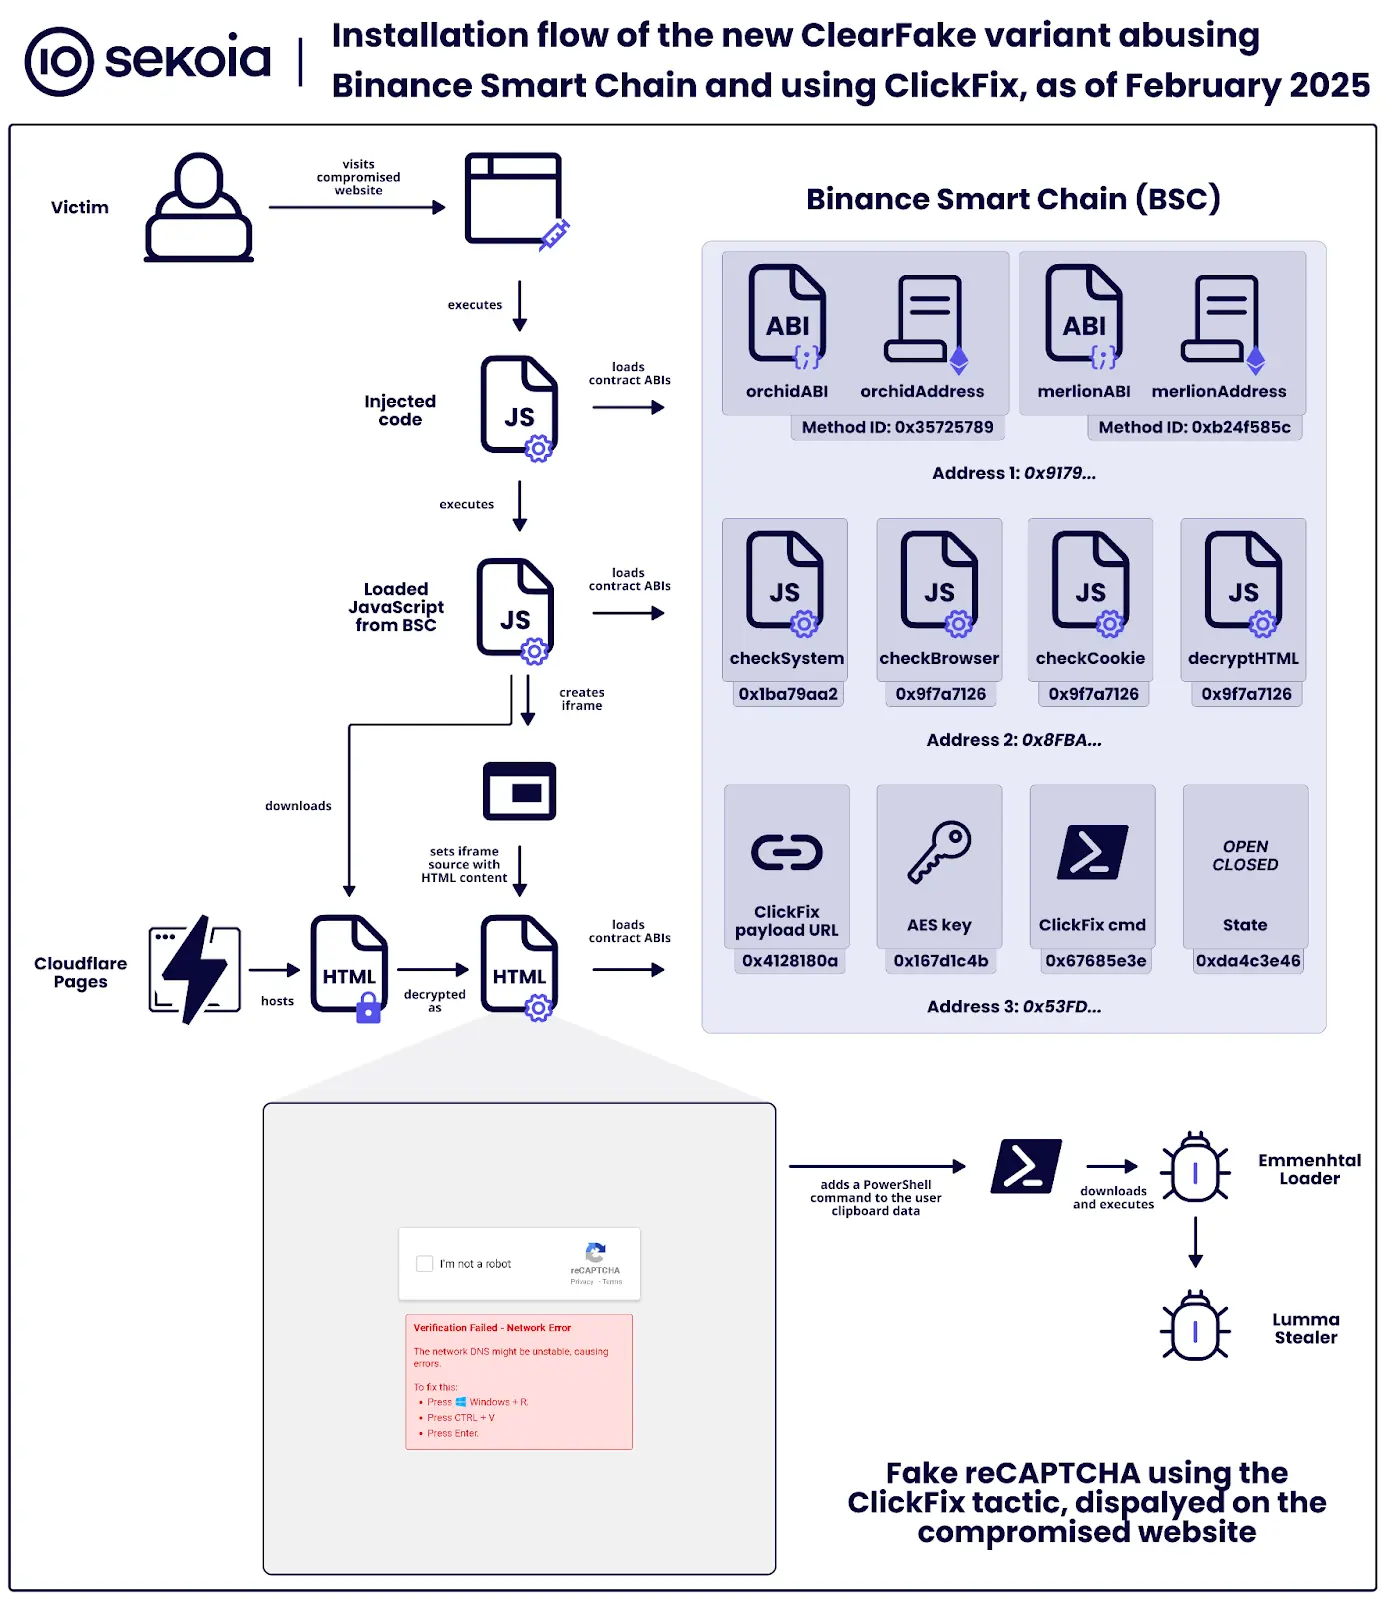
The disease stream starts with infused JavaScript on compromised websites, which recovers noxious code from blockchain-savvy contracts, eventually driving the show of fake security challenges.
Attack Analysis
The assault begins with a brief JavaScript code infused into compromised websites (generally WordPress destinations), which loads genuine conditions like web3, pako, and crypto-js.
This beginning script interatomic with shrewd contracts at wallet addresses like 0x9179dda8B285040Bf381AABb8a1f4a1b8c37Ed53 to recover and execute extra code segments.
The malware employs compressed and base64-encoded information that must have been unscrambled in recent execution.
The ClickFix draws displayed to clients incorporate a fake Cloudflare Entryway confirmation that claims to distinguish “unusual web traffic” or a fake reCAPTCHA challenge near a DNS mistake message.
Both draw educated clients to open the Run command (Win+R) and execute a PowerShell command naturally replicated to their clipboard.
ClickFix baits utilized
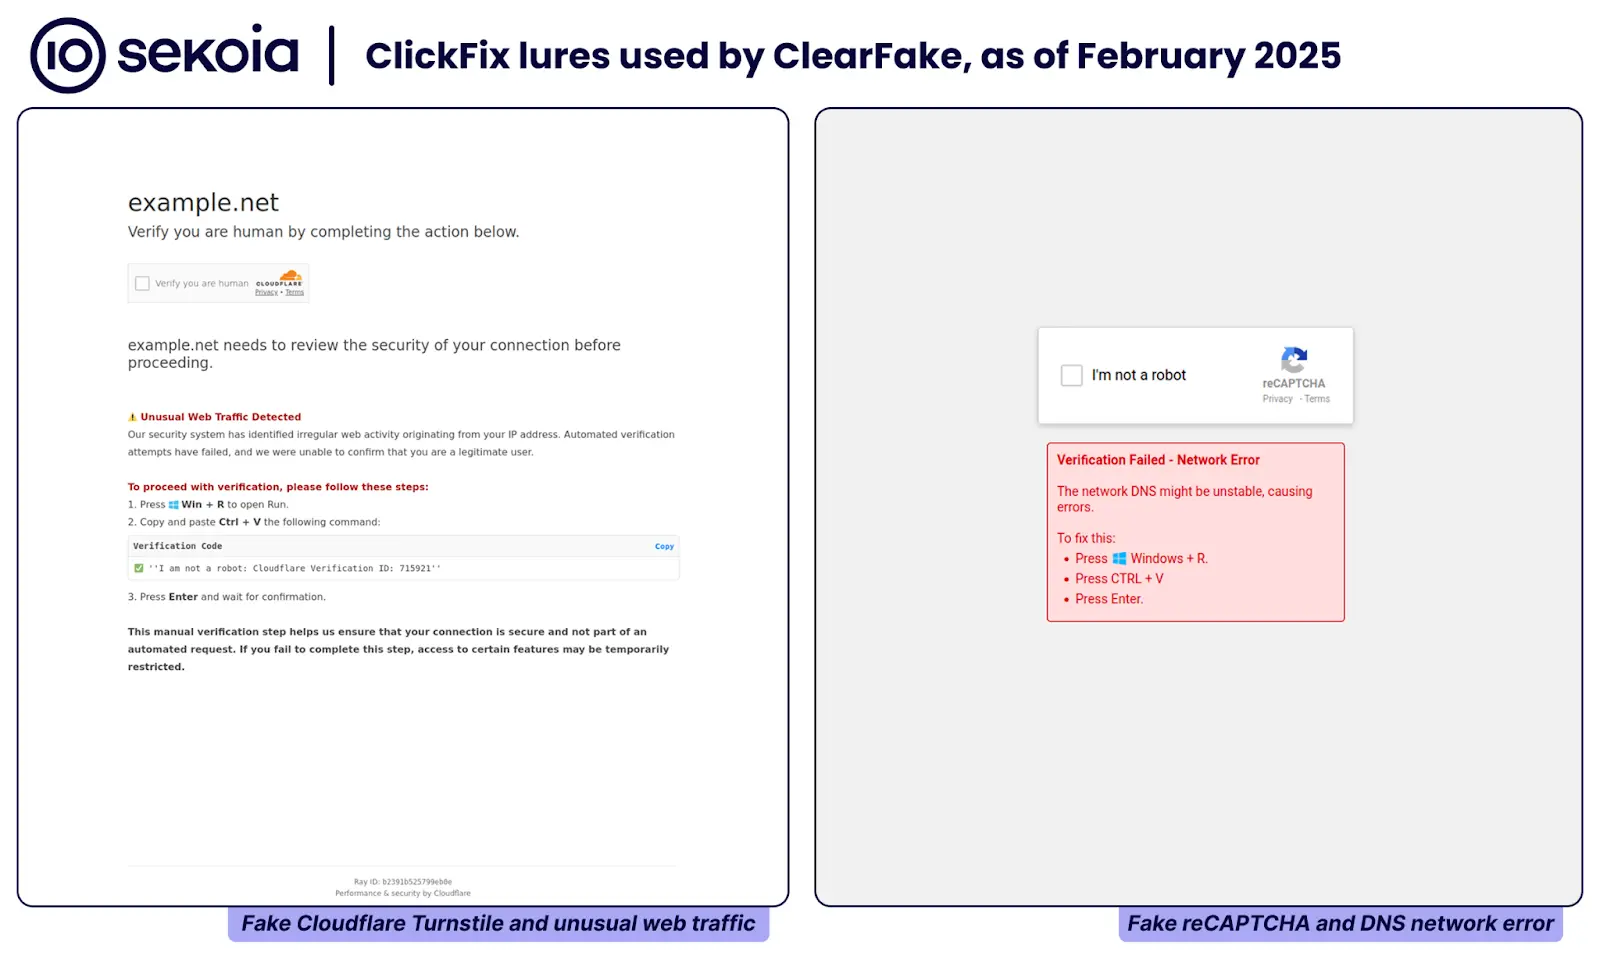
The fake reCAPTCHA asks clients to select pictures of cars, whereas the fake Cloudflare Entryway presents clients with a confirmation challenge, eventually driving them to social building attempts.
The PowerShell commands execute mshta.exe with scripts that provide payloads counting Emmenhtal Loader and eventually Lumma Stealer or Vidar Stealer.
Sekoia analysts are famous for the ClearFake framework, which incorporates over 9,300 compromised websites, with thousands of clients possibly uncovered to these malevolent draws daily.
Utilizing blockchain innovation for malware conveyance speaks to a rising risk that makes conventional relief and blocking more challenging.
Don´t forget to update and stay safe!🕵️
Additional sources to explore: You can also search directly by CVE on Google for more information:







