





Sep 13, 2025 08:53 AM
(This post was last modified: Feb 11, 2026 12:40 PM by JoseMar.)
GitHub Trust Exploited:
Malvertising Delivers Malware via Repos
Malvertising Delivers Malware via Repos
Okay so I just saw a writeup from Unit 42 and my brain did that little jitter where you realize something you thought was safe maybe isn’t. Long story short: there’s a malvertising campaign that’s redirecting searches for GitHub Desktop to compromised repositories. Those repos look normal at first glance, but they contain dangling commits and hidden files that end up being delivery points for a fake installer.
Picture this: you google GitHub Desktop because you want the official client. Ad shows up, looks fine, you click. Bam, you land on a repo that looks legit. README checks out, the commit history looks plausible, everything feels familiar. You download what you think is the installer, and later you realize your machine is phoning home to a server that shouldn’t exist.
Yeah, ugly.
How It Works (High Level)
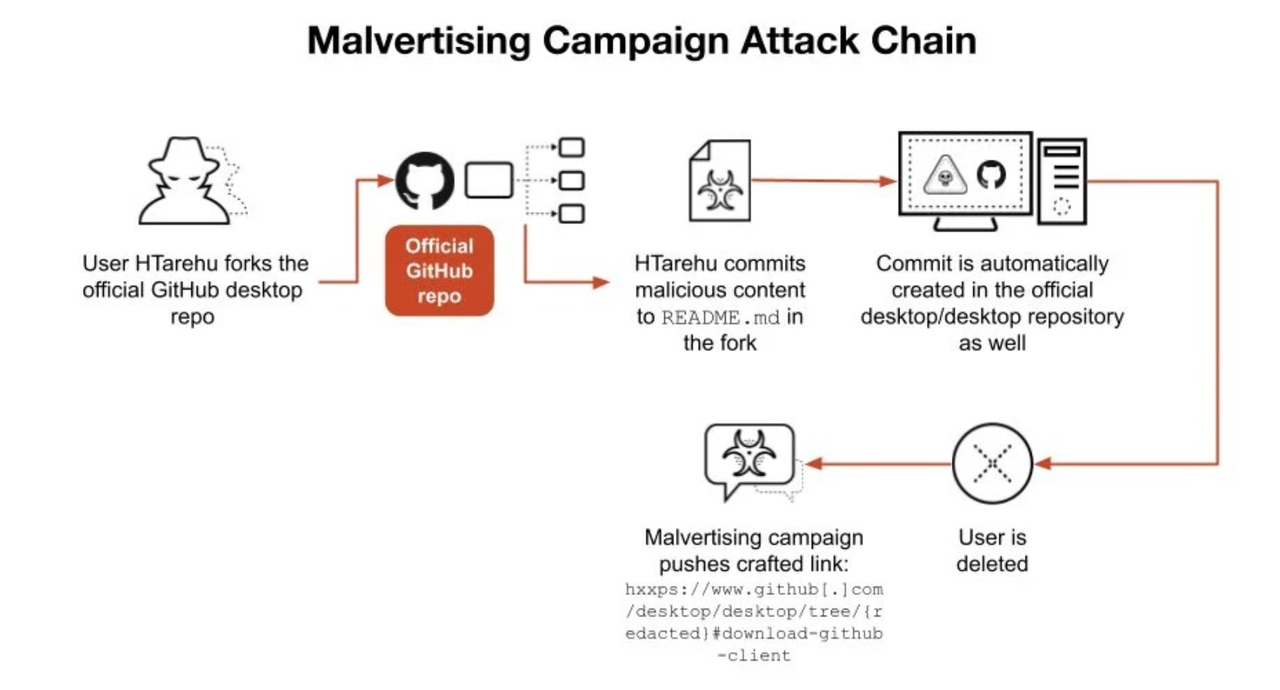
Unit 42 and some folks on X noticed weird download patterns and odd commit activity. The core pieces, simplified:
- Bad actor uses dangling commits and repo artifacts as covert download hosts.
- Compromised ads send traffic to those repos.
- The bundled file masquerades as the GitHub Desktop installer. It’s a multi-stage payload.
- Initial stage runs reconnaissance, gathers OS info, installed apps, network details. That data gets exfiltrated.
- From there the attack chooses a path based on what it finds. PowerShell route? NetSupport RAT gets fetched. Binary route? AutoIT interpreter with odd COM extensions gets used to hide actions.
- Persistence via registry keys. Uses legit system utilities like MSBuild.exe and RegAsm.exe as cover for data exfiltration.
- Also tries to silence Defender by setting exclusion paths and flipping on browser remote debugging so attackers can poke around.
If that sounds familiar or like a Frankenstein mix of old tricks and new polish, it should. It is old tricks, but choreographed better.
Why This Is Clever (And Scary)
The genius is social, not technical. GitHub is trusted. People recognize the layout, the green buttons. A repo feels safe in a way a random exe on a sketchy site does not. Dangling commits are the technical twist - they provide plausible-looking content and can host things that only show up under certain conditions.
Also, using trusted system utilities as a conduit? That is classic living-off-the-land behavior. Blend malicious actions into normal process noise. It reduces alerts and raises the bar for defenders. And conditional payloads make static detection a joke, what runs on one machine might be entirely different on another.
Plus, the ad vector means victims don't need to be tricked through phishing emails or targeted social engineering. It’s broad and opportunistic. People who are casually trying to install a popular tool become targets. That feels... unfair.
What To Watch For (Practical Signs)
Don’t panic but be annoyed. Here are things that made me squint:
- Ads for “GitHub Desktop” that aren’t github.com. Seriously, check the URL before you click.
- Repos with weird commit messages or files with odd extensions sitting in weird directories.
- An installer that asks for unusual permissions or runs PowerShell without obvious reason.
- New MSBuild or RegAsm invocations in logs around the time of installation.
- Browser remote debugging suddenly enabled. That one feels like someone walking into your dev tools and leaving a note. Creepy.
If you manage multiple machines, consider blocking downloads from raw.githubusercontent.com unless strictly necessary, or at least inspect file hashes. Use dedicated tools to verify installers, checksum comparison with official release notes is low effort and high return.
My Two Cents (and one small rant)
I’m tired of the security world treating users like idiots and simultaneously celebrating complexity. This one exploits trust, plain and simple. The fix isn’t just better scanning, though better scanning helps. It’s also about educating people to pause for a second when something looks exactly like what they expect to find.
So yeah, practice basic hygiene. Verify sources. Prefer official domain links. If you run an org or host websites, watch your ad buys. Compromised ads are not just spam; they’re a delivery mechanism and everyone who relies on third-party ad networks should have a moment of dread reading that sentence.
Alright, I’ll shut up now. Anyone else digging into this? Found any indicators, IOCs, or funny commit patterns worth sharing? I’d rather not be paranoid alone.



