


Oct 14, 2025 07:28 AM
(This post was last modified: Oct 14, 2025 09:54 AM by CL1B.)
Bastiller: Skid ready dropper
Like it's hot
Bastille was wondering how skids infect other skids by staging payloads in otherwise legit looking binaries.
How to wrap a program with additional code ?
So I wrote some evil code which might give some insights to this kind of skidware.
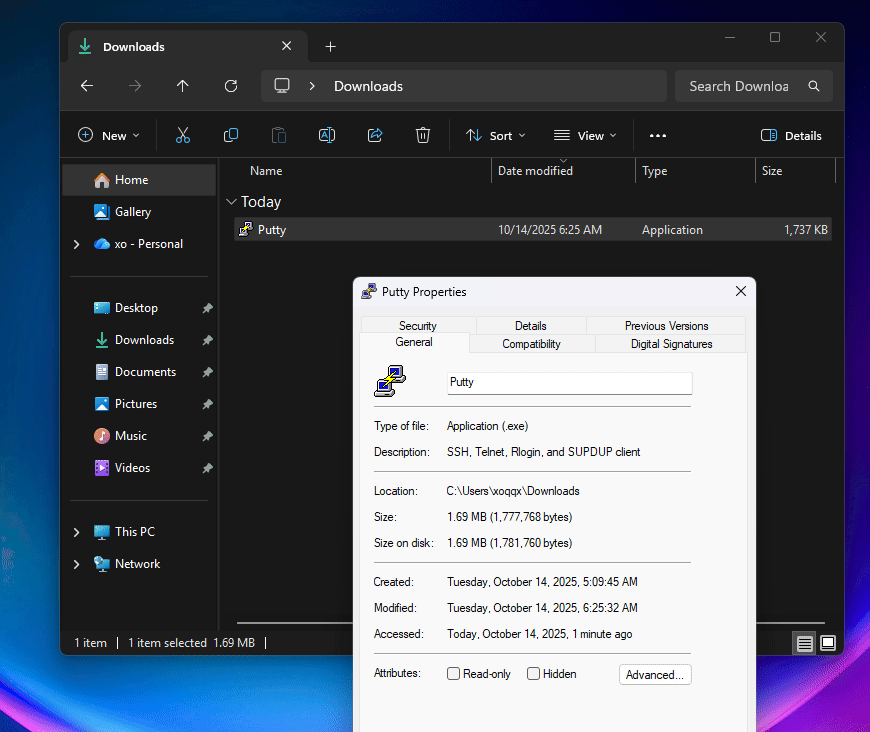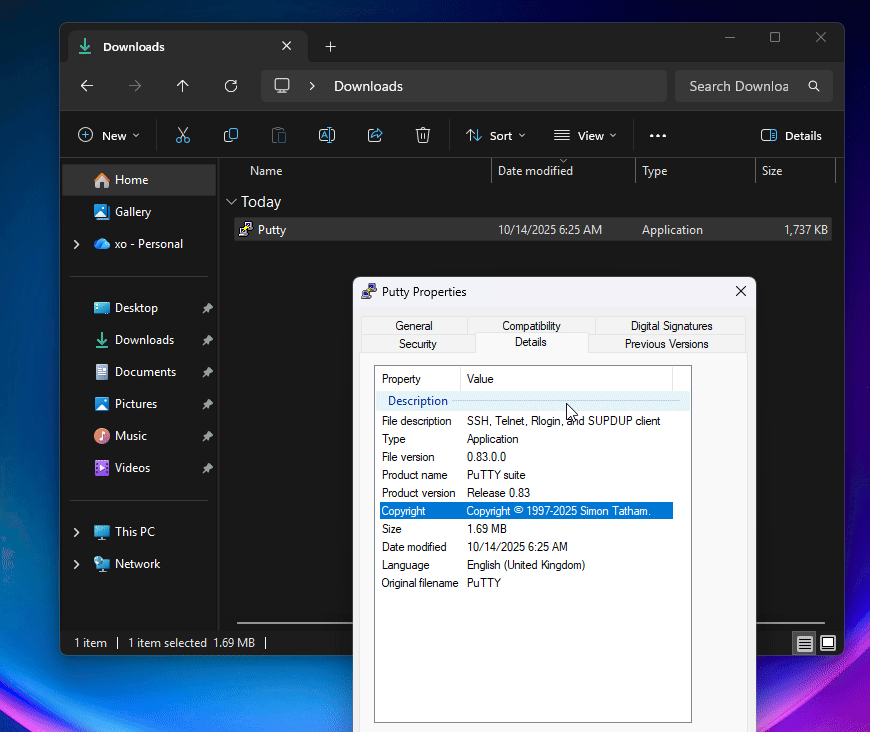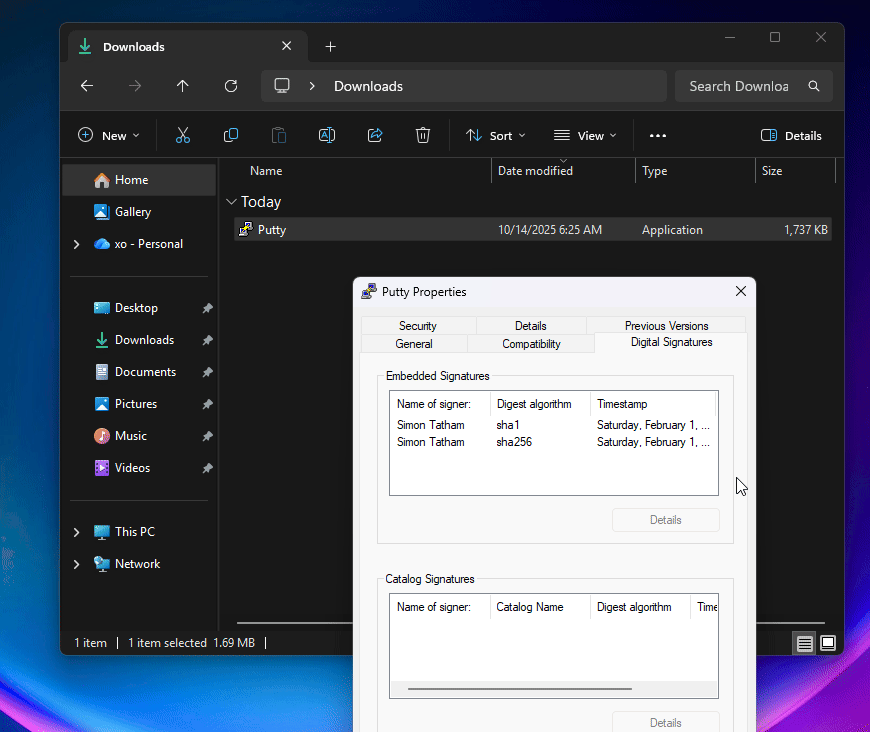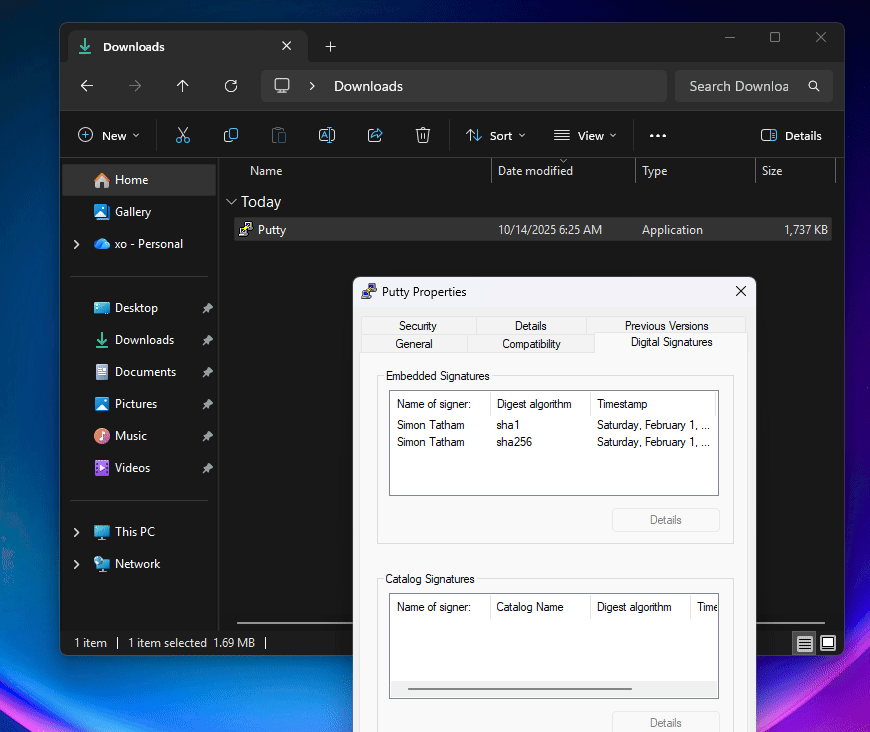
Weird thing is, I noticed Defender doesn't instantly flag invalid signatures anymore.. or at least not putty's?
Shouldn't it auto flag them?
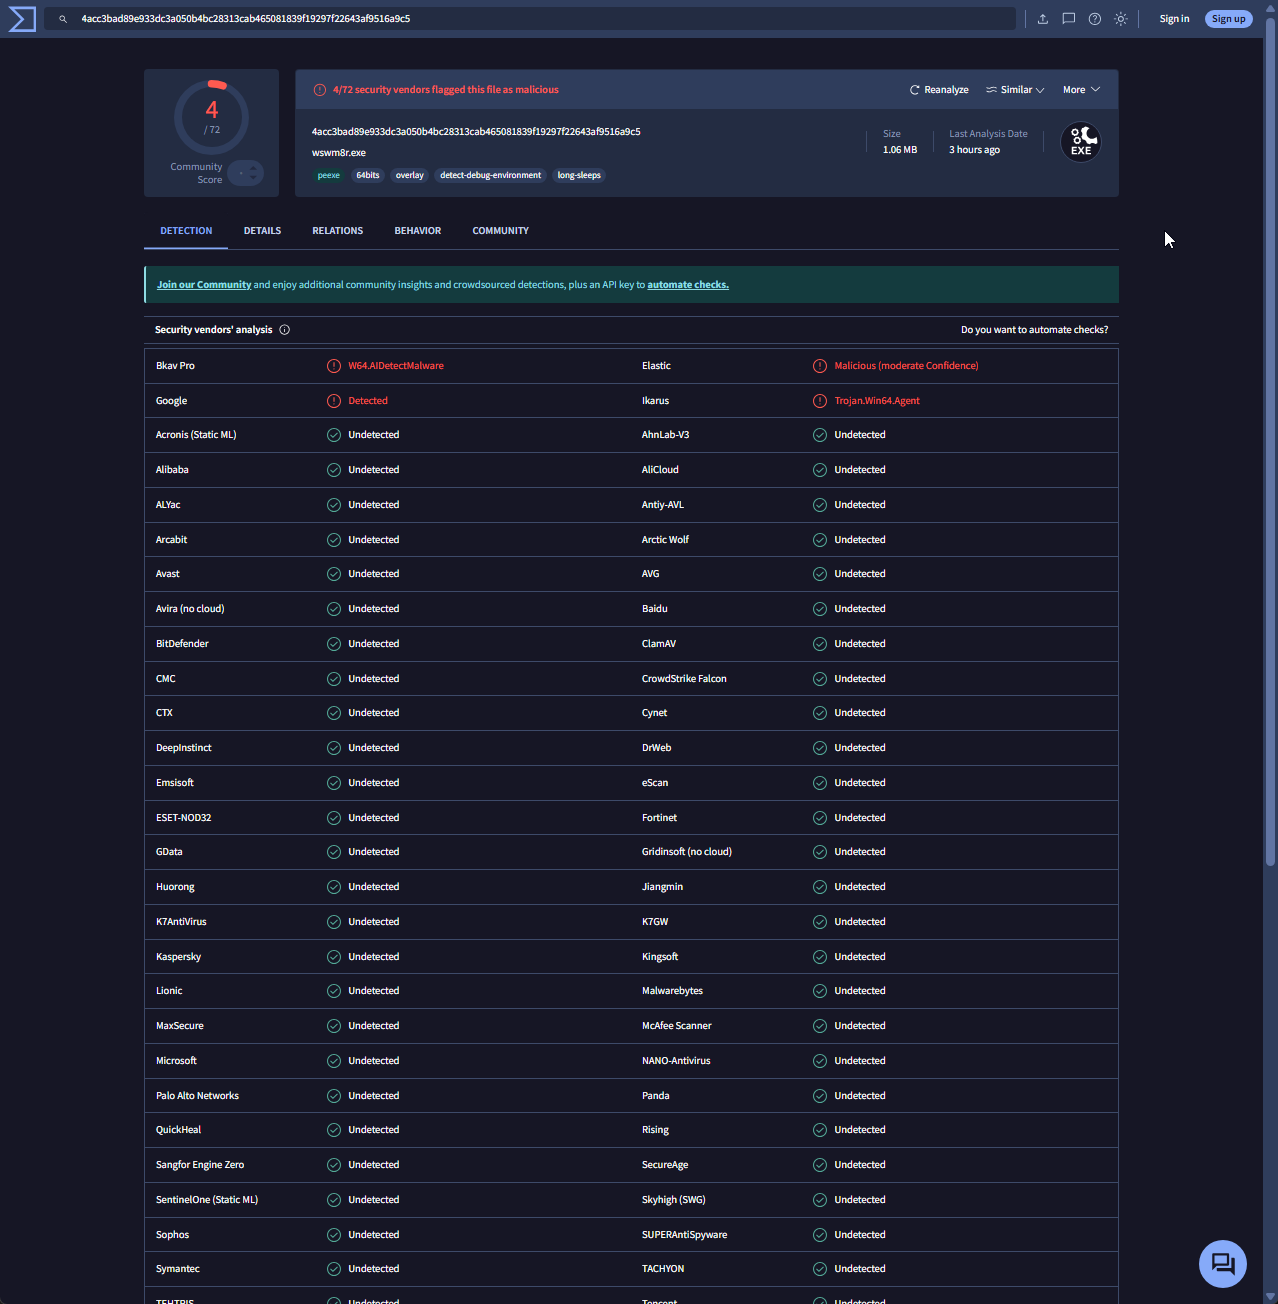
Either way.. Bastiller takes any valid EXE, extracts it's attributes, signatures and such and then compiles a wrapper/dropper or
whatever you want to call it that's weaponized with PS.
Usage:
First change the default HackForums.net payload to whatever payload you want, the compile Bastiller.
Bastiller.exe <path to .exe>
or
Bastiller.exe <path to .exe> -admin
-admin will add a RT manifest to have the app Run As Admin only.
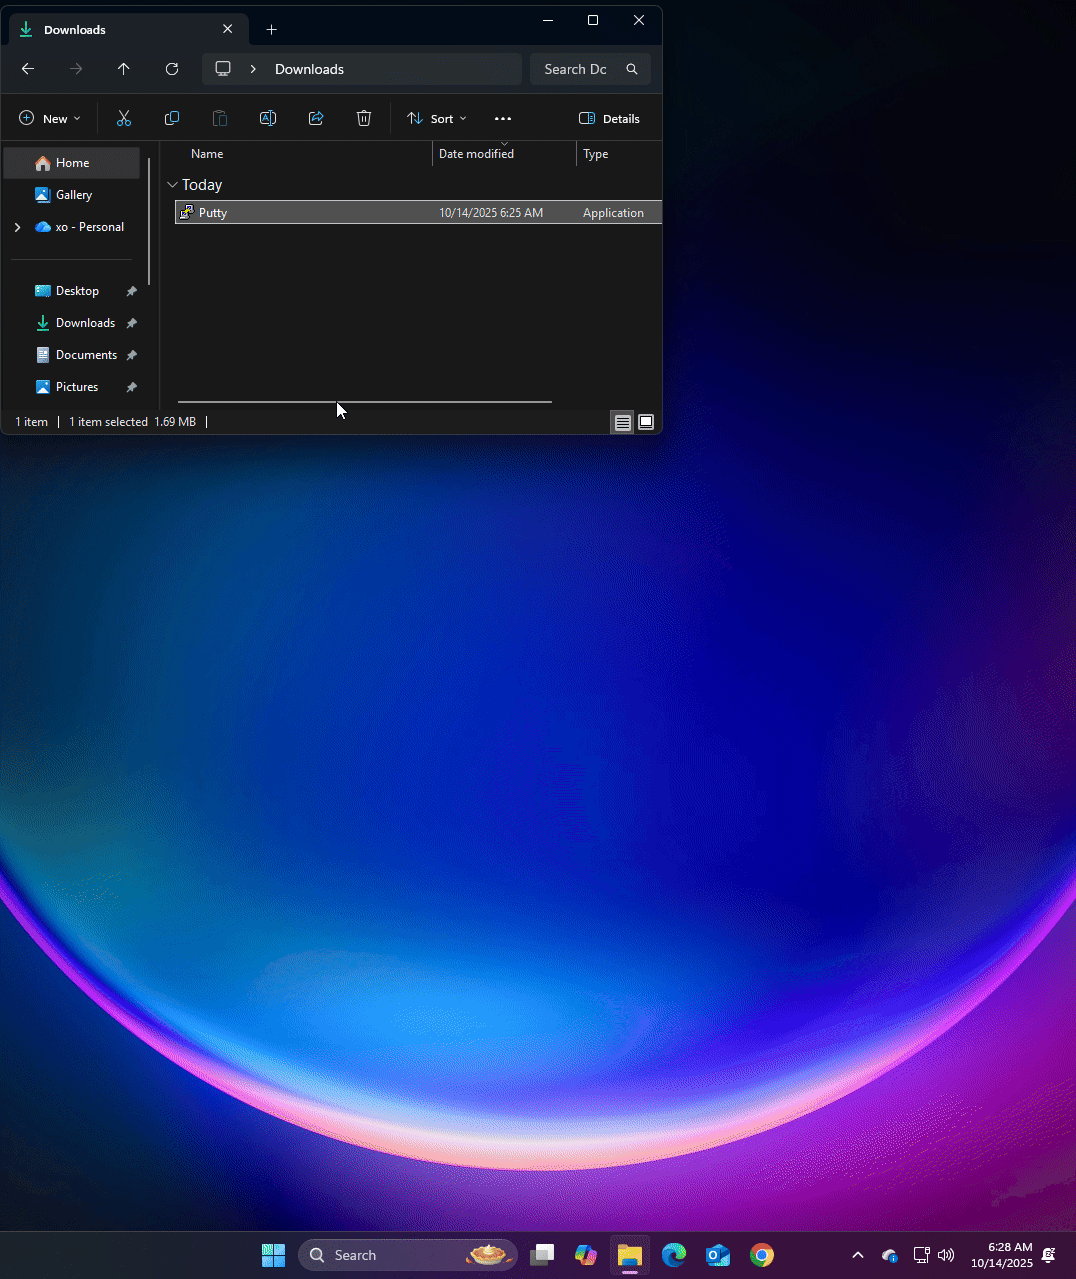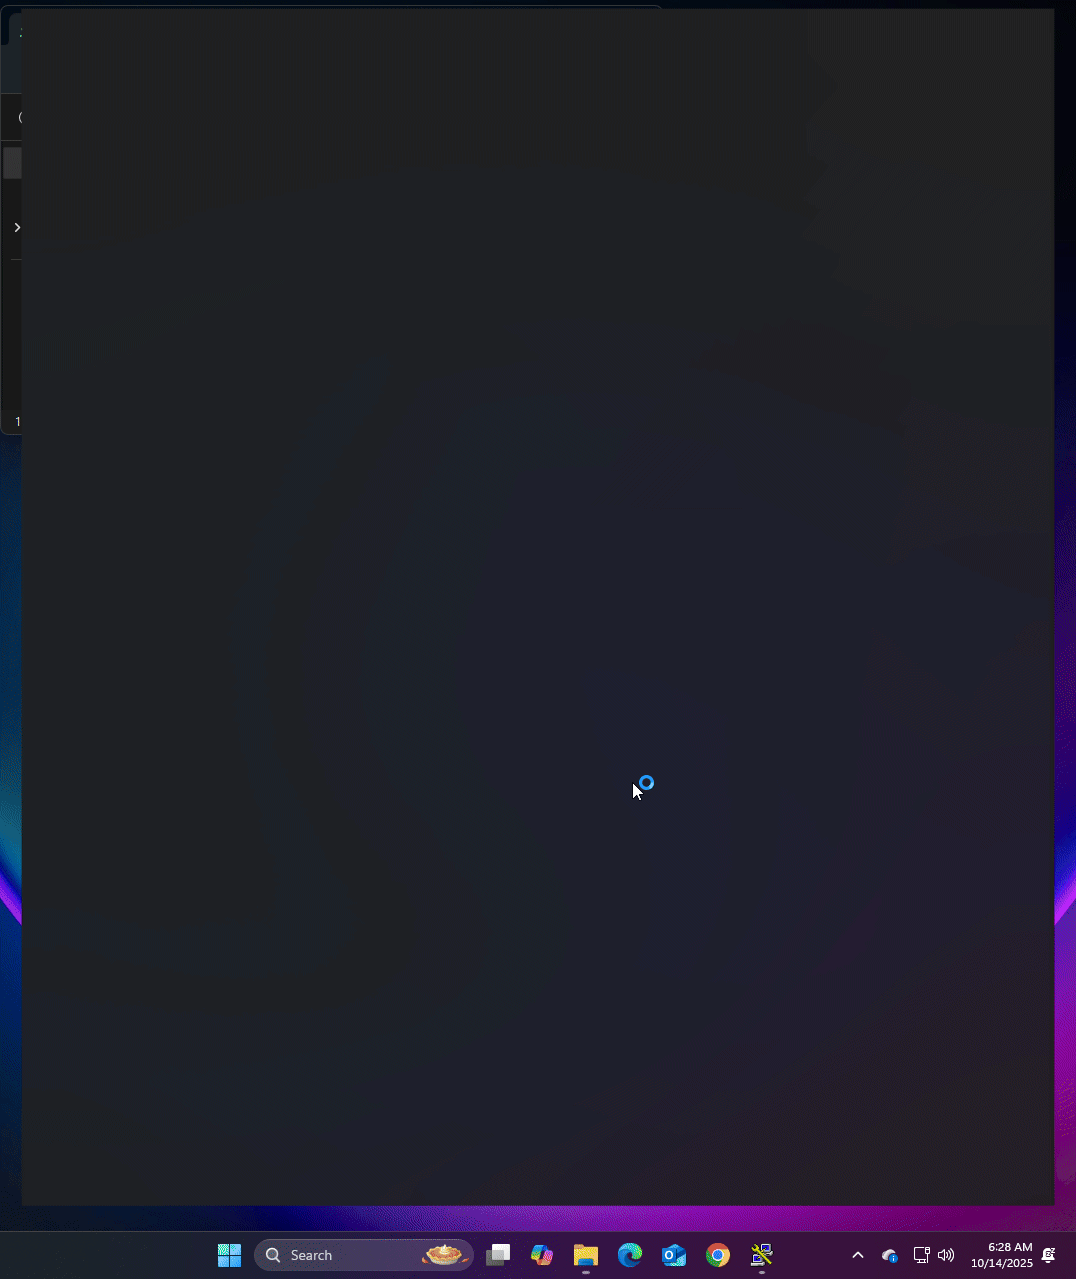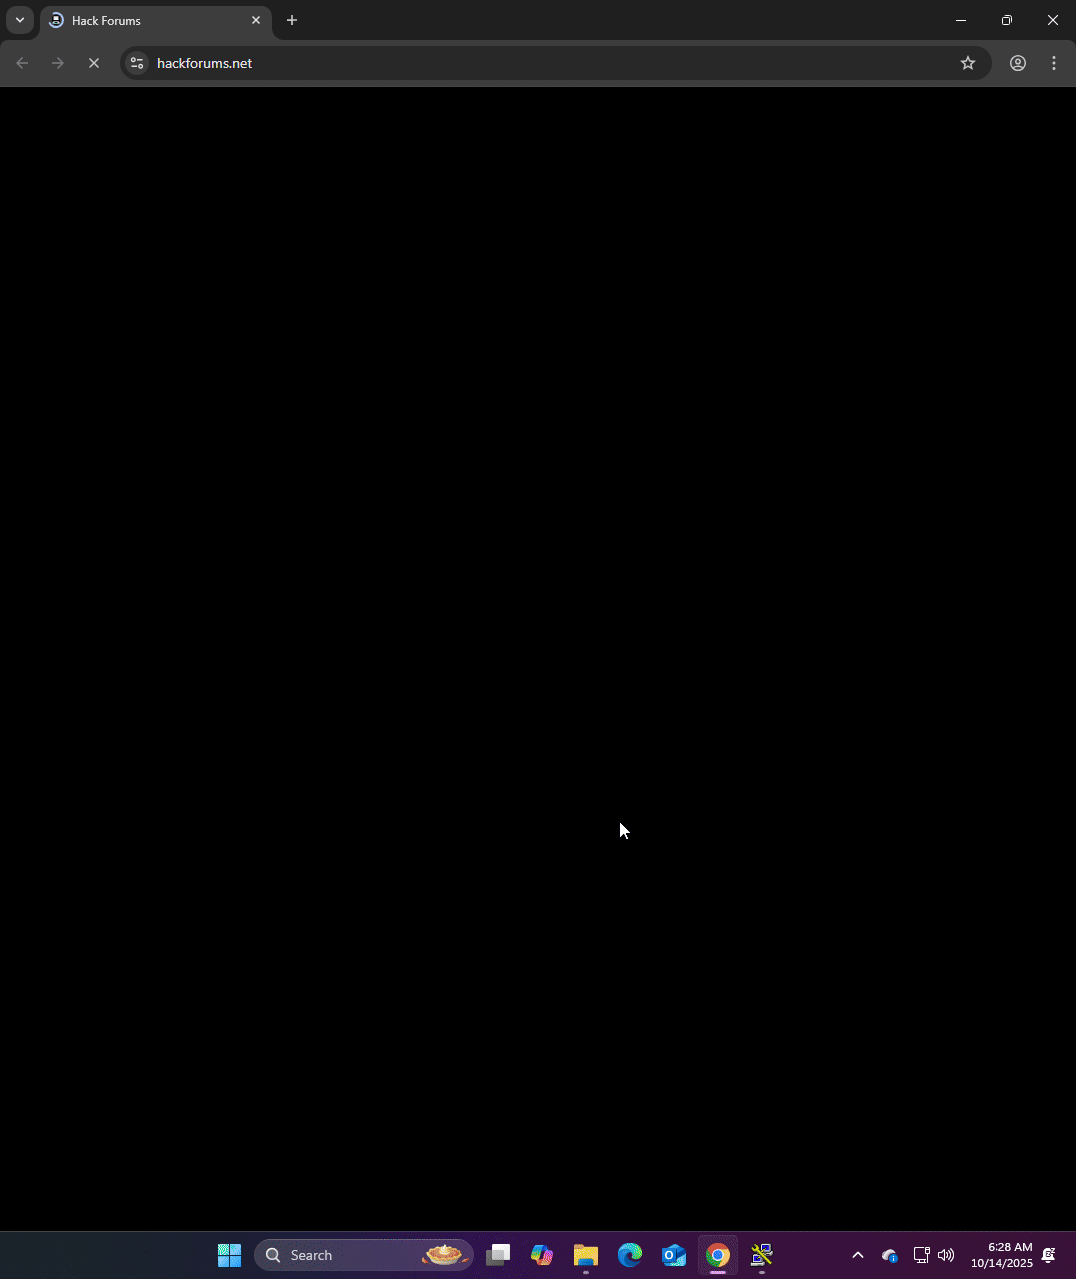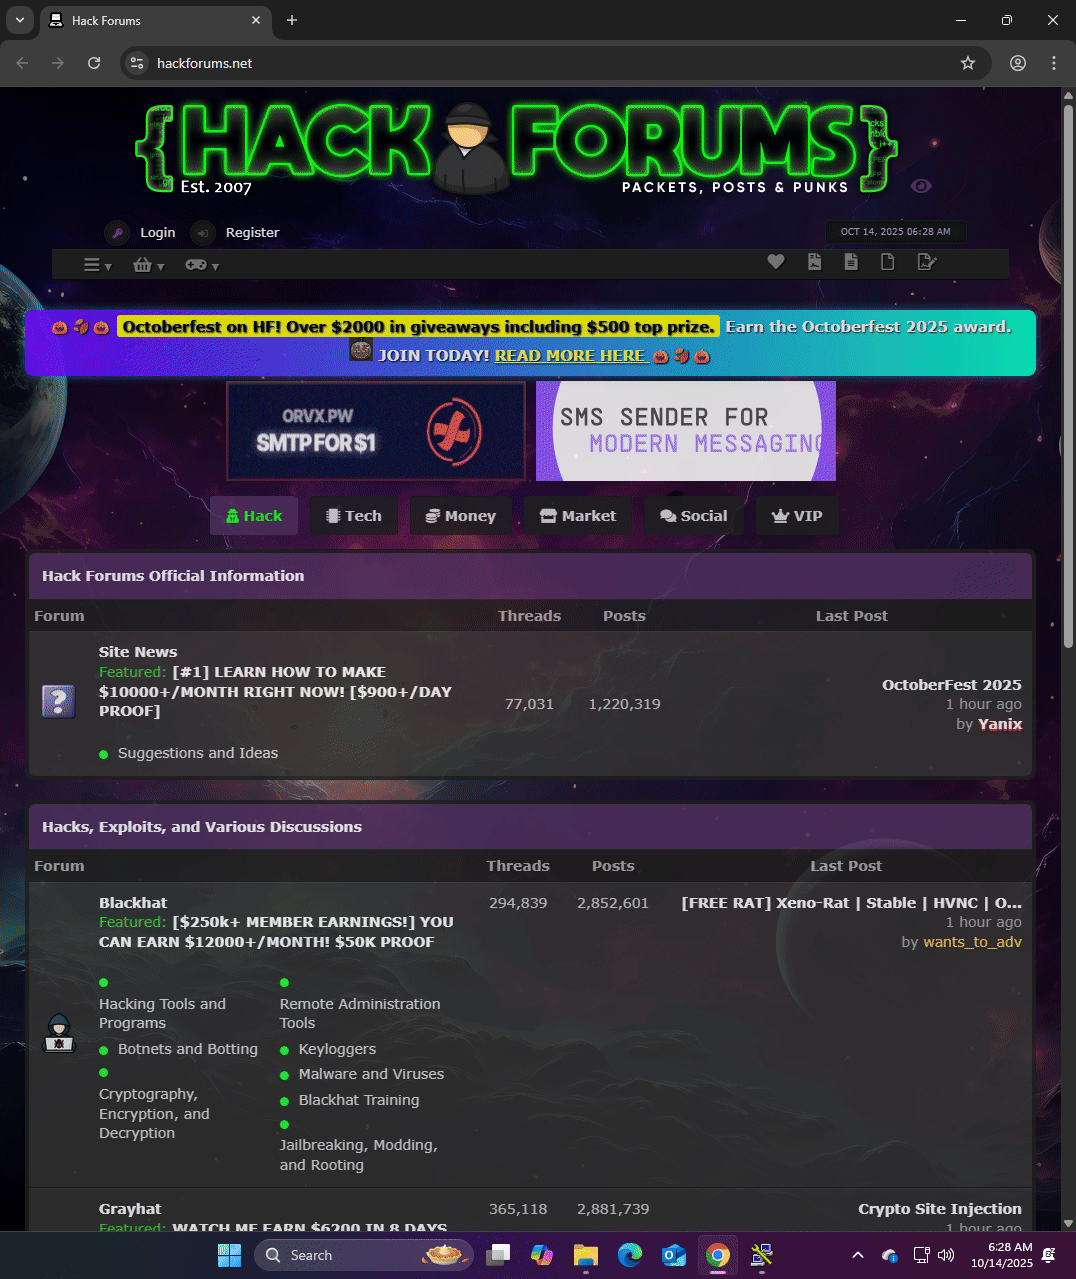
Putty weaponized with the default payload

Putty weaponized with a exclude C:\ drive payload
Proof of concept:
But cigman, how can I not be skid with it?
Learn a thing or 2 about real PE injection techniques. No, i'm not talking about process injection.. I'm talking about detecting possible code caves and then patching them with your payload. Over here we call that: A backdoor. I'm pretty sure there's only 1 user on HF that would understand even the concept of this, so if you're really interested.. you'll have to find out.
Interesting to see some of the EDRs allowing such a binary to run in the first place..
¯\_(ツ)_/¯
Devs in convo (Click to View)
Disclaimer
This tool is for educational and security testing purposes only. Don't use it on systems you don't own or have permission to test. Injection can crash processes and cause system instability.
Like it's hot
Bastille was wondering how skids infect other skids by staging payloads in otherwise legit looking binaries.
How to wrap a program with additional code ?
So I wrote some evil code which might give some insights to this kind of skidware.
Weird thing is, I noticed Defender doesn't instantly flag invalid signatures anymore.. or at least not putty's?
Shouldn't it auto flag them?
Either way.. Bastiller takes any valid EXE, extracts it's attributes, signatures and such and then compiles a wrapper/dropper or
whatever you want to call it that's weaponized with PS.
Usage:
First change the default HackForums.net payload to whatever payload you want, the compile Bastiller.
Bastiller.exe <path to .exe>
or
Bastiller.exe <path to .exe> -admin
-admin will add a RT manifest to have the app Run As Admin only.
Putty weaponized with the default payload
Putty weaponized with a exclude C:\ drive payload
Proof of concept:
But cigman, how can I not be skid with it?
Learn a thing or 2 about real PE injection techniques. No, i'm not talking about process injection.. I'm talking about detecting possible code caves and then patching them with your payload. Over here we call that: A backdoor. I'm pretty sure there's only 1 user on HF that would understand even the concept of this, so if you're really interested.. you'll have to find out.
Interesting to see some of the EDRs allowing such a binary to run in the first place..
¯\_(ツ)_/¯
Devs in convo (Click to View)
Disclaimer
This tool is for educational and security testing purposes only. Don't use it on systems you don't own or have permission to test. Injection can crash processes and cause system instability.





