DO NOT DEAL WITH THIS MEMBER
Sep 12, 2024 06:22 PM
(This post was last modified: Oct 17, 2024 07:30 AM by Py_Dev.
Edit Reason: options added
)
Py_Dev's Private Encrypted Payload Injector
Administrative Privilege Elevation:- Automatically verifies and elevates the tool's privileges to admin level when necessary, ensuring that all operations requiring elevated access are executed seamlessly.
In-Memory Code Execution:- Allocates memory dynamically for code execution directly within system memory, bypassing the need to write executable code to disk. This method helps avoid traditional detection mechanisms that monitor file-based operations.
Randomized Behavior for Evasion:- Introduces randomized delays and non-critical operations throughout its execution flow to make the tool’s behavior unpredictable. This obfuscates patterns that security software might otherwise recognize.
Secure Payload Handling:- Loads and decrypts embedded resources that contain sensitive code or payloads. This ensures that any executable code remains hidden within the tool’s binary, reducing the chances of detection or analysis. We use a combination of Encryption. We use AES-CBC-Mode, Hmac Verification and enhanced encoding of payload.
Efficient Thread Management:- Spawns and manages execution threads in a way that ensures the injected payload is executed efficiently, while maintaining minimal system footprint. This keeps operations discrete and smooth without triggering security alarms.
Special Attributes:- Persistence: Implements an automatic persistence mechanism that ensures the binary re-executes on system startup. This is done by copying the executable to the user's startup directory and hiding the file. This technique helps maintain stealth by ensuring execution continuity across system reboots.
- File Hide: Uses a file attribute manipulation technique to hide the binary from plain sight by applying the "hidden" file attribute. This action is automated via the FileHide() function, enhancing security by making direct detection harder for users and standard tools
Compatble for the following tools (Tested and verified):- Xworm
- Async-RAT
- Xeno-RAT
- Divulge Stealer
- Blue loader
- Pure Miner
- Pure RAT
- PURE LOGS RECOVERY v3
- NIGHTINGALE MALWARE
- ATOM Logger
- VENOM RAT
- Pandora hVNC
Dont see your software on this list? Contact me!
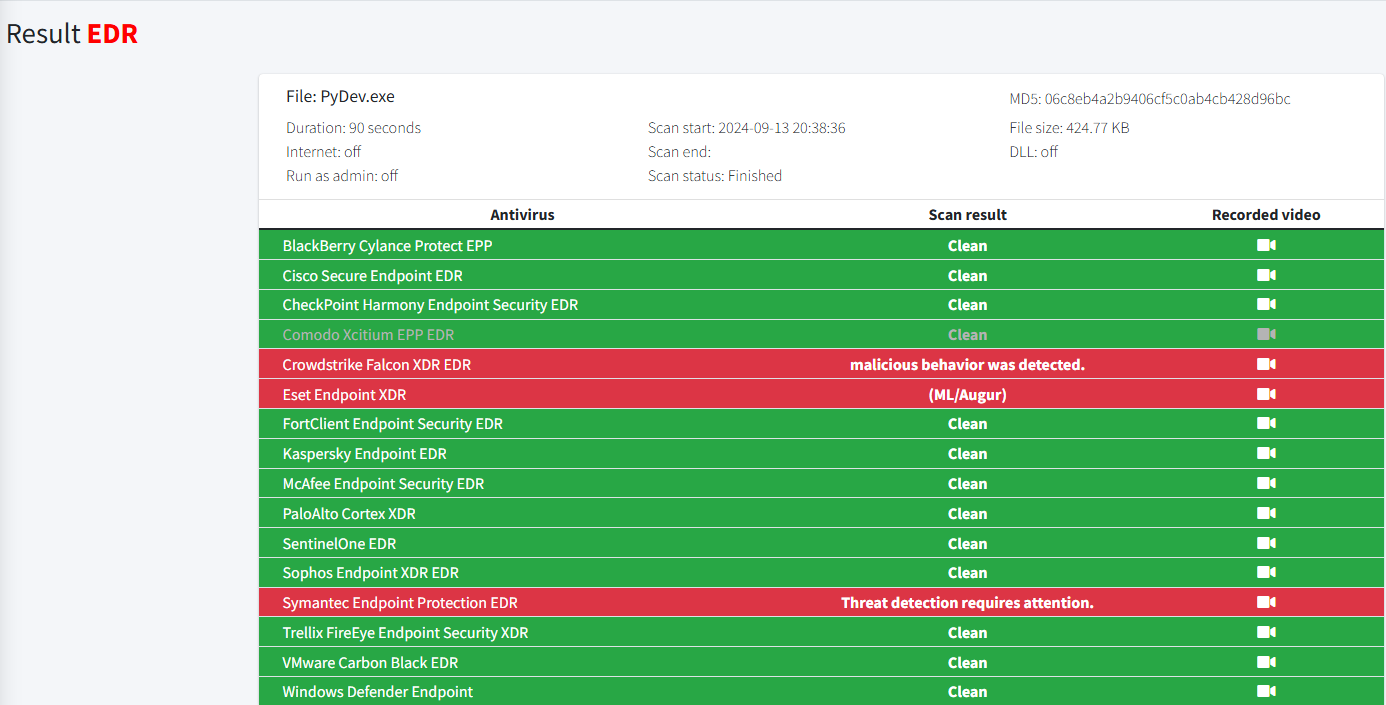
Scan Results:
avcheck
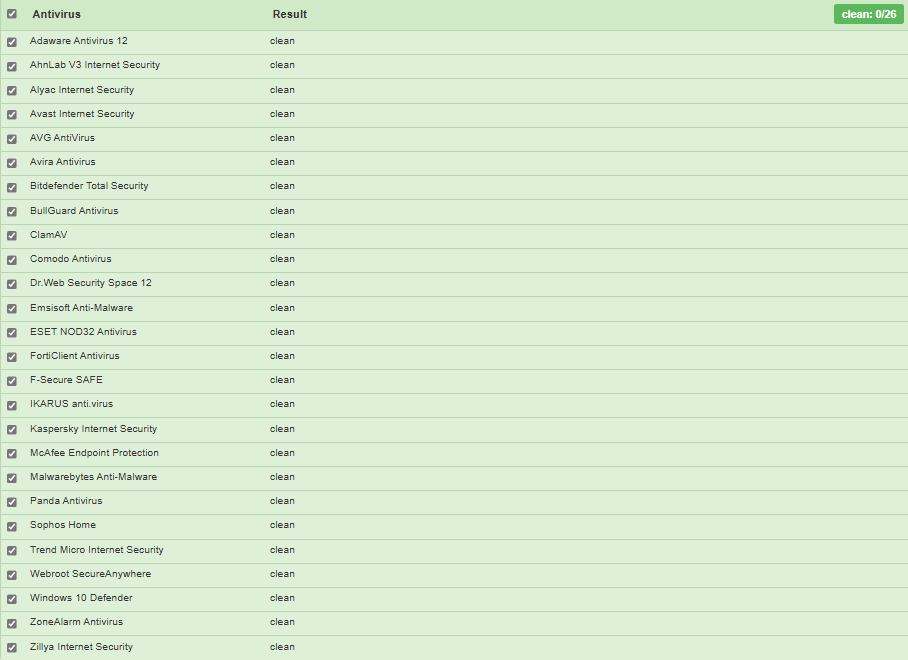
Kleenscan
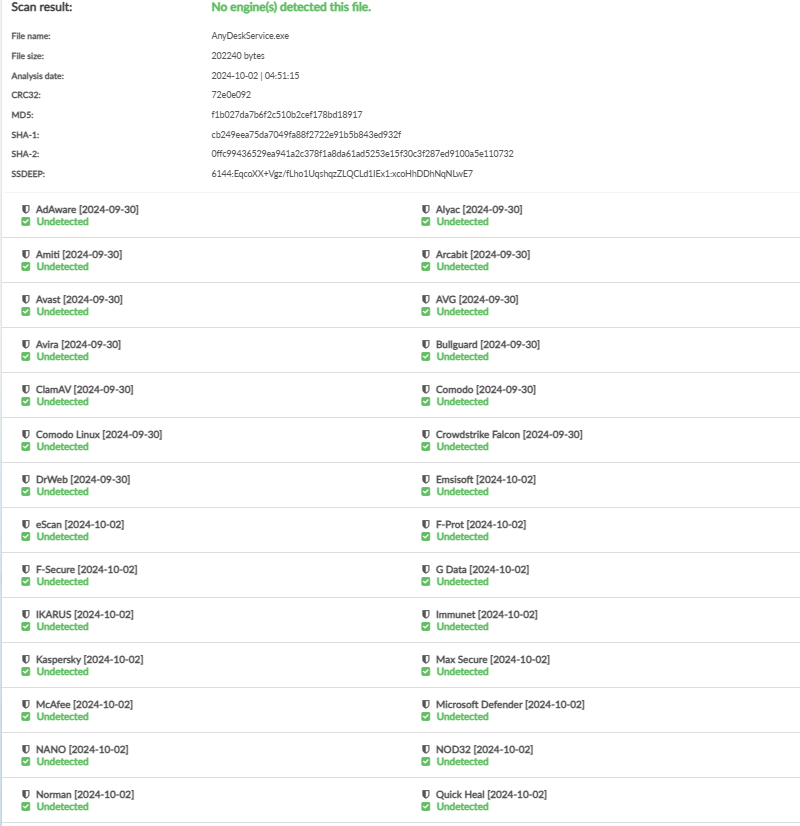
scanner.to
Runtime
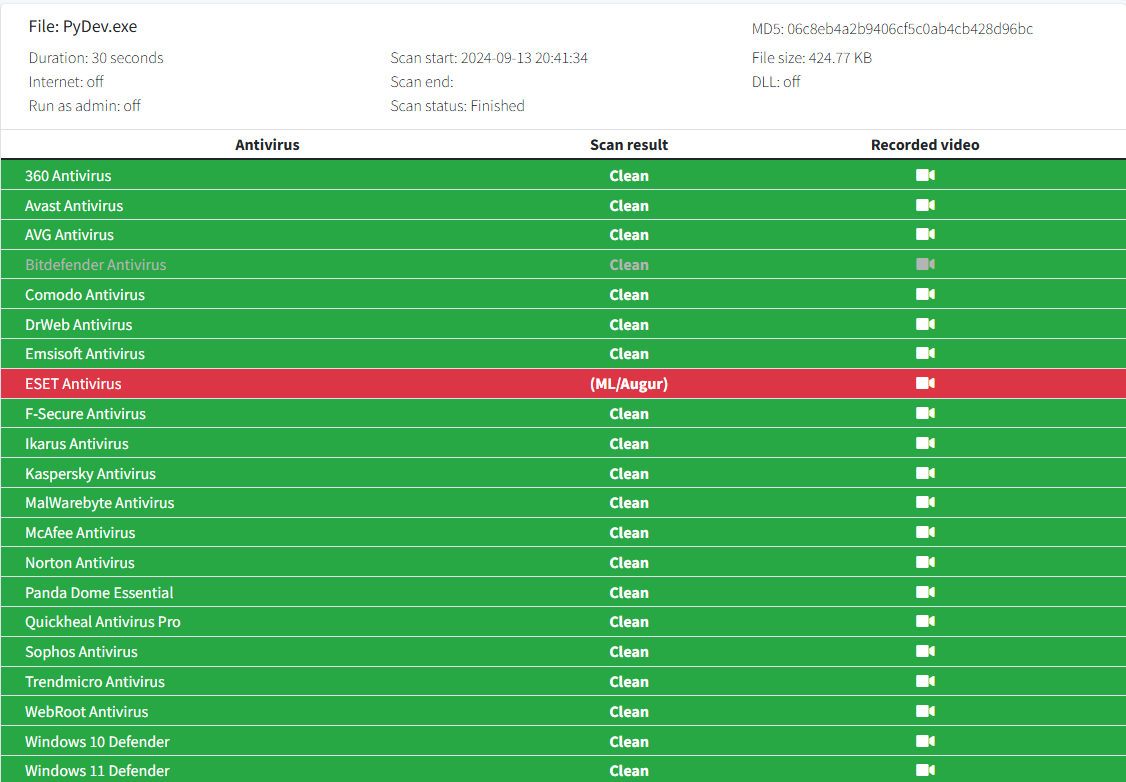
Runtime/EDR
Options Available:
Custom Icon
Custom Assembly Information
Persistence
Bot-Killer (Add on Feature)
Digital Signature (Ripped and appended from another software of your choosing.)
Injector language: C#
Supported payload types:
.NET Executables:
C# Executables:
Native Executables: (In development)
 Useful for the following Malware:
-Remote Access Trojans (RATs)
-Exploit Kits
-Stealers
-Fileless Malware
-Downloaders and Dropper Malware
-Rootkits
-Botnets
Price:
$75.00 USD | Per (1) .exe build
Vouch Copies | 2/2
Methods:- Tron | (TRX) BEST METHOD!
- Bitcoin (BTC)
- Ethereum (ETH)
- Litecoin (LTC)
- Dash (DASH)
- Bitcoin Cash (BCH)
- Ripple (XRP)
- or Use Cooligan middle-man Service.
How To Purchase:
- Start a contact.
- Pay For the order.
- Send me a pm with your .exe you wish to encrypt.
- Once I confirm the payment was received. I will encrypt and send you back the .exe
Contact:
HackForums.net | PM
Vouches:
(Sep 14, 2024 03:55 PM)__Digital__ Wrote: The crypt provided was working flawlessly with a stealer that i couldn't get crypted. That was until now. I am very impressed with this crypt.
Scan before crypt:
https://avcheck.net/id/mV7WKKsEXWBr
Scan after crypt:
https://avcheck.net/id/wjY4XVpgk3hB
The stealer works wonderful and as intended.
(Sep 16, 2024 01:24 AM)Nightmare Wrote: Py_Dev is very friendly !!
Tested his service and i have to say this:
Scantime result : Result
Runtime result: i will add that later on to busy !!
I send him a test file and he send me the encrypted file back,executed that file and got connection directly!
I wish you Py_Dev good luck with your service!Thank you!
(Oct 1, 2024 12:20 PM)Black Jacket Wrote: 10/10 Crypt service, he was so fast to respond and had me setup within munities!
Terms of Service
Py_Dev Encryption Service - Terms of Service
Last Updated: 10-2-24
Welcome to Py_Dev Encryption Service. By using our encryption tools and services, you agree to comply with and be bound by the following terms and conditions. If you do not agree to these terms, please do not use our services.
1. Acceptance of Terms
By accessing or using Py_Dev Encryption Service, you acknowledge that you have read, understood, and agree to be bound by these Terms of Service. Py_Dev reserves the right to modify these terms at any time without notice. Continued use of the service following any such changes constitutes your acceptance of the new terms.
2. Use of Service
Py_Dev provides encryption tools and services to enhance the privacy and security of your data. You are responsible for the lawful use of these services.
Prohibited Activities:
• You agree not to use our encryption services for any illegal activities, including but not limited to unauthorized hacking, data theft, fraud, or violating any applicable laws.
• You are solely responsible for any data or content encrypted using Py_Dev services.
3. No Responsibility for Client Actions
Py_Dev provides encryption services as a tool for secure communication and data storage. We assume no responsibility for the actions or behaviors of users while using our tools. This includes any illegal, unethical, or harmful use of the encrypted data.
You acknowledge and agree that Py_Dev, its owners, developers, and affiliated parties shall not be held responsible or liable for:
• Any damage, loss, or legal consequence arising from your use of our encryption service.
• Any unauthorized access to your encrypted data caused by your negligence or improper use.
4. No Warranties
Py_Dev provides its encryption services on an “as-is” basis without any warranties of any kind, either express or implied. While we strive to provide the highest level of security, we do not guarantee that the service will be free from vulnerabilities, errors, or interruptions.
5. Indemnification
You agree to indemnify, defend, and hold harmless Py_Dev and its team from any and all claims, damages, liabilities, costs, or expenses (including reasonable legal fees) arising from:
• Your use or misuse of the encryption service.
• Any violation of these Terms of Service.
6. Limitation of Liability
To the fullest extent permitted by law, Py_Dev and its team shall not be liable for any indirect, incidental, consequential, or punitive damages, including loss of data, profits, or business opportunities, resulting from:
• The use or inability to use the service.
• Unauthorized access to your encrypted data.
7. Termination
Py_Dev reserves the right to terminate or suspend access to the encryption service at any time, without notice, for any conduct that we believe violates these terms or is harmful to our interests or the interests of others.
8. Refund Policy
No refunds of any kind. All sales are final. Every customer will be provided with a scan of their file. We do not guarantee how long files remain undetectable. As this will vary from customer to customer. If you are found scanning stubs on virus total or similar websites we will not continue services.
Start Contract
Good. İ want to buy.. I don't know how to get it
DO NOT DEAL WITH THIS MEMBER
(Sep 13, 2024 01:07 AM)Olivium50 Wrote: Good. İ want to buy.. I don't know how to get it
start a contact and then start a conversation with me. I only deal on site.
I can't send private messages. I'm new.
DO NOT DEAL WITH THIS MEMBER
Sep 13, 2024 02:30 PM
(This post was last modified: Sep 13, 2024 05:09 PM by Py_Dev.)
(Sep 13, 2024 02:34 AM)Olivium50 Wrote: I can't send private messages. I'm new.
sent you a convo you should be able to reply to that. Or just comment on a few threads and you will unlock messaging.
Hi Im interested in the CRYPTS. can you please provide a contact on Telegram?
Sep 14, 2024 04:36 AM
(This post was last modified: Sep 14, 2024 12:04 PM by Charlie Sheen.)
Hello. Do you offer a trial or something like that?
I want to try using it and I will leave a review.
Content deleted to prevent possible harm to our members. -Staff
DO NOT DEAL WITH THIS MEMBER
(Sep 14, 2024 04:36 AM)hoangdoan Wrote: Hello. Do you offer a trial or something like that?
I want to try using it and I will leave a review.
My tele @hdev84
I will be giving out vouch copies to reputable members here on HF. Unfortunately, you do not make this qualification.
DO NOT DEAL WITH THIS MEMBER
1:Actually, the decision for a small scan window is deliberate. The idea behind a 30-second scan is to be able to catch the initial phases of malicious behavior when it hasn't fully unpacked or obfuscated itself. Many modern malware families try to delay execution or do sandbox evasion techniques that fire after a long delay. We force the malware to act fast or get caught by keeping the test window short. Indeed, if we let it run for 180 seconds with access to the Internet, then we give it ample time to connect to a command-and-control server and adjust its payload to what it finds. We do want to avoid that from happening.
It's a technique of early detection before the malware might get a chance to execute their full payload. It has nothing to do with beautification; instead, it is absolutely about rapid response and mitigation before the malware escalates its actions.
2: Where it's true that the Windows Loader sets up initial threads for program execution, in this instance, we are discussing the creation of threads using CreateThread for injecting shellcode.
Code IntPtr hThread = CreateThread(IntPtr.Zero, 0, allocatedMemory, IntPtr.Zero, 0, out uint threadId);
The running of the shellcode in a newly created thread, which is not controlled by the Windows Loader, takes place here. Such creation and handling of our threads have the effect of very well controlling the context of execution: precise timing, access, and priority will result in the more subtle and effective running of the shellcode. This kind of thread handling allows us to enforce how and when code runs, giving flexibility over inherent Windows thread handling.
3: Nobody says VirtualAlloc is any kind of invention; by dynamic memory allocation, I mean request and get allocated in runtime, and that's what this code does. We allocate in runtime the memory holding the decrypted shellcode; it is not predefined, not static. Also, by doing so, we can control at runtime permissions-performing the allocation with PAGE_EXECUTE_READWRITE, for example-and control when and how such memory is used. That is indeed a pretty common technique in malware and exploitation-to make sure malicious payloads execute only when actually needed, without raising the flag any earlier.
Code IntPtr allocatedMemory = VirtualAlloc(IntPtr.Zero, (uint)shellcode.Length, MEM_COMMIT, PAGE_EXECUTE_READWRITE);
This form of allocation ensures that sensitive data-such as the shellcode-do not live in memory when not needed, adding stealth to the operation.
4:You are absolutely right: Sleep(1000) is just a delay. However, in real code, it's much more than just simple fixed sleep: function RandomDelay() introduces randomness into timing:
Code Random rnd = new Random();
int delay = rnd.Next(10, 1000);
System.Threading.Thread.Sleep(delay);
This introduces randomness into the timing and makes it harder to statically and behaviorally analyze. So many malware detection systems and sandboxes look for consistent behaviors within short periods of time. Randomized delays introduced confuse these systems, thinking the process is benign since the timing is inconsistent with typical malicious signatures. While the payload itself does not change, randomized behavior helps evade detection mechanisms that usually rely on timing patterns, which tend to be key in behavioral analysis.
All those techniques here are not "false advertisement" but rather standard things when performing malware testing, evasion, and exploit development: dynamic memory allocation, thread management, and randomized delays are all well-known techniques that ensure stealth and performance, helping to evade detection.
The crypt provided was working flawlessly with a stealer that i couldn't get crypted. That was until now. I am very impressed with this crypt.
Scan before crypt:
https://avcheck.net/id/mV7WKKsEXWBr
Scan after crypt:
https://avcheck.net/id/wjY4XVpgk3hB
The stealer works wonderful and as intended.
Does it work with Xeno and Venom? And how many days will it be safe? I am really interested in it
DO NOT DEAL WITH THIS MEMBER
(Sep 14, 2024 05:31 PM)hoangdoan Wrote: Does it work with Xeno and Venom? And how many days will it be safe? I am really interested in it
Yes it will. It all depends on how many loads touch and scan the file. So far they are pretty long lasting in my testing.
Sep 14, 2024 10:11 PM
(This post was last modified: Sep 14, 2024 10:12 PM by Tyr.)
(Sep 14, 2024 04:45 AM)Py_Dev Wrote: I will be giving out vouch copies to reputable members here on HF. Unfortunately, you do not make this qualification.
I'll take a vouch copy and pop it onto some VMware then write a nice review for you if this works as you advertise it to
DO NOT DEAL WITH THIS MEMBER
Sep 15, 2024 01:01 AM
(This post was last modified: Sep 15, 2024 06:35 PM by Py_Dev.)
(Sep 14, 2024 10:11 PM)Tyr Wrote: I'll take a vouch copy and pop it onto some VMware then write a nice review for you if this works as you advertise it to
Sounds like a plan man start the contract and send it over
I still have 1 vouch copy up for grabs. First come first serve. Reputable members only.
Congrats for your service my brother!Can i have a vouch?
|