Recently I've become more and more interested in ways to bypass antivirus software and I come here once again to share my ideas for personal projects^^
I saw on some forums people selling so-called reg droppers with very expensive prices, but their objective is basically this: Add Exclusion to WD
Little Stub
Chrome Bypass
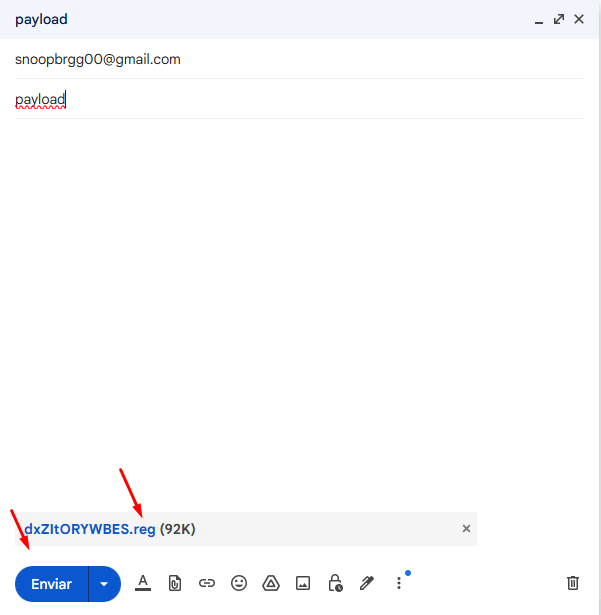
And have the possibility of being attached to EMAIL.
And I confess, this really caught my attention and I decided to create my own project with these interesting ideas, and I'm here to share it with members who are interested in the subject, what do you think? I saw that it is little explored on HF ^^
Please feel free to provide constructive criticism and debate, after all, we are here to share!
Operation:
Choose your .exe
It will create a .REG that does the following
Booting a ps1 > Uac Bypass > added the C: exclusions > Reading the bytes of your .exe > executing.
If you have any ideas that you want to be implemented, you can send me a PM.✌
That's the kind of content I like to see on HF 👀 I've stumbled upon black hat activities and methods recently (I've spent all my time on the white hat side and didn't pay that much attention to the black), and I have to admit that I like it.
I plan to start playing with RATs and sutff in my homelab soon, I see that you're using Async and many people recommended it. I'll take a try with it too, and will follow your future threads I guess
Is the :
Code
Add Exclusion to WD
Obfuscated ? When I'm doing malware analysis I often see PS command lines adding exclusion path to WD and it's easy to check them
(Oct 26, 2024 06:36 PM)Bastille Wrote: That's the kind of content I like to see on HF 👀 I've stumbled upon black hat activities and methods recently (I've spent all my time on the white hat side and didn't pay that much attention to the black), and I have to admit that I like it.
I plan to start playing with RATs and sutff in my homelab soon, I see that you're using Async and many people recommended it. I'll take a try with it too, and will follow your future threads I guess
Is the :
Code
Add Exclusion to WD
Obfuscated ? When I'm doing malware analysis I often see PS command lines adding exclusion path to WD and it's easy to check them
Hi Bastille! I’m glad you came across this.✌ I use AsyncRat because, in my opinion, it provides a very stable connection with users, making it useful for my tests.
I’ve already published the Windows Defender bypass method here on HF so that members can understand a bit of how it works. However, my code is a bit different and isn’t obfuscated because I’m testing several functions haha.
I'm here to bring you the first update of REG EXPLOIT. I've made some nice little changes!
[*] The system is now web-based
[*] Updated .reg protection
[*] Added login system via KEY
[*] Bot to create new KEYS
[*] Zip system and adding password to .zip
These are small changes that make a difference. The output is 1/40 Kleenscan (the only empty one is a false positive).
Some people ask about the sale, and I started thinking about it, it's something new on the market and interesting, any thoughts on it?
I'm interested in how you did it
I combined ps1 with hexadecimal and successfully bypassed WD, but I couldn't create it into REG. It didn't work after creation. It was a bit distressing. :((
Oct 29, 2024 08:32 AM (This post was last modified: Oct 29, 2024 10:43 AM by latencyx.)
(Oct 28, 2024 04:02 PM)woo097878781 Wrote: I'm interested in how you did it
I combined ps1 with hexadecimal and successfully bypassed WD, but I couldn't create it into REG. It didn't work after creation. It was a bit distressing. :((
It depends a lot on how your code works, and how complex it is. There are many ways to do what I do but few are stable and good, basically what I try to do theoretically is this: Basically the code I created does the following steps: REG creates a PS1 and adds it to startup
[User Restarts PC]
.PS1 starts
C: added exclusions
.PS1 executes the bytes of your .exe saving on the PC.
Now it all depends on how you execute it and how well it is done✌
Hello everyone,
I'm here to bring you updates on the project, basically I added some features and protections.
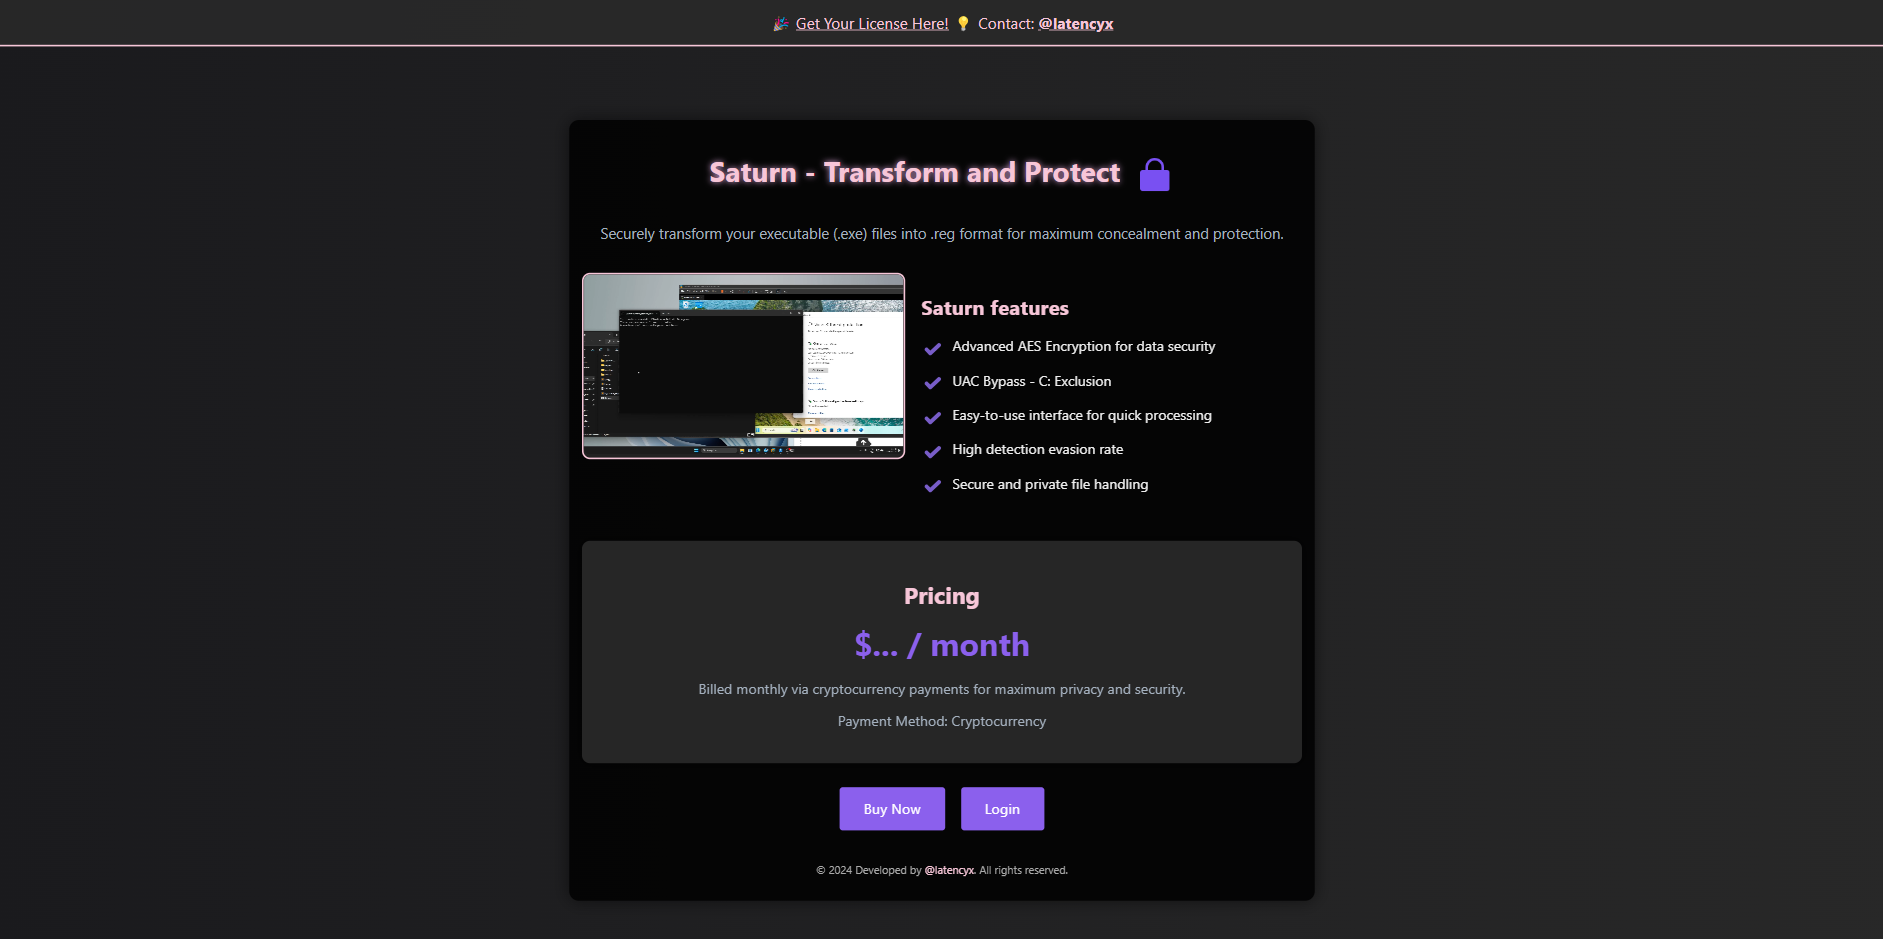
[*]Sales panel
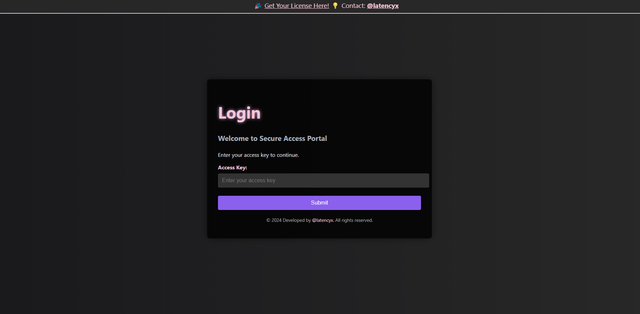
[*]Login panel
[*]Update on the .REG obfuscation system
[*]JunkCode system (Making the output more unique)
Here are some screenshots, what do you think of the design?
Sales Panel:
Login Panel:
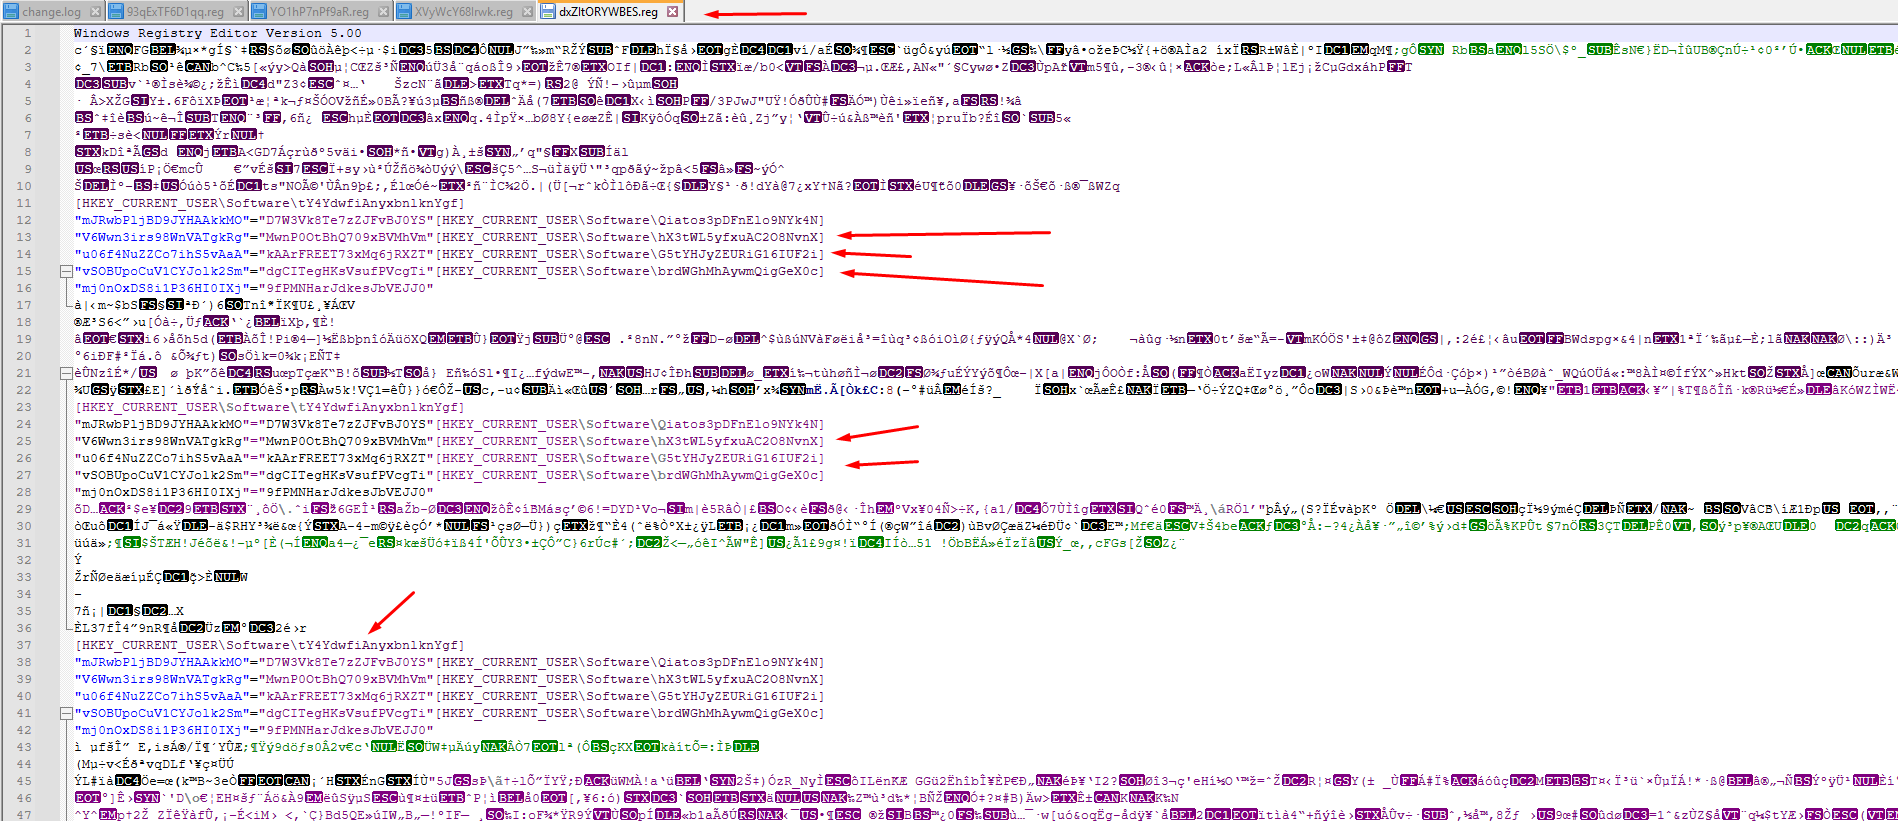
Obfuscation: ~
Gmail attach:
I'm still thinking about a price, I'm thinking about leaving the price low for the first few days or leaving a promotional code if I sell it.
Oct 30, 2024 03:40 AM (This post was last modified: Oct 30, 2024 02:37 PM by latencyx.)
(Oct 29, 2024 06:14 PM)hoangdoan Wrote: Great dude, good luck.
Have you thought about offering your services?
I'm thinking about it, but I'm going to improve security and the user panel a little more, I'm going to give access to some members who have a good reputation, I believe there are few providers of the same service as mine, and those that exist charge an absurd amount for just one file, while I sell unlimited access to a number of files New Update!
I'm still working on the website hosting along with small aspects of our service. Our website is now online but still under construction! I created an infographic for sales. Since I don’t have access to the HF market, I’ll just share updates of my work here. Curious users can see the new changes and improvements, as well as give ideas for the project. ^^ Of course, if you're a recognized user in the community, feel free to request a test; I'd be happy to send you a test key! [2 Keys free]
[*] Website update for different devices
[*] Domain update
[*] The project has been named Empty Builder (I thought it was interesting xD)
Remember, this project is in its early stages, so any contributions will be greatly appreciated!
To the user who comes from HF out of curiosity, mention I give a $10 discount (Temporary)
For those users who have little knowledge in this area or are interested, contact me, I am willing to help HF members to build a reputation! Everyone is welcome.✌ Demonstration:
Recently I've become more and more interested in ways to bypass antivirus software and I come here once again to share my ideas for personal projects^^
I saw on some forums people selling so-called reg droppers with very expensive prices, but their objective is basically this: Add Exclusion to WD
Little Stub
Chrome Bypass
And have the possibility of being attached to EMAIL.
And I confess, this really caught my attention and I decided to create my own project with these interesting ideas, and I'm here to share it with members who are interested in the subject, what do you think? I saw that it is little explored on HF ^^
Please feel free to provide constructive criticism and debate, after all, we are here to share!
Operation:
Choose your .exe
It will create a .REG that does the following
Booting a ps1 > Uac Bypass > added the C: exclusions > Reading the bytes of your .exe > executing.
If you have any ideas that you want to be implemented, you can send me a PM.✌
Using registry in any kind of way is heavily watched and if I am correct heavily sigged too. IF this was to be used in the wild it would be detected and probably patched insainly easily/quick too. Its alr tho.
(Oct 31, 2024 08:19 AM)Biggy_Asian Wrote: Using registry in any kind of way is heavily watched and if I am correct heavily sigged too. IF this was to be used in the wild it would be detected and probably patched insainly easily/quick too. Its alr tho.
I've been using this method for about 2 months, I recently came to explore for sale and if it is detected there are thousands of ways to get around it and if it is detected I will bring a quick update,It's just a matter of trying and seeing





 ~